Stored procedures only directly prevent SQL injection if you call them in a paramerized way. If you still have a string in your app with the procedure name and concatenate parameters from user input to that string in your code you'll have still have trouble.
How can SQL injection be prevented?
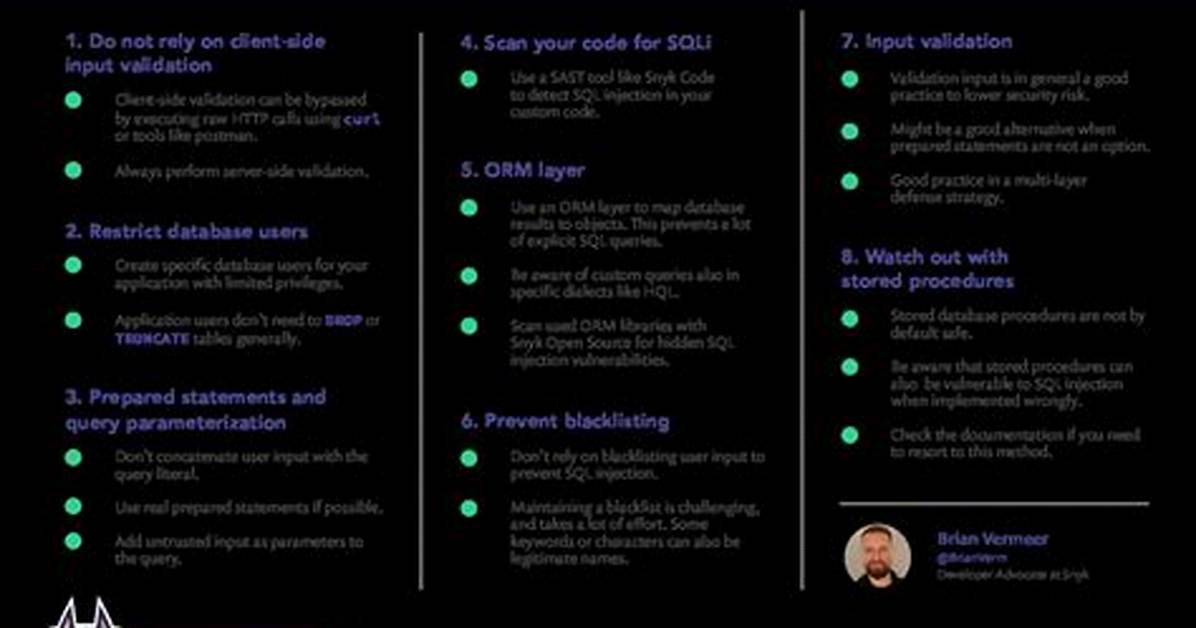
The only sure way to prevent SQL Injection attacks is input validation and parametrized queries including prepared statements. The application code should never use the input directly. ... In such cases, you can use a web application firewall to sanitize your input temporarily.
What is the best defense against SQL injection?
How to Prevent SQL Injection
- Use Stored Procedure, Not Dynamic SQL. Consider our earlier dynamic SQL example. ...
- Use Prepared Statements. ...
- Use Object Relational Mapping (ORM) Framework. ...
- Least Privilege. ...
- Input Validation. ...
- Character Escaping. ...
- Vulnerability Scanners. ...
- Use Web Application Firewall.

