What is Win32/Filecoder.JSWorm.A infection?
In this article you will certainly find concerning the definition of Win32/Filecoder.JSWorm.A as well as its unfavorable influence on your computer. Such ransomware are a type of malware that is clarified by online scams to demand paying the ransom money by a victim.
In the majority of the cases, Win32/Filecoder.JSWorm.A virus will certainly advise its targets to initiate funds move for the function of reducing the effects of the modifications that the Trojan infection has actually introduced to the target’s tool.
Win32/Filecoder.JSWorm.A Summary
These modifications can be as adheres to:
- A process created a hidden window;
- Uses Windows utilities for basic functionality;
- Attempts to stop active services;
- Attempts to repeatedly call a single API many times in order to delay analysis time. This significantly complicates the work of the virus analyzer. Typical malware tactics!
- Installs itself for autorun at Windows startup. There is simple tactic using the Windows startup folder located at:
C:\Users\[user-name]\AppData\Roaming\Microsoft\Windows\StartMenu\Programs\Startup. Shortcut links (.lnk extension) placed in this folder will cause Windows to launch the application each time [user-name] logs into Windows.The registry run keys perform the same action, and can be located in different locations:
- HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Run
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run
- HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\RunOnce
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\RunOnce
- Creates a copy of itself;
- Ciphering the records located on the sufferer’s hard disk — so the victim can no more use the information;
- Preventing regular accessibility to the victim’s workstation;
| z.whorecord.xyz | Trojan.Ransom.JSWorm |
| a.tomx.xyz | Trojan.Ransom.JSWorm |
Win32/Filecoder.JSWorm.A
The most typical networks whereby Win32/Filecoder.JSWorm.A Trojans are infused are:
- By means of phishing e-mails;
- As a consequence of user winding up on a source that hosts a malicious software program;
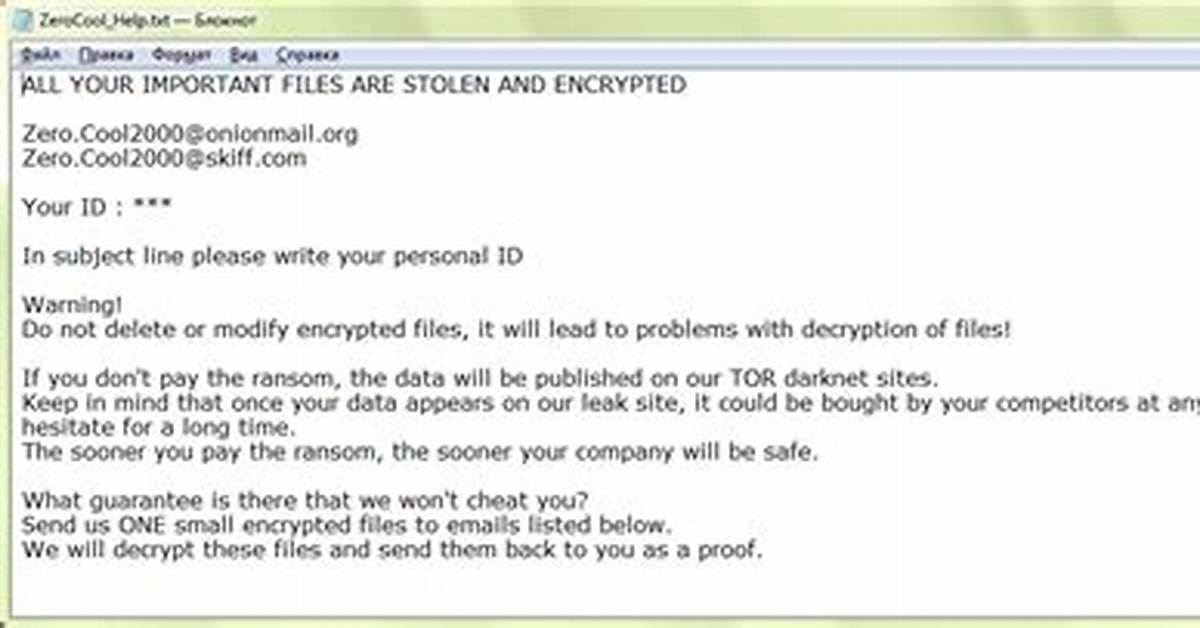
As quickly as the Trojan is effectively injected, it will certainly either cipher the information on the victim’s PC or protect against the tool from working in a correct manner – while likewise putting a ransom money note that discusses the need for the sufferers to impact the payment for the purpose of decrypting the documents or restoring the file system back to the preliminary condition. In many instances, the ransom note will show up when the customer reboots the COMPUTER after the system has currently been harmed.
Win32/Filecoder.JSWorm.A distribution channels.
In numerous corners of the globe, Win32/Filecoder.JSWorm.A expands by jumps and bounds. Nonetheless, the ransom money notes and techniques of obtaining the ransom money amount may differ depending upon particular local (local) setups. The ransom money notes as well as methods of extorting the ransom quantity may differ depending on particular regional (regional) setups.
For example:
Faulty informs about unlicensed software.
In specific areas, the Trojans typically wrongfully report having spotted some unlicensed applications enabled on the target’s device. The sharp then demands the individual to pay the ransom.
Faulty declarations concerning unlawful content.
In nations where software program piracy is much less prominent, this approach is not as efficient for the cyber scams. Additionally, the Win32/Filecoder.JSWorm.A popup alert might incorrectly assert to be deriving from a police establishment and also will certainly report having situated kid pornography or various other prohibited data on the device.
Win32/Filecoder.JSWorm.A popup alert may incorrectly assert to be deriving from a regulation enforcement establishment and also will report having situated youngster pornography or other illegal data on the tool. The alert will similarly contain a demand for the user to pay the ransom.
Technical details
File Info:
crc32: 358A342Cmd5: 6917163da452e8e47db8833af8617875name: 6917163DA452E8E47DB8833AF8617875.mlwsha1: d697e4a7f1ea1635e57ff8f05e09a1cc255fc0ffsha256: 1bf5a742be1c1319ed3646793efe6b909b80e077c5960ac3b1cebc9522498b77sha512: 3fe3410bcda7cda65cf4e0c581493a84bb8226b22b713944e34aa4a99827597b24459475c81ef7ff43934eedfb2c100fbde03e6bf261176c7cdbb33a7018d8f0ssdeep: 6144:vBpI7KUeB7VLJskfWpRF5m8ajXYOQV7D5iSVUPySZ0w18kH4ALXZR6AOzez+yEF:vBwKlVLaxfm7I5iSVUPySZ0KfXZR6Yztype: PE32 executable (GUI) Intel 80386, for MS WindowsVersion Info:
0: [No Data]
Win32/Filecoder.JSWorm.A also known as:
| GridinSoft | Trojan.Ransom.Gen |
| K7AntiVirus | Trojan ( 0054e6741 ) |
| Elastic | malicious (high confidence) |
| DrWeb | Trojan.Encoder.28634 |
| Cynet | Malicious () |
| ALYac | Trojan.Ransom.JSWorm |
| Cylance | Unsafe |
| Zillya | Trojan.Filecoder.Win32.9432 |
| Sangfor | Trojan.Win32.FileCoder.terpa |
| CrowdStrike | win/malicious_confidence_100% (W) |
| Alibaba | Trojan:Win32/DelShad.8afdce30 |
| K7GW | Trojan ( 0054e6741 ) |
| Cybereason | malicious.da452e |
| Symantec | ML.Attribute.HighConfidence |
| ESET-NOD32 | a variant of Win32/Filecoder.JSWorm.A |
| APEX | Malicious |
| Avast | Win32:Trojan-gen |
| Kaspersky | Trojan-Ransom.Win32.JSWorm.cc |
| BitDefender | DeepScan:Generic.Ransom.JSWORM.45C67EF2 |
| NANO-Antivirus | Trojan.Win32.DelShad.fqmjhh |
| MicroWorld-eScan | DeepScan:Generic.Ransom.JSWORM.45C67EF2 |
| Tencent | Win32.Trojan.Delshad.Wnml |
| Ad-Aware | DeepScan:Generic.Ransom.JSWORM.45C67EF2 |
| Comodo | Malware@#3gagsqmtdbfs8 |
| F-Secure | |
| BitDefenderTheta | Gen:NN.ZexaF.34722.wqW@aa1PHVe |
| VIPRE | Trojan.Win32.Generic!BT |
| TrendMicro | Ransom.Win32.JSWORM.SM |
| McAfee-GW-Edition | Trojan-FQZW!6917163DA452 |
| FireEye | Generic.mg.6917163da452e8e4 |
| Emsisoft | DeepScan:Generic.Ransom.JSWORM.45C67EF2 (B) |
| SentinelOne | Static AI – Malicious PE |
| Jiangmin | Trojan.DelShad.ap |
| Avira | HEUR/AGEN.1128004 |
| eGambit | Unsafe.AI_Score_99% |
| Antiy-AVL | Trojan/Generic.ASMalwS.2B9B856 |
| Microsoft | Ransom:Win32/Paradise.BC!MTB |
| Arcabit | DeepScan:Generic.Ransom.JSWORM.45C67EF2 |
| AegisLab | Trojan.Win32.DelShad.4!c |
| GData | Win32.Trojan-Ransom.Filecoder.CF@gen |
| AhnLab-V3 | Malware/Win32.Generic.C3253347 |
| McAfee | Trojan-FQZW!6917163DA452 |
| MAX | malware (ai score=99) |
| VBA32 | Trojan.DelShad |
| Malwarebytes | Ransom.JSWorm |
| Panda | Trj/GdSda.A |
| TrendMicro-HouseCall | Ransom.Win32.JSWORM.SM |
| Yandex | Trojan.GenAsa!amOcVnkWzS0 |
| Ikarus | Trojan-Ransom.FileCrypter |
| MaxSecure | Trojan.Malware.74319874.susgen |
| Fortinet | W32/Filecoder.NVV!tr.ransom |
| AVG | Win32:Trojan-gen |
| Paloalto | generic.ml |

