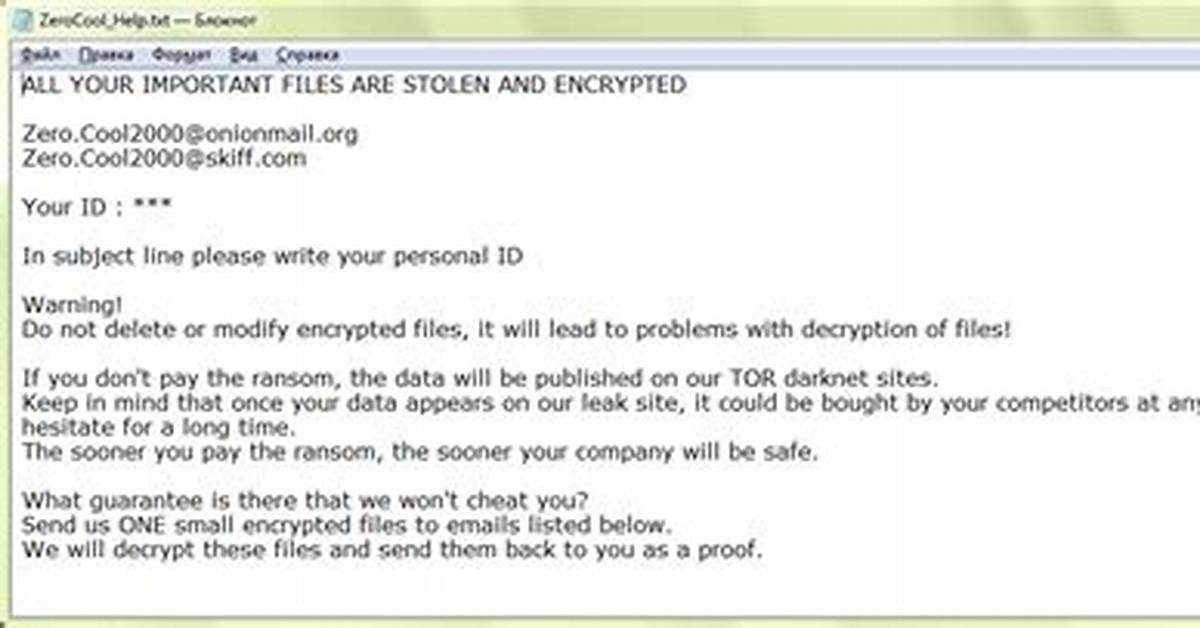
Win32/Filecoder.OIF detection is a malware detection you can spectate in your system. It generally appears after the preliminary procedures on your computer – opening the dubious email, clicking the advertisement in the Web or setting up the program from unreliable sources. From the instance it appears, you have a short time to act until it starts its malicious action. And be sure – it is far better not to wait for these destructive effects.
What is Win32/Filecoder.OIF virus?
Win32/Filecoder.OIF is ransomware-type malware. It looks for the files on your disks, ciphers it, and then asks you to pay the ransom for getting the decryption key. Besides making your files locked, this virus additionally does a ton of harm to your system. It alters the networking settings in order to avoid you from reading the removal manuals or downloading the antivirus. In rare cases, Win32/Filecoder.OIF can also prevent the launching of anti-malware programs.
Win32/Filecoder.OIF Summary
In total, Win32/Filecoder.OIF virus actions in the infected computer are next:
- Uses Windows utilities to enumerate running processes;
- Authenticode signature is invalid;
- Uses Windows utilities for basic functionality;
- Uses Windows utilities for basic functionality;
- Detects Bochs through the presence of a registry key;
- Checks the version of Bios, possibly for anti-virtualization;
- Checks the CPU name from registry, possibly for anti-virtualization;
- Collects information to fingerprint the system;
- Uses suspicious command line tools or Windows utilities;
- Encrypting the files located on the victim’s drive — so the victim cannot check these files;
- Blocking the launching of .exe files of anti-virus apps
- Blocking the launching of installation files of anti-malware programs
Ransomware has actually been a headache for the last 4 years. It is difficult to imagine a more harmful malware for both individuals and corporations. The algorithms utilized in Win32/Filecoder.OIF (generally, RHA-1028 or AES-256) are not hackable – with minor exclusions. To hack it with a brute force, you need a lot more time than our galaxy currently exists, and possibly will exist. However, that malware does not do all these unpleasant things without delay – it can take up to several hours to cipher all of your files. Hence, seeing the Win32/Filecoder.OIF detection is a clear signal that you need to begin the clearing process.
Where did I get the Win32/Filecoder.OIF?
Typical tactics of Win32/Filecoder.OIF distribution are standard for all other ransomware examples. Those are one-day landing web pages where users are offered to download and install the free program, so-called bait emails and hacktools. Bait e-mails are a relatively modern strategy in malware spreading – you get the e-mail that imitates some standard notifications about shippings or bank service conditions changes. Inside of the e-mail, there is an infected MS Office file, or a link which leads to the exploit landing page.
Malicious email message. This one tricks you to open the phishing website.
Avoiding it looks quite simple, but still requires tons of recognition. Malware can hide in different places, and it is better to stop it even before it goes into your computer than to depend on an anti-malware program. Basic cybersecurity knowledge is just an important item in the modern-day world, even if your relationship with a computer stays on YouTube videos. That may save you a lot of time and money which you would spend while seeking a solution.

