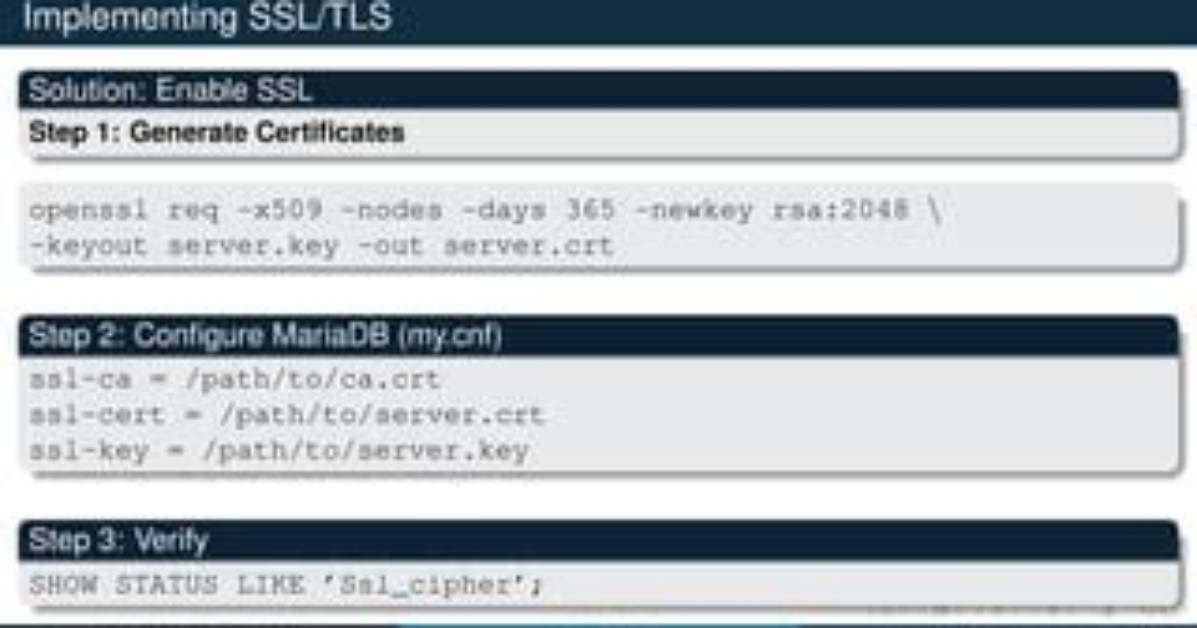
I have to make my MariaDB authentication a bit safer than default. I tried to set up SSL support for this, but found only an old howto here:
How to enable MySQL SSL on Ubuntu
I followed it, however after checking I get this:
MariaDB [(none)]> show variables like "%ssl%";
+---------------+----------------------------+
| Variable_name | Value                      |
+---------------+----------------------------+
| have_openssl  | NO                         |
| have_ssl      | DISABLED                   |
| ssl_ca        | /etc/mysql/ca-cert.pem     |
| ssl_capath    |                            |
| ssl_cert      | /etc/mysql/server-cert.pem |
| ssl_cipher    |                            |
| ssl_crl       |                            |
| ssl_crlpath   |                            |
| ssl_key       | /etc/mysql/server-key.pem  |
+---------------+----------------------------+
9 rows in set (0.00 sec)

MariaDB [(none)]> \s
...
SSL: not in use
...
This source was written in 2011. Maybe it is outdated, or I've made a mistake somewhere. When I generated .pems there were no errors. My /var/log/mysql/error.log file is empty.
Do you have any ideas?
2 Answers
To enable ssl within mariadb your version needs to be compiled with ssl (have_ssl | DISABLED) and you need to enable it within your mysql config:
# grep -Ri ssl /etc/mysql/my.cnf
ssl = true
ssl-ca = /etc/mysql/cacert.pem
ssl-cert = /etc/mysql/server-cert.pem
ssl-key = /etc/mysql/server-key.pem
after a restart or the mysql process ssl should be enabled.
sidenote
this answer from another question helped my getting rid of this error:
ERROR 2026 (HY000): SSL connection error: tlsv1 alert unknown ca
I created an Ubuntu 18.04.3 Certificate Authority. Verified everything about it. Root, Certificate, Key chain works.
MariaDB [(none)]>
MariaDB [(none)]>
MariaDB [(none)]>
MariaDB [(none)]> SHOW VARIABLES LIKE '%ssl%';
+---------------------+---------------------------------+
| Variable_name       | Value                           |
+---------------------+---------------------------------+
| have_openssl        | YES                             |
| have_ssl            | YES                             |
| ssl_ca              | /etc/mysql/ssl/ca-cert.pem      |
| ssl_capath          |                                 |
| ssl_cert            | /etc/mysql/ssl/mariadb-cert.pem |
| ssl_cipher          | DHE-RSA-AES256-SHA              |
| ssl_crl             |                                 |
| ssl_crlpath         |                                 |
| ssl_key             | /etc/mysql/ssl/mariadb-key.pem  |
| version_ssl_library | OpenSSL 1.1.1c  28 May 2019     |
+---------------------+---------------------------------+

mysql  Ver 15.1 Distrib 10.4.8-MariaDB, for debian-linux-gnu (x86_64) using readline 5.2

Connection id:          37
Current database:
Current user:           sa@localhost
SSL:                    Not in use
Current pager:          stdout
Using outfile:          ''
Using delimiter:        ;
Server:                 MariaDB
Server version:         10.4.8-MariaDB-1:10.4.8+maria~bionic mariadb.org binary distribution
Protocol version:       10
Connection:             Localhost via UNIX socket
Server characterset:    latin1
Db     characterset:    latin1
Client characterset:    utf8
Conn.  characterset:    utf8
UNIX socket:            /var/run/mysqld/mysqld.sock
Uptime:                 19 hours 5 min 57 sec

Threads: 7  Questions: 66  Slow queries: 0  Opens: 31  Flush tables: 1  Open tables: 25  Queries per second avg: 0.000
--------------

MariaDB [(none)]>
I followed the process online for the CA and creating the MariaDB SSL keys.
I did the my.cnf to get the keys to show up above. /etc/mysql/mariadb.cnf has the keys in it. I have the Mariadb repository installed for the updates.
Here is my.cnf:
[mysqld]
ssl = true
ssl-ca          = /etc/mysql/ssl/ca-cert.pem
ssl-cert         = /etc/mysql/ssl/mariadb-cert.pem
ssl-key          = /etc/mysql/ssl/mariadb-key.pem
log_error=/var/log/mysql/mysql_error.log
ssl-cipher=DHE-RSA-AES256-SHA


grep -Ri ssl /etc/mysql/my.cnf
ssl = true
ssl-ca          = /etc/mysql/ssl/ca-cert.pem
ssl-cert         = /etc/mysql/ssl/mariadb-cert.pem
ssl-key          = /etc/mysql/ssl/mariadb-key.pem
ssl-cipher=DHE-RSA-AES256-SHA

ssl-cipher entry can be removed.

