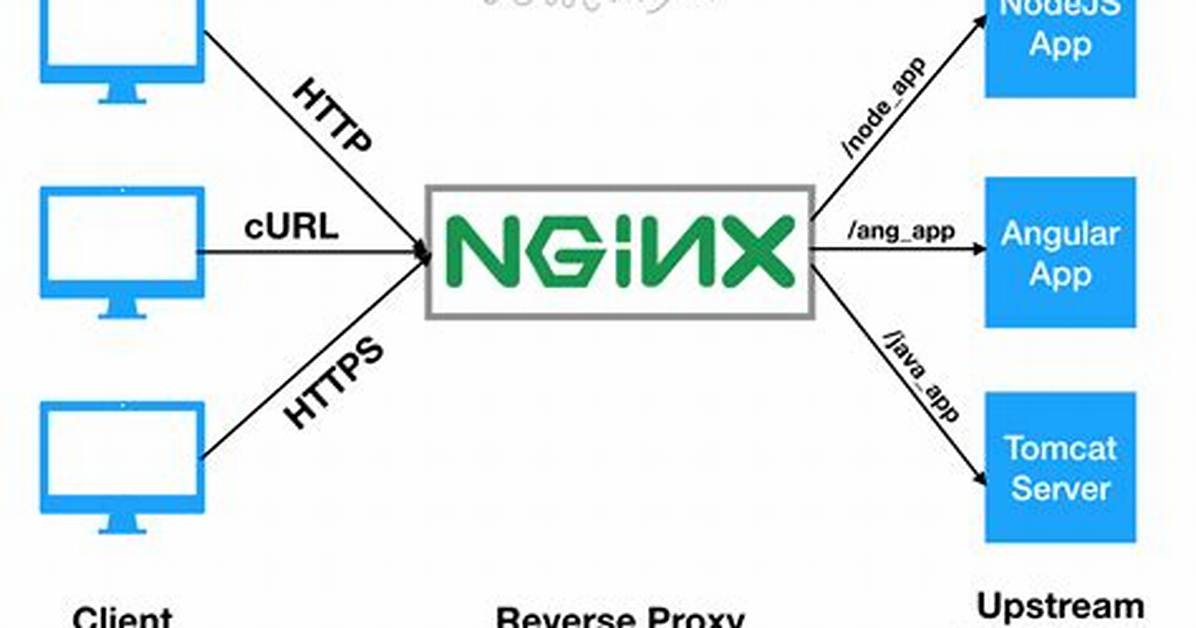
Follow up of a previous question of mine.
What I want to do?
I want to have my reverse proxy [NGINX] to redirect incoming webtraffic (HTTP and HTTPS) to the correct server based on the sub-domain.
The traffic towards the reverseproxy (RP) from the internet should be with HTTPS while inside my network I don't mind http traffic.
What is my current situation?
I got my webservices running, as of now only 2, iRedMail and Kanboard. Both can be reached via http without a problem. I was able to share my wildcard certificate from my RP with my other servers (I learned later, this isn't necessary).
However, when I try to reach my Servers domain-name via https over Firefox I get PR_END_OF_FILE_ERROR and via Chrome ERR:CONNECTION_CLOSED. In this case it doesn't matter if I try to reach the webserver on the RP itself or the other 2.
Meaning I understood the NGINX with http proxy but failed when it came to certificates and https proxy.
For my configurations please check out the following pastebins, I don't want this post to be to long. All pasts will be available for 6 Months, and I will edit this post to add my failed configuration, if there is any.
And finally the output of logs I thought about:
 (Reverse-Proxy)> sudo nano /var/log/nginx/error.log
2020/02/21 07:07:46 [error] 9213#9213: *1 no "ssl_certificate" is defined in server listening on SSL port while SSL handshaking, client: XXX.XXX.XXX.XXX, server: 0.0.0.0:443
2020/02/21 07:08:27 [error] 9213#9213: *2 no "ssl_certificate" is defined in server listening on SSL port while SSL handshaking, client: XXX.XXX.XXX.XXX, server: 0.0.0.0:443
2020/02/21 07:11:46 [error] 9320#9320: *1 no "ssl_certificate" is defined in server listening on SSL port while SSL handshaking, client: XXX.XXX.XXX.XXX, server: 0.0.0.0:443
2020/02/21 07:12:03 [error] 9320#9320: *2 open() "/usr/share/nginx/html/favicon.ico" failed (2: No such file or directory), client: XXX.XXX.XXX.XXX, server:  request: "GET /favic$
2020/02/21 07:12:07 [error] 9320#9320: *3 no "ssl_certificate" is defined in server listening on SSL port while SSL handshaking, client: XXX.XXX.XXX.XXX, server: 0.0.0.0:443
2020/02/21 07:23:12 [error] 9320#9320: *4 no "ssl_certificate" is defined in server listening on SSL port while SSL handshaking, client: XXX.XXX.XXX.XXX, server: 0.0.0.0:443
2020/02/21 07:23:12 [error] 9320#9320: *5 no "ssl_certificate" is defined in server listening on SSL port while SSL handshaking, client: XXX.XXX.XXX.XXX, server: 0.0.0.0:443
2020/02/21 07:23:17 [error] 9320#9320: *6 no "ssl_certificate" is defined in server listening on SSL port while SSL handshaking, client: XXX.XXX.XXX.XXX, server: 0.0.0.0:443
2020/02/21 07:23:47 [error] 9320#9320: *7 no "ssl_certificate" is defined in server listening on SSL port while SSL handshaking, client: XXX.XXX.XXX.XXX, server: 0.0.0.0:443
2020/02/21 07:24:47 [error] 9320#9320: *8 no "ssl_certificate" is defined in server listening on SSL port while SSL handshaking, client: XXX.XXX.XXX.XXX, server: 0.0.0.0:443
2020/02/21 07:29:47 [error] 9320#9320: *10 no "ssl_certificate" is defined in server listening on SSL port while SSL handshaking, client: XXX.XXX.XXX.XXX, server: 0.0.0.0:443
2020/02/21 07:39:48 [error] 9320#9320: *11 no "ssl_certificate" is defined in server listening on SSL port while SSL handshaking, client: XXX.XXX.XXX.XXX, server: 0.0.0.0:443
2020/02/21 07:53:21 [error] 9320#9320: *12 no "ssl_certificate" is defined in server listening on SSL port while SSL handshaking, client: XXX.XXX.XXX.XXX, server: 0.0.0.0:443
I tried this from 7 am to 9 am, but the log stopped with errors around 8 am. I also checked the logs of the Kanboard server, but nothing was reported, neither for access nor error.

