I am using keycloak as an identity broker to a simplesamlphp identity provider in order to login to an angular application.
The keycloak redirects correctly to the identity provider with the login mask. After the login the identity provider redirects as expected to keycloak. Unfortunately I get the following error message (as JSON):
{"error":"invalid_request","error_description":"Missing parameter: username"}
My IdP has a user, my keycloak does not, since I do not want to store the users additionally in keycloak.
My broker configuration looks like this:
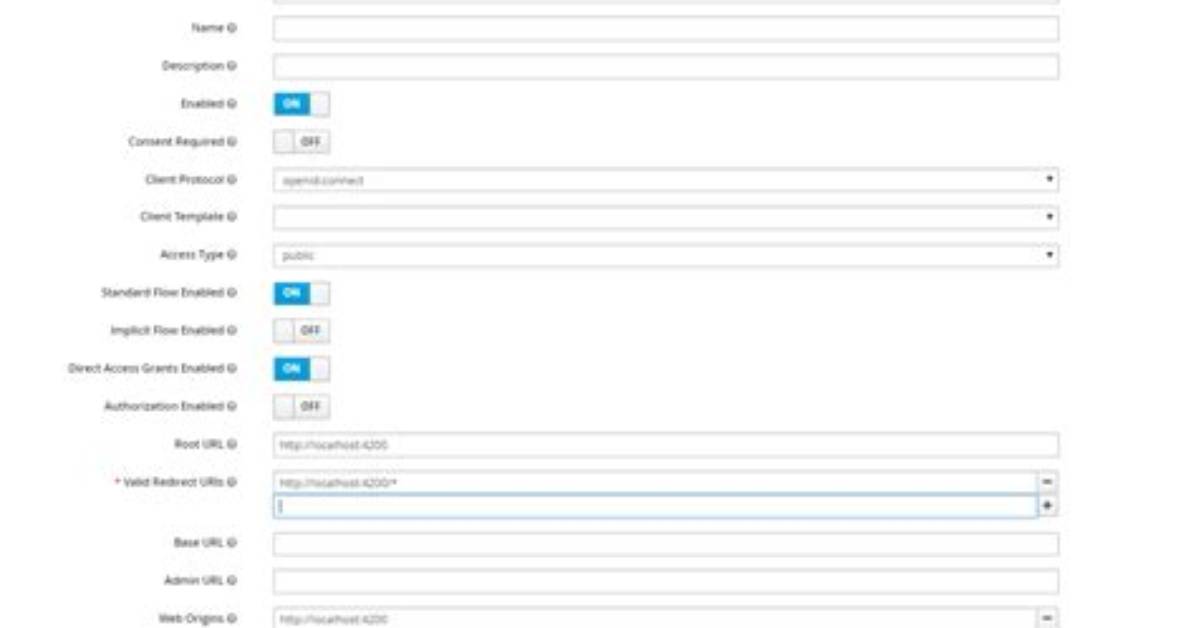
My client configuration is this:
I am familiar with neither SAML nor Keycloak, so if I need to provide any other information, please tell me.
1 Answer
Ok, I managed to solve this issue. Here's how:
Apparently, for now KC always stores authenticated users locally. There is a feature request for the NO IMPORT option, but it has been deferred. See here: KEYCLOAK-4429
So, basically, you just let KC create a local user and link the brokered account to the newly created user automatically. To do so, you create an Authentication Flow with these two steps as seen here: Auth Flow Do note, however, that the the autolink execution is only available since KC 3.5, so a JBOSS SSO 7.2 (based on KC 3.4) will likely not support this.
You then use this flow in your Identity Provider configuration as the First Login Flow.
Next time, when logging in via the external IdP, KC will create a new user and link it to the one used in the in the external IdP. The created user will then be used with your client.
Two more things:
- You can configure Mappers with your Identity Provider to automatically import attributes from the assertion claims directly to the newly created KC user. You can then configure Mappers with your client to pass these attributes along as additional claims (in my case I needed an UID attributed obtained via SAML).
- You can configure User Federation in your realm e.g. by adding an LDAP connection, in which case, KC will not only create a default new user, but will correctly auto-import said user via LDAP and then link it with your IdP user.

