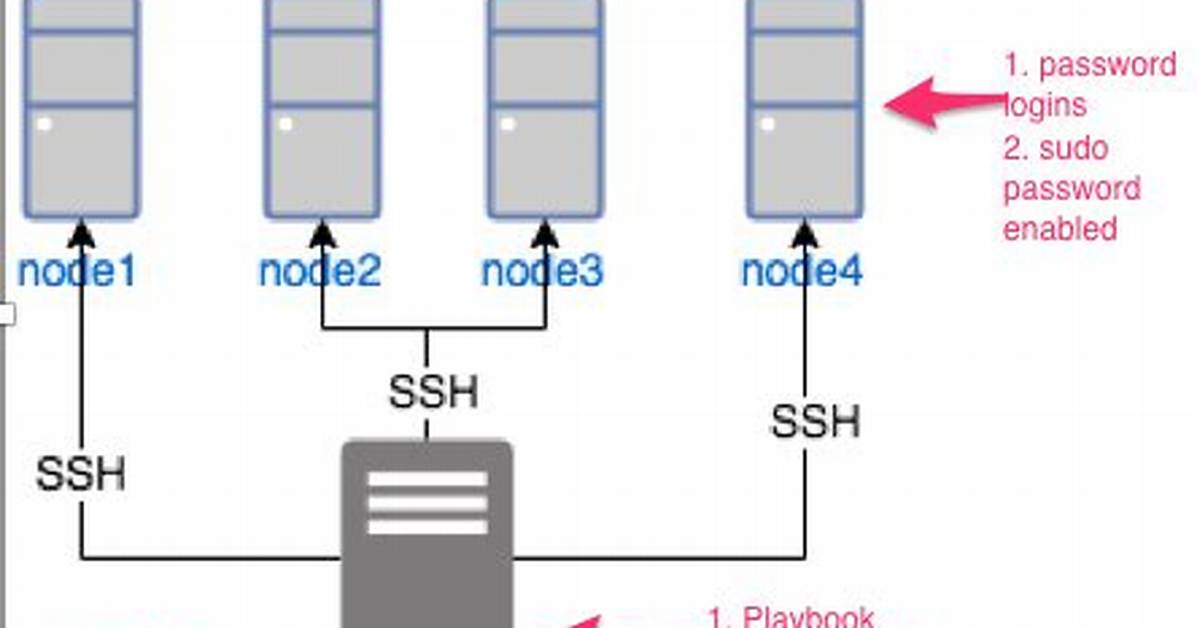
I want to run ansible with user sa1 without sudo password:
First time OK:
[root@centos1 cp]# ansible cent2 -m shell -a "sudo yum -y install httpd"

cent2 | SUCCESS | rc=0 >>
Second time FAILED:
[root@centos1 cp]# ansible cent2 -s -m yum -a "name=httpd state=absent"

cent2 | FAILED! => {
    "changed": false,
    "failed": true,
    "module_stderr": "",
    "module_stdout": "sudo: a password is required\r\n",
    "msg": "MODULE FAILURE",
    "parsed": false
}
Please help!
3 Answers
It's not ansible it's your server's configuration. Make sure that sudo is allowed for the user ansible is using without password.
- To do that login to the server
- Open the sudoers file with
sudo visudo - Make sure you have a line something like this:
centos ALL=(ALL) NOPASSWD:ALL - Replace
centoswith the your user - Save the file
You can try from the server itself by running:
sudo -u [yourusername] sudo echo "success"
If this works it should work from ansible too.
By default ansible runs sudo with the flags: -H -S -n to become root. Where --non-interactive would be the corresponding long form for option -n. This option seems to make sudo return the error message, without attempting to let the authentication modules do their thing.
I managed to get around the password error by creating a ~/.ansible.cfg containing lines as below, for the most relevant ansible version.
ansible 2.4
[defaults]
sudo_flags = --set-home --stdin
ansible 2.9
[sudo_become_plugin]
flags = -H -S
That was at least enough to allow pam_ssh_agent_auth.so to run and authenticate me.
Prior to version 2.8 the above example works, newer than 2.8 requires the second example. Documentation for the new style configuration can be found in the Ansible User Guide.
Here's the playbook in case you want ansible make it for you
- Add user to chosen group ( in my case
wheel) - Add this to your playbook
- name: Make users passwordless for sudo in group wheel
  lineinfile:
    path: /etc/sudoers
    state: present
    regexp: '^%wheel'
    line: '%wheel ALL=(ALL) NOPASSWD: ALL'
    validate: 'visudo -cf %s'

