What's the difference in context of web applications? I see the abbreviation "auth" a lot. Does it stand for auth-entication or auth-orization? Or is it both?
17 Answers
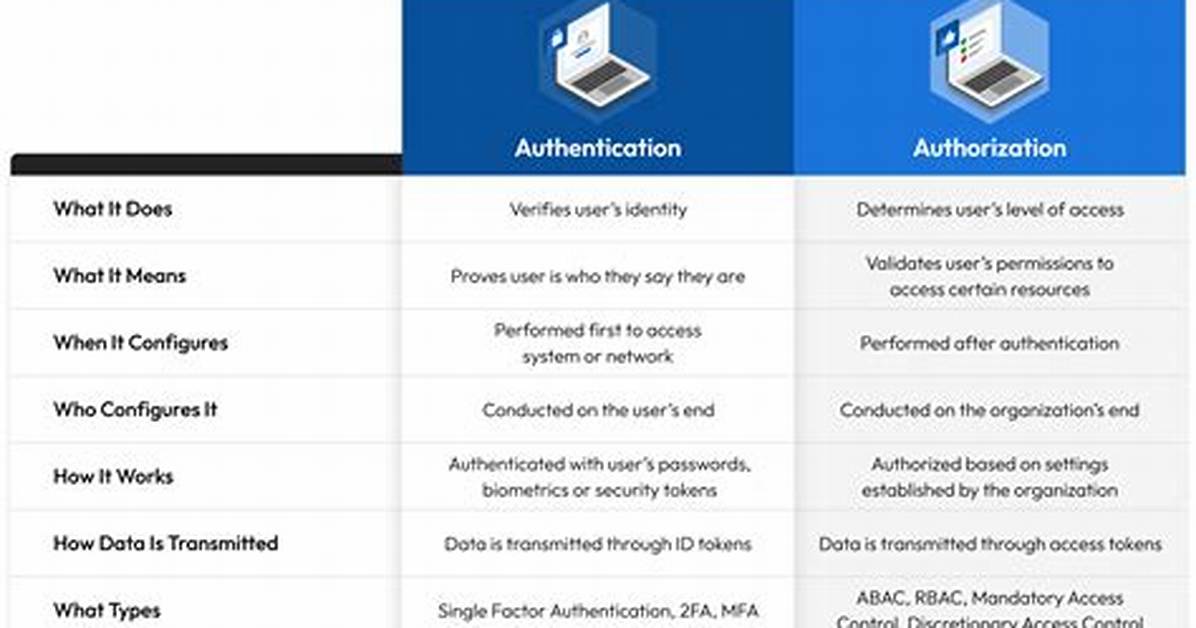
Authentication is the process of ascertaining that somebody really is who they claim to be.
Authorization refers to rules that determine who is allowed to do what. E.g. Adam may be authorized to create and delete databases, while Usama is only authorised to read.
The two concepts are completely orthogonal and independent, but both are central to security design, and the failure to get either one correct opens up the avenue to compromise.
In terms of web apps, very crudely speaking, authentication is when you check login credentials to see if you recognize a user as logged in, and authorization is when you look up in your access control whether you allow the user to view, edit, delete or create content.
In short, please. :-)
Authentication = login + password (who you are)
Authorization = permissions (what you are allowed to do)
Short "auth" is most likely to refer either to the first one or to both.
As Authentication vs Authorization puts it:
Authentication is the mechanism whereby systems may securely identify their users. Authentication systems provide an answers to the questions:
- Who is the user?
- Is the user really who he/she represents himself to be?
Authorization, by contrast, is the mechanism by which a system determines what level of access a particular authenticated user should have to secured resources controlled by the system. For example, a database management system might be designed so as to provide certain specified individuals with the ability to retrieve information from a database but not the ability to change data stored in the datbase, while giving other individuals the ability to change data. Authorization systems provide answers to the questions:
- Is user X authorized to access resource R?
- Is user X authorized to perform operation P?
- Is user X authorized to perform operation P on resource R?
See also:
- Authentication vs. authorization on Wikipedia
In User Context:
Authentication = Verifying the User is who he claims to be (you can technically verify a lot of different things like password, tax info, social security info, driver's license, fingerprints, or other biometrics ... but usually a username/password is sufficient)
Authorization = Permitting the User to do something (you can set up roles ['admin', 'seller', 'buyer'...] with permissions ['access control center', 'delete products'...] and give those roles to the users, then validate the user has a role that permits him to do an action)
Permissions have a direct relationship with CRUD operations, so if building a UI, you can list objects as rows, and checkboxes in 4 columns for Create, Read, Update, Delete of that object permission for any given role.
Like in my example above 'access control center' is a full Create, Read, Update, and Delete access of the control center object, while 'delete products' is Delete access for the products object.
Note: HTTP Authorization Header was intended as permission to access a resource, but really is used as an authentication for all resource access.
It is easier in my head and in my code to think of verification and permissions because the two words
- don't sound alike
- don't have the same abbreviation
- and actual implementation of authorization typically involves implementing Roles and Permissions
Authentication is verification and Authorization is checking permission(s). Auth can mean either, but is used more often as "User Auth" i.e. "User Authentication". A lot of times there is no explicit authorization implementation (roles and permissions), just the authentication is used to provide the authorization to do every available action. And so that is Auth.
The confusion is understandable, since the two words sound similar, and since the concepts are often closely related and used together. Also, as mentioned, the commonly used abbreviation Auth doesn't help.
Others have already described well what authentication and authorization mean. Here's a simple rule to help keep the two clearly apart:
- Authentication validates your Identity (or authenticity, if you prefer that)
- Authorization validates your authority, i.e. your right to access and possibly change something.
I have tried to create an image to explain this in the most simple words
1) Authentication means "Are you who you say you are?"
2) Authorization means "Should you be able to do what you are trying to do?".
This is also described in the image below.
I have tried to explain it in the best terms possible, and created an image of the same.
Authentication is the process of verifying the proclaimed identity.
- e.g. username/password
Usually followed by authorization, which is the approval that you can do this and that.
- e.g. permissions
Adding to @Kerrek's answer;
Authentication is Generalized form (All employees can login in to the machine )
Authorization is Specialized form (But admin only can install/uninstall the application in Machine)
Authentication is the process of verifying your log in username and password.
Authorization is the process of verifying that you can access to something.
Definitions
Authentication - Are you the person you claim to be?
Authorization - Are you authorized to do whatever it is you're trying to do?

