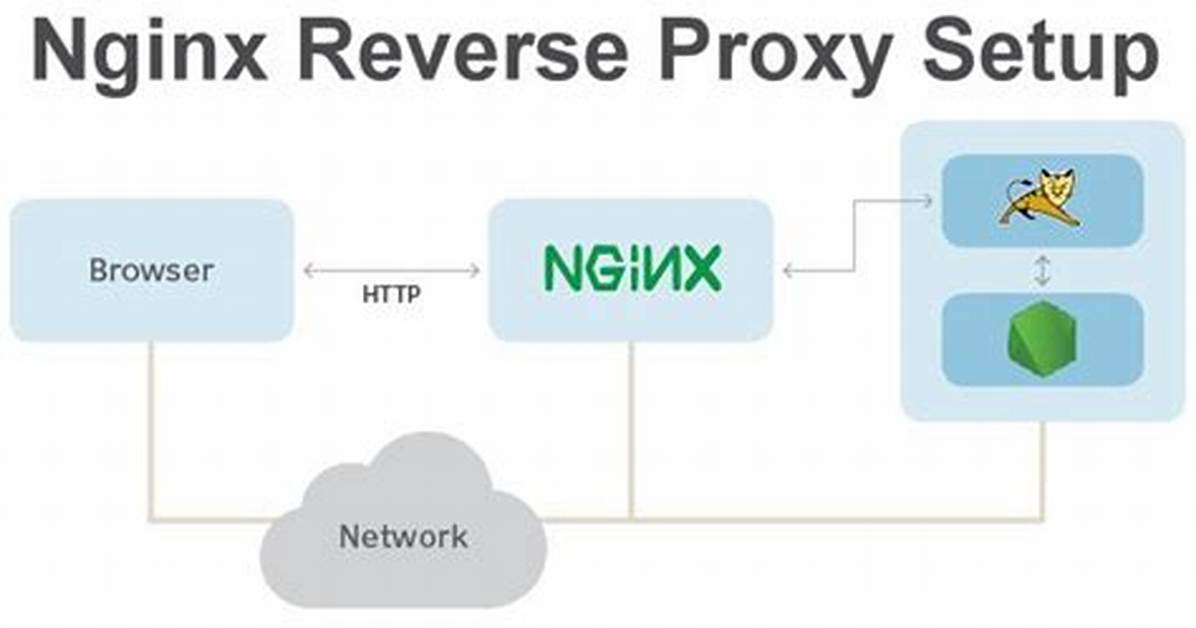
we have:
Ubuntu 16.04
nginx 1.10.3
i am new to nginx and need help on proxy_pass to https.
We have clients in internet they call a url for example.
i want to pass this traffic to my server with the ip address 192.168.0.10. On this server i have ssl enabled listen port 9443.
We want use nginx as reverse_proxy. My nginx config looks like.
server {
  listen 443;
  servername testapp.mobios.example.com;

  location / {
    proxy_pass
}
}
If the clients try to contact the ssl server with they get nothing.
What i need is just pass https to https. Is SNI a problem here?
Any idea? Please help ayyoladi
3 Answers
Not directly same but similar question brought me here.
Load balancing to HTTPS:
Client <- HTTPS -> (decrypt) Load balancer (encrypt) <- HTTPS -> Server
Generally thisisayush answer () is very good and it partially solves my problem but adding load balancing makes it a bit more difficult to google.
When you make upstream list you must remember about adding a 443 port.
NOT WORKING:
upstream myapp2 {
  server 10.0.1.1;
}
WORKING:
upstream myapp2 {
  server 10.0.1.1:443;
}
Even if you use in location https protocol (which I expected to point by default to 443):
location / {
  proxy_pass
}
Full example:
http {
  upstream myapp2 {
    server 10.0.1.1:443;
  }

  server {
    listen 443;

    ssl_certificate     /etc/nginx/cert.crt;
    ssl_certificate_key /etc/nginx/cert.key;

    ssl on;

    location / {
      proxy_pass
    }
  }
}
Answer is based on documentation which I eventually found with help of thisisayush comment:
server {
    listen 80;
    server_name website.domain.com;
    return 301
}

server {
        listen 443 ssl;
        listen [::]:443 ssl;
        server_name website.domain.com;

       #Size archive        client_max_body_size 50M;

        ssl_certificate          /etc/letsencrypt/live/mydomain/fullchain.pem;
        ssl_certificate_key      /etc/letsencrypt/live/mydomain/privkey.pem;
        ssl_trusted_certificate  /etc/letsencrypt/live/mydomain/chain.pem;

       location / {
               proxy_set_header   X-Forwarded-For $remote_addr;
               proxy_set_header   Host $http_host;
   1   ===>    proxy_pass
[ OR ]
   2   ===>    proxy_pass
       }

}
I did this once for my client. What you do is enable and install SSL in Nginx rather than to the server being proxied.

