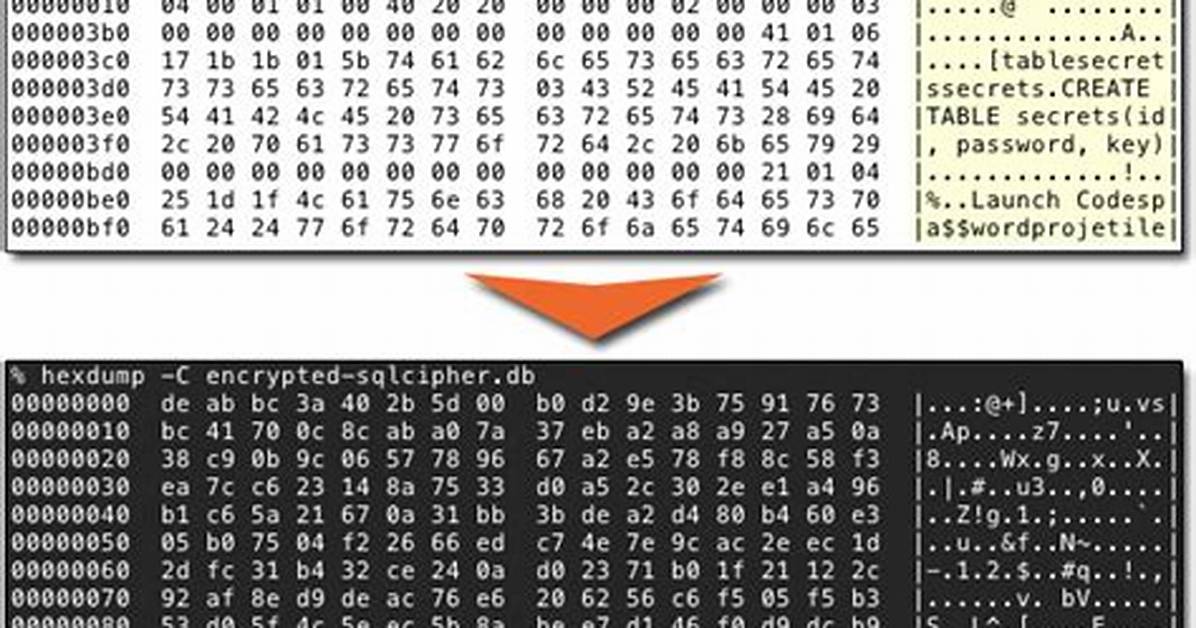
The question is simple
What I have is:
- I have a database file which is encrypted using sqlcipher.
- I also have the passphrase which was used to encrypt this db file
What I need is:
- I need to decrypt the database file/ need a database file which is unencrypted/non encrypted/decrypted.
4 Answers
Download and Build sqlcipher
--Skip this if sqlcipher is already installed
Pull the code from in a directory (say ~/sqlcipher)mkdir ~/bld; # Build will occur in a sibling directory
cd ~/bld; # Change to the build directory
../sqlcipher/configure --enable-tempstore=yes CFLAGS="-DSQLITE_HAS_CODEC" LDFLAGS="-lcrypto";
#configure sqlcipher
make install; # Install the build products
Decrypt the database to a plaintext database
$ cd ~/;
$ ./sqlcipher encrypted.db
sqlite> PRAGMA key = 'testkey';
sqlite> ATTACH DATABASE 'plaintext.db' AS plaintext KEY '';  -- empty key will disable encryption
sqlite> SELECT sqlcipher_export('plaintext');
sqlite> DETACH DATABASE plaintext;
Find the decrypted database at ~/plaintext.db which you can use with any sqlite browser like this.
Update : September 2015
now supports sqlcipher databases. That's neat.
Use SQliteStudio
Select SQLiteCipher and enter the password. The database will be opened.
This shell script will decrypt a SQLCipher database called mydb.db and create one called mydb-decrypt.db. Params are $1=key, $2, path to read & write from.
#!/bin/bash
echo "Decrypting $2 using key $1"
echo "PRAGMA key='$1';select count(*) from sqlite_master;ATTACH DATABASE '$2/mydb-decrypt.db' AS plaintext KEY '';SELECT sqlcipher_export('plaintext');DETACH DATABASE plaintext;" | sqlcipher $2/mydb.db
echo "Done."
If you wanted to do this in a single command line, the guts of this are:
echo "PRAGMA key='$1';select count(*) from sqlite_master;ATTACH DATABASE '$2/mydb-decrypt.db' AS plaintext KEY '';SELECT sqlcipher_export('plaintext');DETACH DATABASE plaintext;" | sqlcipher $2/mydb.db
Building on the previous answers , I have a comprehensive answer. I have the configuration- OS X version - 10.10.4 Steps : 1. Donwload and build OpenSSL code:
$ curl -o openssl-1.0.0e.tar.gz
$ tar xzf openssl-1.0.0e.tar.gz
$ cd openssl-1.0.0e
$ ./Configure darwin64-x86_64-cc
$ make
- Download and build SQLCipher code.
In another directory,
$ git clone
$ cd sqlcipher
Change '/path/to/libcrypto.a' in the following command to your path
$ ./configure --enable-tempstore=yes CFLAGS="-DSQLITE_HAS_CODEC" LDFLAGS="/path/to/libcrypto.a"
$ make
Decrypt to plaintext database (As illustrated in previous post by Vinay)
$ cd ~/;
$ ./sqlcipher encrypted.db
sqlite> PRAGMA key = 'testkey';
sqlite> ATTACH DATABASE 'plaintext.db' AS plaintext KEY '';  -- empty key will disable encryption
sqlite> SELECT sqlcipher_export('plaintext');
sqlite> DETACH DATABASE plaintext;
Tis should help you decrypt the encrypted file...

