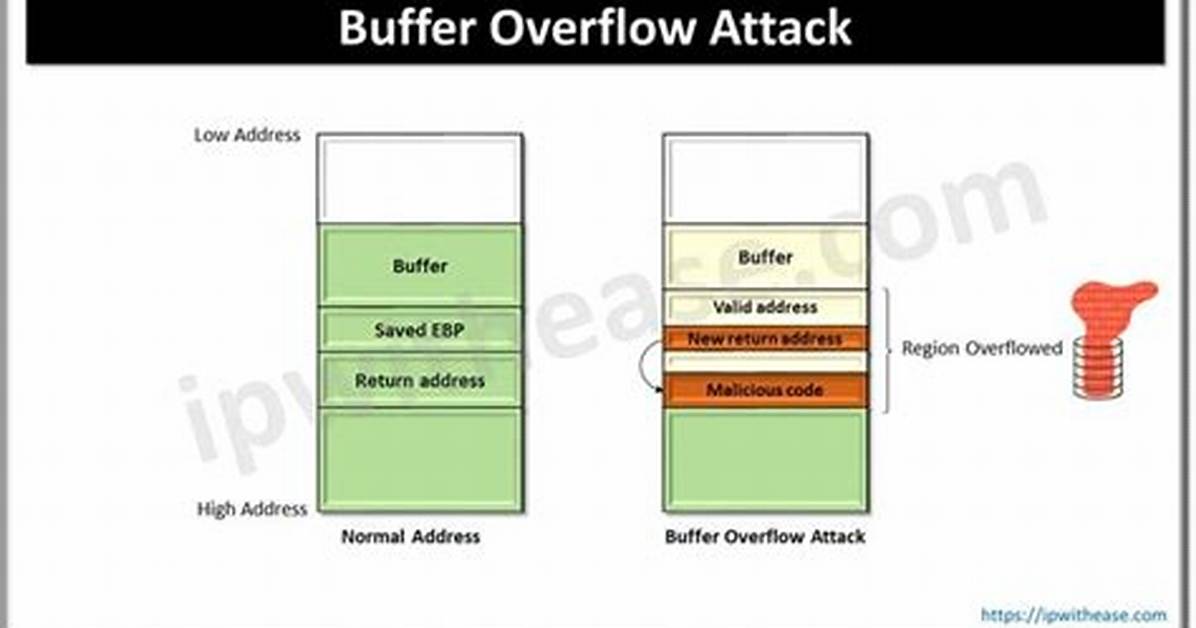
A buffer overflow occurs when data written to a buffer also corrupts data values in memory addresses adjacent to the destination buffer due to insufficient A range check is a check to make sure a number is within a certain range; for example, to ensure that a value about to be assigned to a 16-bit integer is within the capacity of a 16-bit integer (i.e. checking against wrap-around).
What causes a buffer overflow?
A buffer overflow (or buffer overrun) occurs when the volume of data exceeds the storage capacity of the memory buffer. ... Buffer overflows can affect all types of software. They typically result from malformed inputs or failure to allocate enough space for the buffer.
Why do buffer overflow vulnerabilities exist?
A buffer overflow vulnerability occurs when you give a program too much data. The excess data corrupts nearby space in memory and may alter other data. As a result, the program might report an error or behave differently. Such vulnerabilities are also called buffer overrun.

