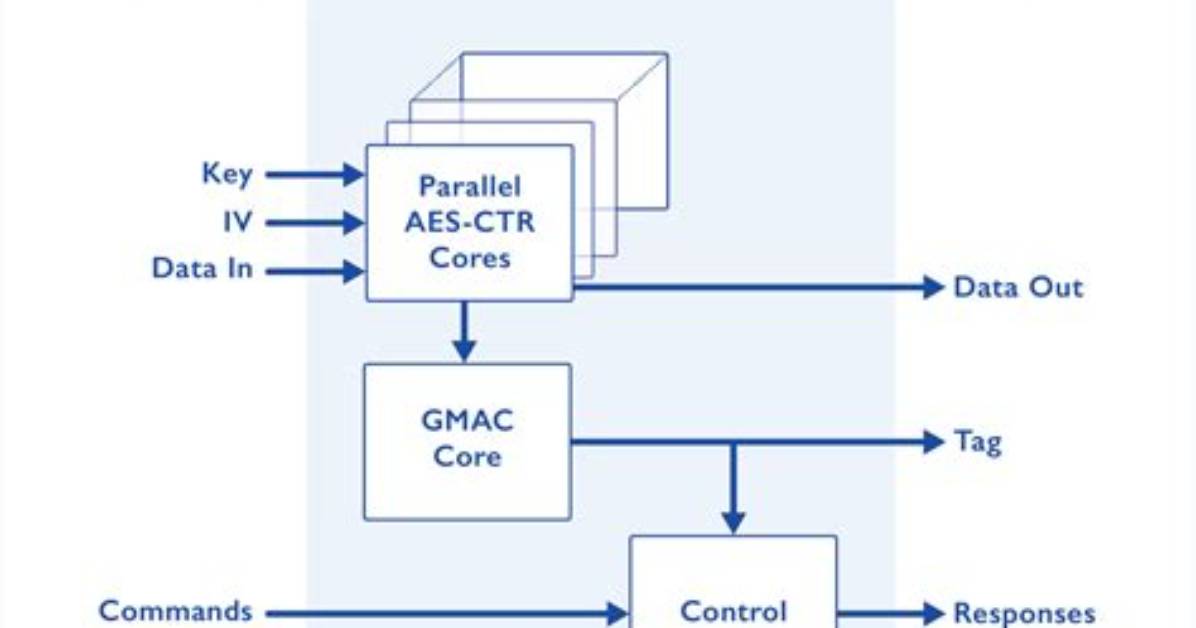
TL;DR: Padding is part of the specification of the mode and thus doesn't need to be done by the user of the primitive. Internally GCM really is CTR mode along with a polynomial hashing function applied on the ciphertext.
Does AES use padding?
[Back] Padding is used in a block cipher where we fill up the blocks with padding bytes. AES uses 128-bits (16 bytes), and DES uses 64-bit blocks (8 bytes). The main padding methods are: ... This pads with 0x80 (10000000) followed by zero (null) bytes.
How secure is AES GCM?
As for GCM, it's basically GCM = CTR + Authentication (not CBC). It's fast and secure if used correctly, and very versatile, hence its popularity. CBC is older, which means more compatibility and just overall historical reasons. There are performance advantages, if you don't need GCM for authenticity.

