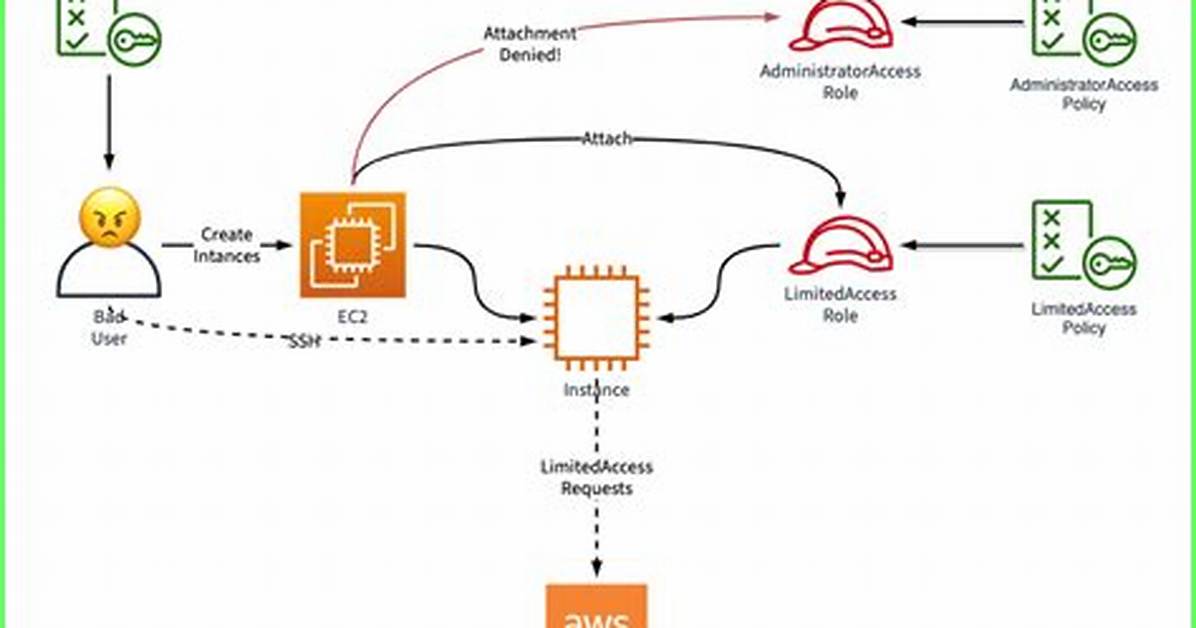
PassRole is a permission granted to IAM Users and resources that permits them to use an IAM Role. For example, imagine that there is an IAM Role called Administrators. This role has powerful permissions that should not be given to most users.
Is not Authorised to perform IAM PassRole?
If you receive an error that you’re not authorized to perform the iam:PassRole action, then you must contact your administrator for assistance. Your administrator is the person that provided you with your user name and password. Ask that person to update your policies to allow you to pass a role to Resource Groups.
What is IAM permission in AWS?
Permissions let you specify access to AWS resources. Permissions are granted to IAM entities (users, groups, and roles) and by default these entities start with no permissions. In other words, IAM entities can do nothing in AWS until you grant them your desired permissions.
How do I assume AWS role?
To assume a role from a different account, your AWS account must be trusted by the role. The trust relationship is defined in the role’s trust policy when the role is created. That trust policy states which accounts are allowed to delegate that access to users in the account.
What is Createservicelinkedrole?
PDF. Creates an IAM role that is linked to a specific AWS service. The service controls the attached policies and when the role can be deleted. This helps ensure that the service is not broken by an unexpectedly changed or deleted role, which could put your AWS resources into an unknown state.
What is the difference between an IAM role and an IAM user?
An IAM user has permanent long-term credentials and is used to directly interact with AWS services. An IAM role does not have any credentials and cannot make direct requests to AWS services. IAM roles are meant to be assumed by authorized entities, such as IAM users, applications, or an AWS service such as EC2.
Which IAM policy provides full access to resources?
The policy of Power User provides full access to all of the resources in IAM.
What is temporary security credentials?
Temporary security credentials are short-term, as the name implies. They can be configured to last for anywhere from a few minutes to several hours. After the credentials expire, AWS no longer recognizes them or allows any kind of access from API requests made with them.
What is IAM role and policy?
An IAM role is both an identity and a resource that supports resource-based policies. For that reason, you must attach both a trust policy and an identity-based policy to an IAM role. Trust policies define which principal entities (accounts, users, roles, and federated users) can assume the role.
Is IAM free in AWS?
Free to use
AWS Identity and Access Management (IAM) and AWS Security Token Service (AWS STS) are features of your AWS account offered at no additional charge. You are charged only when you access other AWS services using your IAM users or AWS STS temporary security credentials.
Why do we need IAM?
It helps protect against compromised user credentials and easily cracked passwords that are common network entry points for criminal hackers who want to plant ransomware or steal data. Done well, IAM helps ensure business productivity and frictionless functioning of digital systems.
Who can assume IAM role?
Because this IAM role is assumed by an IAM user, you must specify a principal that allows IAM users to assume that role. For example, a principal similar to arn:aws:iam::123456789012:root allows all IAM identities of the account to assume that role.
Do IAM roles expire?
Once you increase the maximum session duration, users and applications assuming the IAM role can request temporary, short-term credentials that expire when the IAM role session expires.
How do I create an IAM in AWS?
Creating a role
Sign into the AWS Management Console as an administrator of Account A.Navigate to the IAM console.In the navigation pane, choose Roles.Choose Create New Role.Type a name for the new role, and then choose Next Step.Choose Role for Cross-Account Access.
What is AWSServiceRoleForECS?
Amazon ECS uses the service-linked role named AWSServiceRoleForECS to enable Amazon ECS to call AWS APIs on your behalf. The AWSServiceRoleForECS service-linked role trusts the ecs.amazonaws.com service principal to assume the role.
How do I remove Awsserviceroleforsupport?
AWS Support Service Linked Role (SLR) cannot be deleted since it is necessary for providing administrative, operational and technical support for your AWS account.
What is AWS role path?
The path variable in IAM is used for grouping related users and groups in a unique namespace, usually for organizational purposes. From Friendly Names and Paths: If you are using the IAM API or AWS Command Line Interface (AWS CLI) to create IAM entities, you can also give the entity an optional path.

