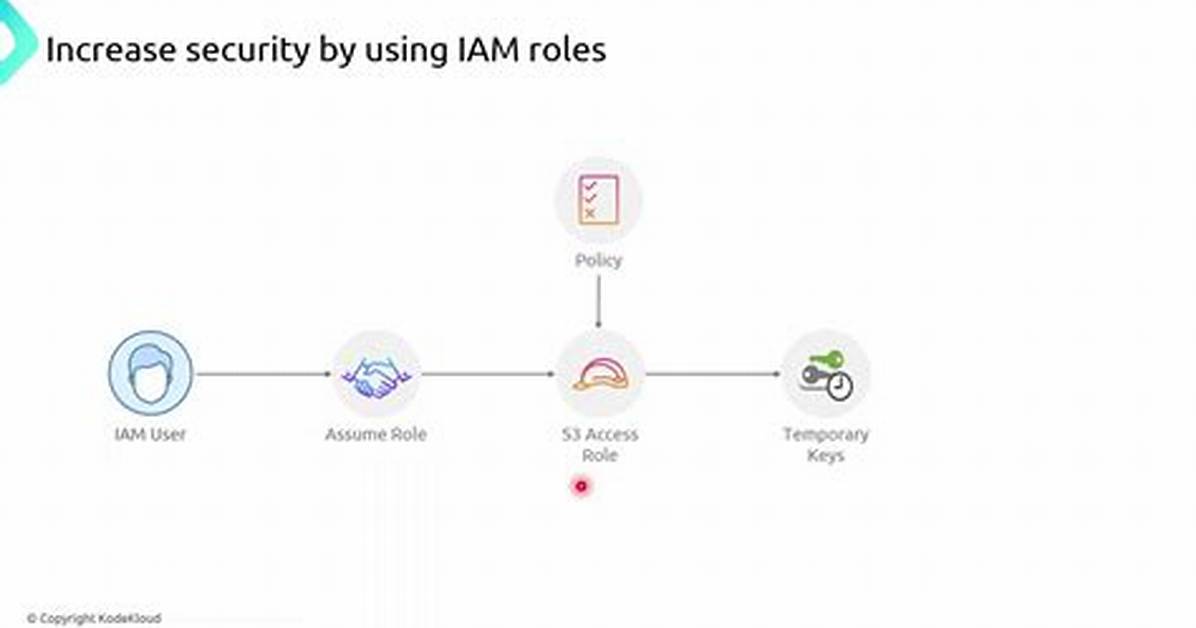
An IAM role is both an identity and a resource that supports resource-based policies. For that reason, you must attach both a trust policy and an identity-based policy to an IAM role. Trust policies define which principal entities (accounts, users, roles, and federated users) can assume the role.
What is the role of IAM manager?
The IAM Master role duty is to create IAM users, groups, and roles, while the IAM Manager role responsibility is to assign users and roles to IAM groups. This rule can help you with the following compliance standards: CISAWSF. APRA.
What are the two types of IAM roles?
There are three types of roles in IAM:
Basic roles, which include the Owner, Editor, and Viewer roles that existed prior to the introduction of IAM.Predefined roles, which provide granular access for a specific service and are managed by Google Cloud.
What is difference between IAM role and IAM policy?
Hi Sonal, IAM roles define the set of permissions for making AWS service request whereas IAM policies define the permissions that you will require.
What is role in AWS and why is it used?
AWS Identity and Access Management (IAM) roles provide a way to access AWS by relying on temporary security credentials. Each role has a set of permissions for making AWS service requests, and a role is not associated with a specific user or group.
Are IAM roles global?
AWS IAM is a global service that you can use to manage access to AWS services and resources. Access can be granted to IAM users, groups and roles using permission policies.
What is an IAM role quizlet?
An IAM role is an IAM entity that defines a set of permissions for making AWS service requests. IAM roles are not associated with a specific user or group. Instead, trusted entities assume roles, such as IAM users, applications, or AWS services such as EC2.
How do I find my role as an IAM?
Open the Amazon EC2 console at .
On the dashboard, choose Launch instance.Select an AMI and instance type and then choose Next: Configure Instance Details.On the Configure Instance Details page, for IAM role, select the IAM role that you created.
What is IAM role in GCP?
IAM lets you grant granular access to specific Google Cloud resources and helps prevent access to other resources. IAM lets you adopt the security principle of least privilege, which states that nobody should have more permissions than they actually need.
What are roles in GCP?
A role is a group of permissions that can be assigned to members. Creation of roles and assigning permissions to the roles can be done from the Google Cloud Platform (GCP) console. A project organizes all GCP resources.
What primitive roles can be found in a GCP IAM?
Primitive roles, i.e. “Owner”, “Editor” and “Viewer”, are managed roles that existed prior to the introduction of Cloud IAM. Predefined roles are roles created and maintained by Google, that provide granular access to specific Google Cloud Platform (GCP) resources and deny unwanted access to other resources.
How does IAM role connect to IAM user?
To assign IAM role to an IAM user, do the following:
Open the IAM Dashboard.Select the role that you want to assign to an IAM user.Edit the trust policy.add the ARN of the IAM user in the Principal’s section.
What is role and policy in AWS?
An IAM identity represents a user, and can be authenticated and then authorized to perform actions in AWS. Each IAM identity can be associated with one or more policies. Policies determine what actions a user, role, or member of a user group can perform, on which AWS resources, and under what conditions.

