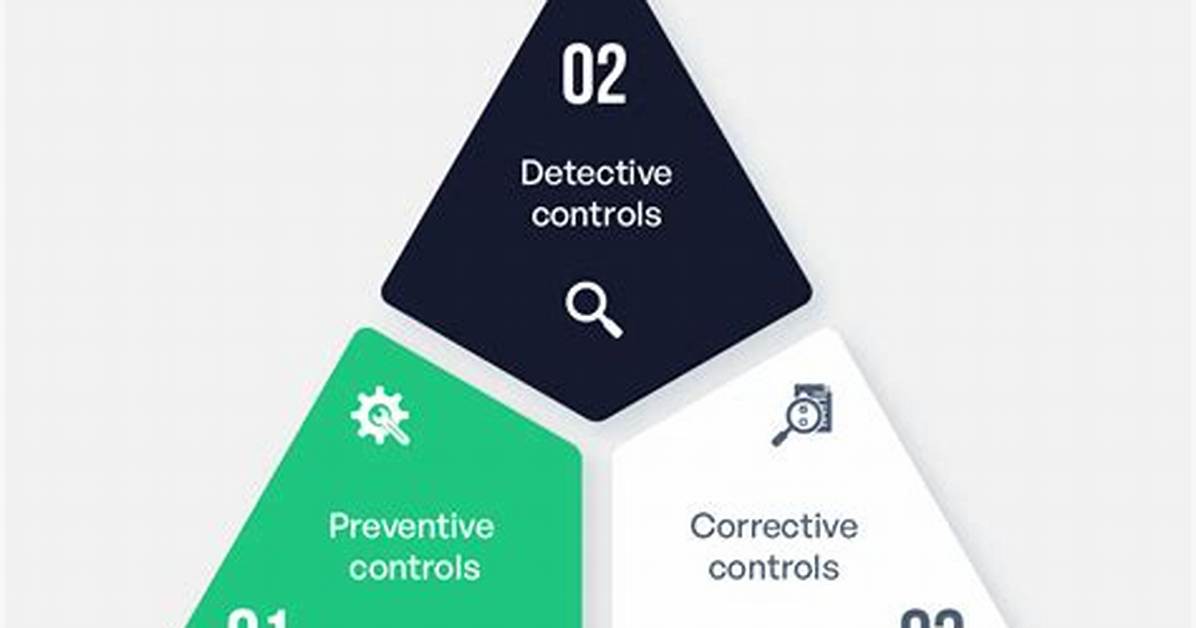
As the name suggests, corrective controls are put in place to fix any issues found through detective controls. These can also include remedying any issues made on accounting books after the audit process has been completed by an accountant.
What are the 3 types of internal controls?
There are three main categories of internal controls: preventative, detective and corrective. Internal controls are characteristically summed up as a series of policies and procedures or technical protections that are put in place to prevent problems and protect the assets of a business organization.
What are 3 examples of preventive controls?
Examples of preventive controls include:
Separation of duties.Pre-approval of actions and transactions (such as a Travel Authorization)Access controls (such as passwords and Gatorlink authentication)Physical control over assets (i.e. locks on doors or a safe for cash/checks)
What are the 5 internal controls?
There are five interrelated components of an internal control framework: control environment, risk assessment, control activities, information and communication, and monitoring.
Which of the following is a corrective control?
Explanation: Implementing data backup and recovery procedure is a corrective control, because backup and recovery procedures can be used to roll back database errors.
What is a preventive control?
Preventive Controls
Preventive controls attempt to prevent or deter undesirable acts from occurring. They are proactive controls, designed to prevent a loss, error, or omission.
What are the 7 internal control procedures?
The seven internal control procedures are separation of duties, access controls, physical audits, standardized documentation, trial balances, periodic reconciliations, and approval authority.
Separation of Duties. Accounting System Access Controls. Physical Audits of Assets. Standardized Financial Documentation.
What are two main types of control?
Yes, generally speaking there are two types: preventive and detective controls. Both types of controls are essential to an effective internal control system. From a quality standpoint, preventive controls are essential because they are proactive and emphasize quality.
What are the 9 common internal controls?
Here are controls: Strong tone at the top; Leadership communicates importance of quality; Accounts reconciled monthly; Leaders review financial results; Log-in credentials; Limits on check signing; Physical access to cash, Inventory; Invoices marked paid to avoid double payment; and, Payroll reviewed by leaders.
What are examples of Directive controls?
The Highway Code is an example of a directive control. Detective controls aim to identify a breach after the event, an example being a financial review or audit after activity has taken place. They will often lead to corrective action being taken.
What are SOX internal controls?
SOX controls, also known as SOX 404 controls, are rules that can prevent and detect errors in a company’s financial reporting process. Internal controls are used to prevent or discover problems in organizational processes, ensuring the organization achieves its goals.
What are the types of control measures?
When we look at control measures we often refer to the hierarchy of control measures.
Eliminate the hazard. Substitute the hazard with a lesser risk. Isolate the hazard. Use engineering controls. Use administrative controls. Use personal protective equipment.
What is a COSO framework?
The COSO Framework is a system used to establish internal controls to be integrated into business processes. Collectively, these controls provide reasonable assurance that the organization is operating ethically, transparently and in accordance with established industry standards.
What is COSO risk assessment?
Risk Assessment
COSO advocates for identifying and analyzing risks that may adversely affect the achievement of an objective and risks that may positively affect the objective. To ensure a clear risk assessment, the organization should specify the objectives and outline the risk in each stage.
What are the COSO principles?
COSO Principle 1: The entity demonstrates a commitment to integrity and ethical values. COSO Principle 2: The board of directors demonstrates independence from management and exercises oversight of the development and performance of internal control.
Which of the following is a corrective control of information security?
Corrective controls include any measures taken to repair damage or restore resources and capabilities to their prior state following an unauthorized or unwanted activity. Examples of technical corrective controls include patching a system, quarantining a virus, terminating a process, or rebooting a system.
Which of the following is Detective control?
Examples of detective controls include physical inventory checks, reviews of account reports and reconciliations, as well as assessments of current controls. Preventive controls stand in contrast to detective controls, as they are controls enacted to prevent any errors from occurring.
Which of the following is not one of the interrelated components of internal controls identified by the COSO Report?
B. internal control policies [Correct. Internal control policies are NOT one of COSO’s five components of internal control. However, control environment and control activities are two of the five internal control framework components.]

