This @CrossOrigin annotation enables cross-origin resource sharing only for this specific method. By default, its allows all origins, all headers, and the HTTP methods specified in the @RequestMapping annotation. Also, a maxAge of 30 minutes is used.
What does Crossorigin mean in HTML?
The crossorigin attribute sets the mode of the request to an HTTP CORS Request. Web pages often make requests to load resources on other servers. Here is where CORS comes in. A cross-origin request is a request for a resource (e.g. style sheets, iframes, images, fonts, or scripts) from another domain.
What is Crossorigin in script tag?
The crossorigin attribute on a
What is Crossorigin error?
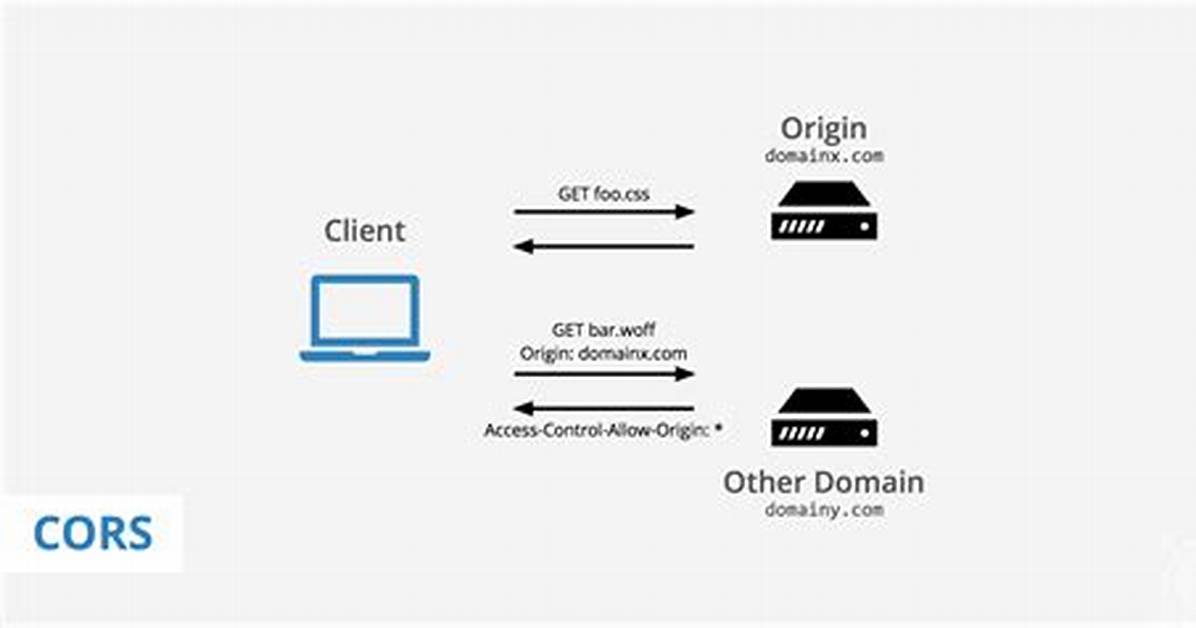
Cross-Origin Resource Sharing (CORS) is a standard that allows a server to relax the same-origin policy. This is used to explicitly allow some cross-origin requests while rejecting others. For example, if a site offers an embeddable service, it may be necessary to relax certain restrictions.
Why do we need CORS?
CORS is a way to whitelist requests to your web server from certain locations, by specifying response headers like 'Access-Control-Allow-Origin'. It's an important protocol for making cross-domain requests possible, in cases where there's a legitimate need to do so.
How do CORS work?
How CORS works. CORS allows the server to explicitly whitelist certain origin and help to bypass the same-origin policy. If your server is configured for CORS, it will return an extra header with “Access-Control-Allow-Origin” on each response.
How do I add Crossorigin?
For IIS6
Open Internet Information Service (IIS) Manager.Right click the site you want to enable CORS for and go to Properties.Change to the HTTP Headers tab.In the Custom HTTP headers section, click Add.Enter Access-Control-Allow-Origin as the header name.Enter * as the header value.Click Ok twice.
What is CORS in web API?
Cross-origin resource sharing (CORS) is a browser security feature that restricts cross-origin HTTP requests that are initiated from scripts running in the browser. If your REST API's resources receive non-simple cross-origin HTTP requests, you need to enable CORS support.
How do CORS headers work?
CORS also relies on a mechanism by which browsers make a "preflight" request to the server hosting the cross-origin resource, in order to check that the server will permit the actual request. In that preflight, the browser sends headers that indicate the HTTP method and headers that will be used in the actual request.
How do I enable CORS in HTML?
Perform the following steps:
Open Internet Information Service (IIS) Manager.Right-click the site you want to enable CORS for and go to Properties.Change to the HTTP Headers tab.In the Custom HTTP headers section, click Add.Enter Access-Control-Allow-Origin as the header name.Enter * as the header value.Click Ok twice.
How do I remove CORS error in Reactjs?
set the request's mode to 'no-cors' to fetch the resource with CORS disabled. It states that there's a missing Access-Control-Allow-Origin header on the resource you requested.
What is integrity in HTML?
The integrity attribute allows a browser to check the fetched script to ensure that the code is never loaded if the source has been manipulated. Subresource Integrity (SRI) is a W3C specification that allows web developers to ensure that resources hosted on third-party servers have not been altered.
How do I fix the problem with CORS in chrome?
Turn OFF the CORS plugin, reload the app, at this time you should still get the errors which are correct. ii. Turn it back ON, reload the app, if the APIs are successful, stop here, no need to proceed to iii.
How do I disable CORS in chrome?
Run Chrome browser without CORS
Right click on desktop, add new shortcut.Add the target as "[PATH_TO_CHROME]chrome.exe" --disable-web-security --disable-gpu --user-data-dir=~/chromeTemp.Click OK.
How do you fix a CORS problem?
Open a network tab in your console. In the response header look for the Access-Control-Allow-Origin header. If it does not exist then add it as a middleware in the way we discussed above. If it does exist then make sure there is no URL mismatch with the website.
How do I enable CORS in API?
You can enable CORS per action, per controller, or globally for all Web API controllers in your application. To enable CORS for a single action, set the [EnableCors] attribute on the action method. The following example enables CORS for the GetItem method only.
How is CORS secure?
CORS is a security mechanism that allows a web page from one domain or Origin to access a resource with a different domain (a cross-domain request). CORS is a relaxation of the same-origin policy implemented in modern browsers.
Is CORS server side?
CORS is a unique web technology in that it has both a server-side and a client-side component. The server-side component configures which types of cross-origin requests are allowed, while the client-side component controls how cross-origin requests are made.

