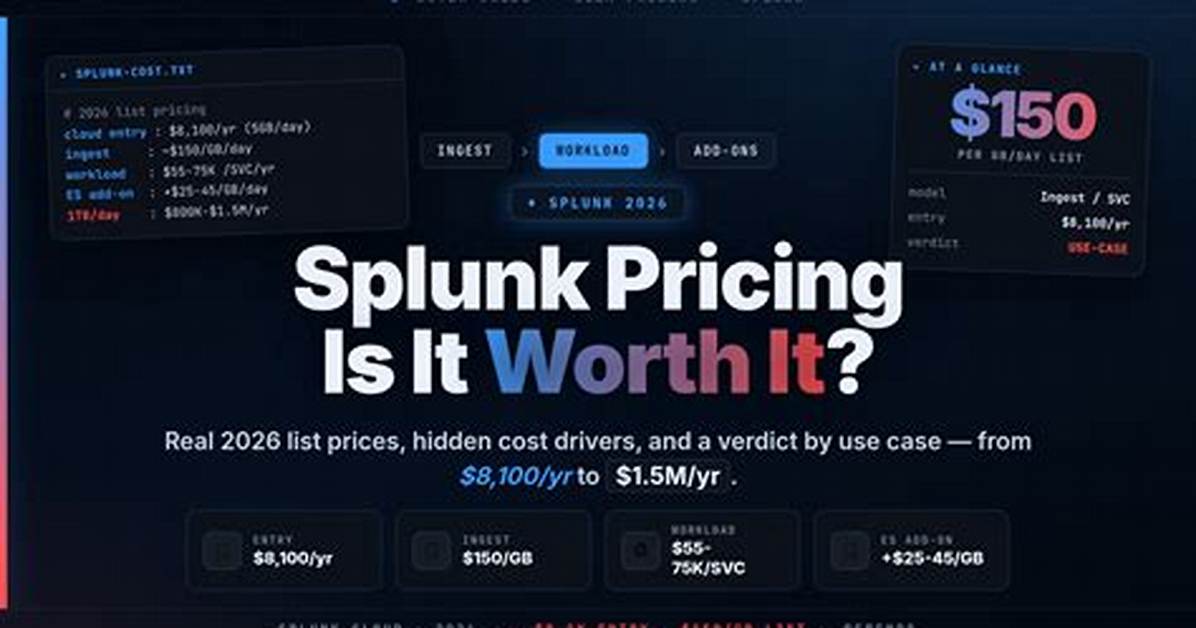
Splunk Cloud annual pricing ranges from $8,100 to $24,000 for 5 GB/day to 20 GB/day of indexing volume; custom quotes are available for larger volumes.
Is Splunk still free?
Splunk is available in three versions: the free version (or Splunk Light), the paid version (Splunk Enterprise), and Splunk Cloud (or Splunk Enterprise as a Service).
Is Splunk an open source?
No, Splunk is not an open source and there is a good amount of costing is associated with its usage.
How much does Splunk SIEM cost?
Pricing is available as a perpetual or annual term license, is based on maximum daily data ingestion, and? starts at $2,000/year for 1 GB/day. Splunk Cloud is available for monthly or annual subscription.
Why elk is better than Splunk?
Elasticsearch is a database search engine, and Splunk is a software tool for monitoring, analyzing, and visualizing the data. Elasticsearch stores the data and analyzes them, whereas Splunk is used to search, monitor, and analyze the machine data.
What is the difference between Splunk and Splunk es?
Splunk enterprise is platform and whereas Splunk Enterprise Security is Splunk-developed licensed application that sits on top of Splunk. You need to install Splunk first to use Splunk Enterprise Security and then import the application.
How long is Splunk free?
Search, analyze and visualize your data with a free Splunk download for 60 days.
What is Splunk competitor?
Answer: Splunk competes in a wide range of markets. However, the company’s main competitors are IBM Security (QRadar), McAfee SIEM, AlienVault, LogRhythm, CA Technologies, HPE ArcSight, and SolarWinds.
Why is Splunk so popular?
It is Scalable and has no Backend
This makes Splunk available on multiple platforms and can be installed speedily on any software. If one server is not enough another can be added easily and data is distributed across both these servers evenly.
Is Splunk the best tool?
Splunk is an excellent tool. In fact, it’s one of the most encompassing, analytical, and widely used log-management software available. The machine data analytics platform comes with its own SPL language for transforms, queries, visualizations, and statistical analysis.
Is Splunk easy to learn?
Is Splunk Easy to Learn? The courses to learn Splunk are easily accessible online. However, it simply takes time and dedication to learn like any skill. There are many courses available online that you can take in the ease of your own home from your laptop.
Is Kibana like Splunk?
Kibana is the visualization tool in the ELK Stack, and like Splunk, the platform supports the creation of visualizations such as line charts, area arts and tables and the presentation of them in a dashboard.
Is Splunk a SIEM or soar?
Splunk SOAR integrates across 350+ third-party tools and supports over 2,800 different automatable actions. Connect and coordinate complex workflows across your team and tools.
What is difference between Splunk and Kibana?
Kibana allows data formats like JSON; unlike Splunk, it does not allow all kinds of data, but it can be integrated with third parties to send data in the desired format. Splunk can take in any data formats like . csv, log files, JSON, etc. and is very flexible for integrating with other plugins or tools.
Can I use elk for free?
ELK stack software is free to use, but building, growing, and maintaining the ELK stack requires infrastructure and resources. Whether you deploy on-premises or in the cloud, your costs for computing and data storage will depend on: The total log volume you aggregate daily from all applications, systems, and networks.
Is Splunk based on Hadoop?
The Splunk Hadoop monitoring allows this company a single interface to search, monitor and analyze the full Hadoop environment including cluster resources beyond Hadoop itself, such as the network, operating system and database. Thanks!

