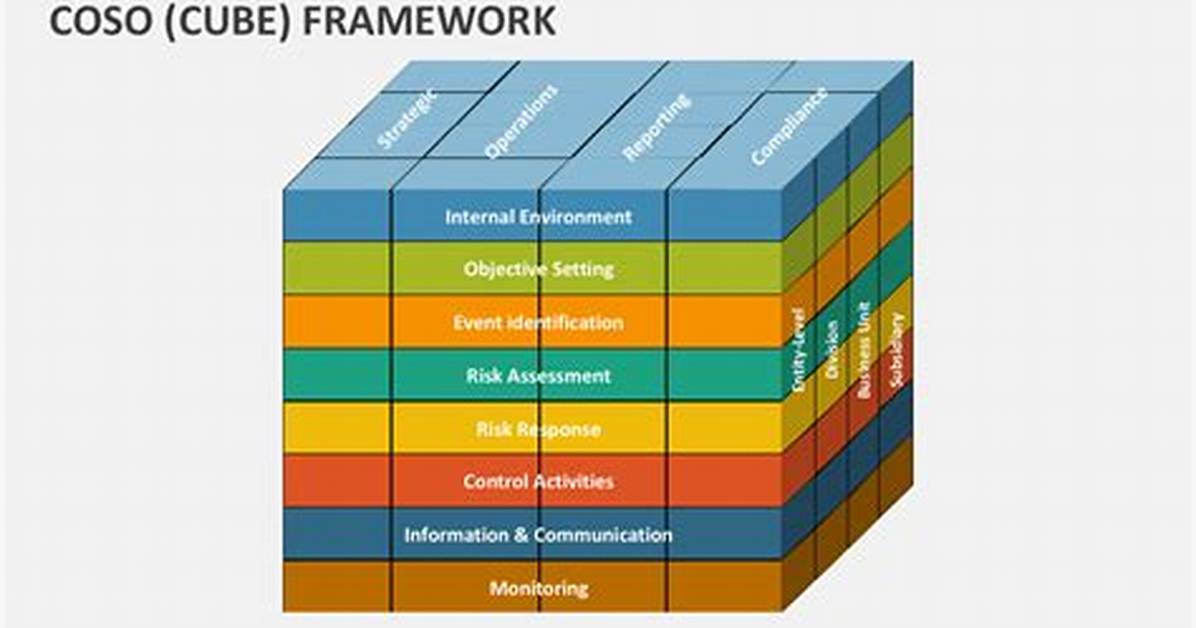
The COSO cube is a diagram that shows the relationship among all parts of an internal control system. Aside from showing how these parts are connected, it also identifies a number of principles an organization should follow to meet their internal control objectives.
What are the 5 components of COSO?
Here are the five components of the COSO framework:
Control environment. The control environment seeks to make sure that all business processes are based on the use of industry-standard practices. Risk assessment and management. Control activities. Information and communications. Monitoring.
What is COSO stand for?
WHAT DOES COSO STAND FOR? In 1992, the Committee of Sponsoring Organizations of the Treadway Commission (COSO) developed a COSO Framework for evaluating internal controls.
What are the 3 COSO internal control objectives?
The COSO framework objectives are divided into three distinct disciplines: operations, reporting, and compliance. The goal behind internal control systems is to achieve an organization’s overall business objectives and strategy.
What are the 5 internal controls?
There are five interrelated components of an internal control framework: control environment, risk assessment, control activities, information and communication, and monitoring.
What are the 3 types of internal controls?
There are three main categories of internal controls: preventative, detective and corrective. Internal controls are characteristically summed up as a series of policies and procedures or technical protections that are put in place to prevent problems and protect the assets of a business organization.
What is COSO in risk management?
COSO is short for the Committee of Sponsoring Organizations of the Treadway Commission (COSO). Founded in 1985, COSO is a private-sector initiative originally formed to combat fraudulent financial reporting but has expanded its mission over the years to include internal controls and enterprise risk management.
What is COSO testing?
What is COSO? COSO is the acronym used to refer to a model used for testing and evaluating internal control and processes.
What is COSO risk assessment?
Risk assessment is one of the key components of the COSO internal control framework. It addresses how the organization assesses risk and identifies threats the organization.
Who uses COSO?
COSO is a committee composed of representatives from five organizations: American Accounting Association. American Institute of Certified Public Accountants. Financial Executives International.
Who created COSO?
It was founded by five major professional associations, The American Accounting Organization (AAA), American Institute of Certified Public Accountants (AICPA), Financial Executives International (FEI), Institute of Internal Auditors (IIA), and Institute of Management Accountants (IMA) Organizations seeking to scale
Why is the COSO framework important?
The overarching goal of a COSO Framework is to enhance and improve organizational performance and oversight, as well as reducing the extent of the risk of fraud.
How do you use COSO framework?
Implementing the COSO Framework in Five Phases
PHASE 1: PLAN AND SCOPE. Appoint an implementation team. PHASE 2: ASSESS AND DOCUMENT. In this phase, the implementation team assesses the organization’s control structure. PHASE 3: REMEDIATE. PHASE 4: DESIGN, TEST, AND REPORT. PHASE 5: OPTIMIZE INTERNAL CONTROLS’ EFFECTIVENESS.
How is COSO used in internal audit?
The four principles of the COSO risk assessment component are:
Specify appropriate objectives,Identify and analyze risks,Evaluate fraud risks, and.Identify and analyze changes that could significantly affect internal controls.
What is control environment in COSO?
Control Environment is the set of standards, processes, and structures that provide the basis for carrying out internal control across the organization. The board of directors and senior management establish the tone at the top regarding the importance of internal control including expected standards of conduct.
What are the 7 principles of internal control?
The seven internal control procedures are separation of duties, access controls, physical audits, standardized documentation, trial balances, periodic reconciliations, and approval authority.
What are the 4 types of internal controls?
Preventive Controls
Separation of duties.Pre-approval of actions and transactions (such as a Travel Authorization)Access controls (such as passwords and Gatorlink authentication)Physical control over assets (i.e. locks on doors or a safe for cash/checks)
What are the 9 common internal controls?
Here are controls: Strong tone at the top; Leadership communicates importance of quality; Accounts reconciled monthly; Leaders review financial results; Log-in credentials; Limits on check signing; Physical access to cash, Inventory; Invoices marked paid to avoid double payment; and, Payroll reviewed by leaders.

