The TPM is a cryptographic module that enhances computer security and privacy. Protecting data through encryption and decryption, protecting authentication credentials, and proving which software is running on a system are basic functionalities associated with computer security.
Where do I find TPM headers?
To open it, press Windows+R to open a run dialog window. Type tpm. msc into it and press Enter to launch the tool. If you see information about the TPM in the PC—including a message at the bottom right corner of the window informing you which TPM specification version your chip supports—your PC does have a TPM.
What is TPM interface?
Trusted Platform Module (TPM, also known as ISO/IEC 11889) is an international standard for a secure cryptoprocessor, a dedicated microcontroller designed to secure hardware through integrated cryptographic keys. The term can also refer to a chip conforming to the standard. Trusted Platform Module. Abbreviation. TPM.
Can I add TPM to my computer?
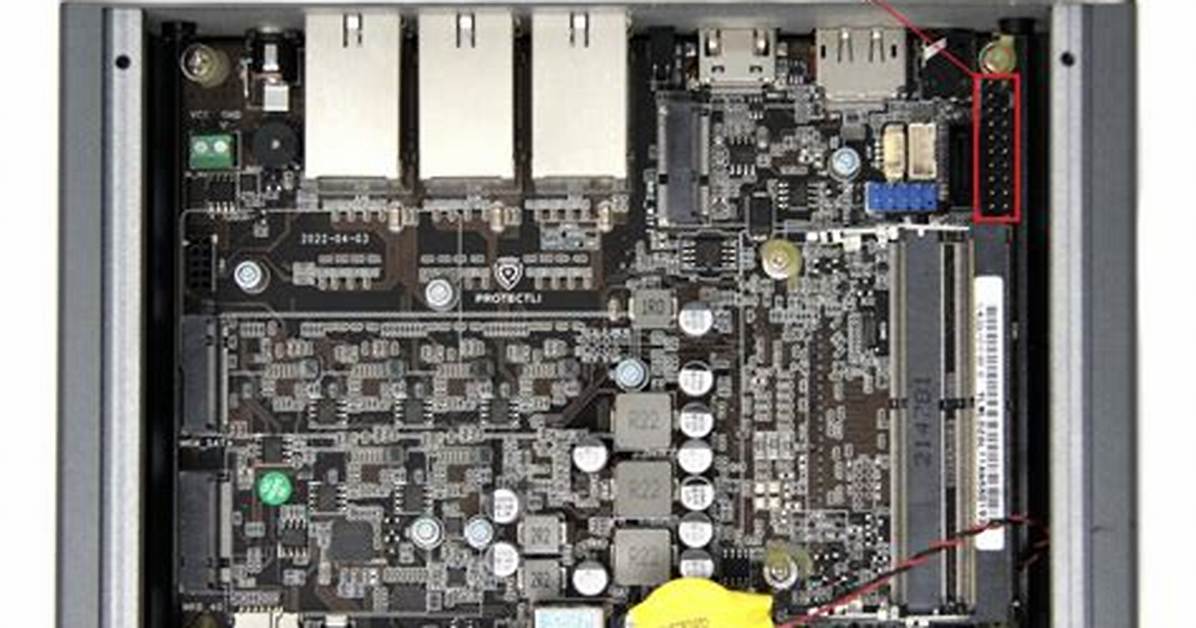
If you’re savvy with technology, you can open your PC and check your motherboard. Check the manufacturer’s website for more technical details if you’re still unsure. You can also check your motherboard model number online. This TPM port is open, and you can install an aftermarket TPM chip on this motherboard.
What is TPM security in BIOS?
A Trusted Platform Module (TPM) is a specialized chip on a laptop or desktop computer that is designed to secure hardware with integrated cryptographic keys. A TPM helps prove a user’s identity and authenticates their device. A TPM also helps provide security against threats like firmware and ransomware attacks.
What does TPM mean on a motherboard?
Trusted Platform Module (TPM) technology is designed to provide hardware-based, security-related functions. A TPM chip is a secure crypto-processor that is designed to carry out cryptographic operations.
Is TPM in CPU or motherboard?
TPM is usually a dedicated chip on a motherboard that provides hardware encryption for features like Windows Hello and BitLocker. Most motherboards you can buy don’t come with a dedicated chip, but they do come with firmware that can look and act like TPM in Windows.
How do I know if my motherboard has TPM?
Press [Windows Key] + R or select Start > Run. Type “tpm.msc” (do not use quotation marks) and choose OK. If you see a message saying a “Compatible TPM cannot be found,” your PC may have a TPM that is disabled.
How do I enable TPM in BIOS?
How to Enable TPM 2.0 in BIOS
Restart your PC.Hold down the F2 key (FN F2 if no dedicated function keys) during boot up to get to the BIOS menu.Use the arrow keys to navigate to the Security tab.Find a listing for either TPM, Intel Platform Trust Technology (IPTT), or AMD CPU fTPM.Toggle to “Enabled”
Should I enable TPM?
As a hardware device, the TPM is immune to malware and forgery. Remember, Trusted Computing technology protects sensitive data, but it also requires specific hardware components. And hardware can fail. Enable TPMs only where most appropriate, manage passwords vigilantly and be sure to test TPM behaviors thoroughly.
Where is TPM chip located?
The TPM is installed on the motherboard of a computer, and it communicates with the rest of the system by using a hardware bus. Computers that incorporate a TPM can create cryptographic keys and encrypt them so that they can only be decrypted by the TPM.
What keys are stored in TPM?
TPM (Trusted Platform Module) is a computer chip (microcontroller) that can securely store artifacts used to authenticate the platform (your PC or laptop). These artifacts can include passwords, certificates, or encryption keys.
What if my PC does not have TPM?
Open the Device Manager and look for a node called “Security devices“. Expand it and see if it has a “Trusted Platform Module” listed. This will let you view the current status of the TPM chip: activated or enabled. If there is no TPM installed on your computer, you’ll get the message “No Instance(s) Available“.
Does TPM slow down computer?
Many computers, including several product lines from Teguar, come with a TPM chip by default, but the TPM is inactive until it is enabled in the BIOS. It will not affect the computer in anyway, the chip will lay dormant, until activated. Once activated, a user may notice a slower boot up process with the OS.
How do I install Windows TPM?
Press the required key repeatedly until you enter the setup mode. Typically, you need to press the Esc, Delete, or one of the Function keys (F1, F2, F10, etc.). Open the security settings page. Select the Trusted Platform Module (TPM) option and press Enter.
What is TPM in BIOS HP?
Select Trusted Platform Module Options and press the Enter key. Select Enabled to enable the TPM and BIOS secure startup. The TPM is fully functional in this mode. Press the F10 key to save your selection.
Does TPM affect performance?
Ryzen performance affected for second time in three months
Commonly reported problems include frequent stuttering and audio glitches, with affected users expressing their frustration. The issues appear to be caused by the TPM 2.0 module, one of Windows 11’s key hardware requirements.
Can TPM be hacked?
Can the attacker use it to hack your network? Research published last week shows that the answer is a resounding “yes.” Not only that, but a hacker who has done her homework needs a surprisingly short stretch of time alone with the machine to carry out the attack.

