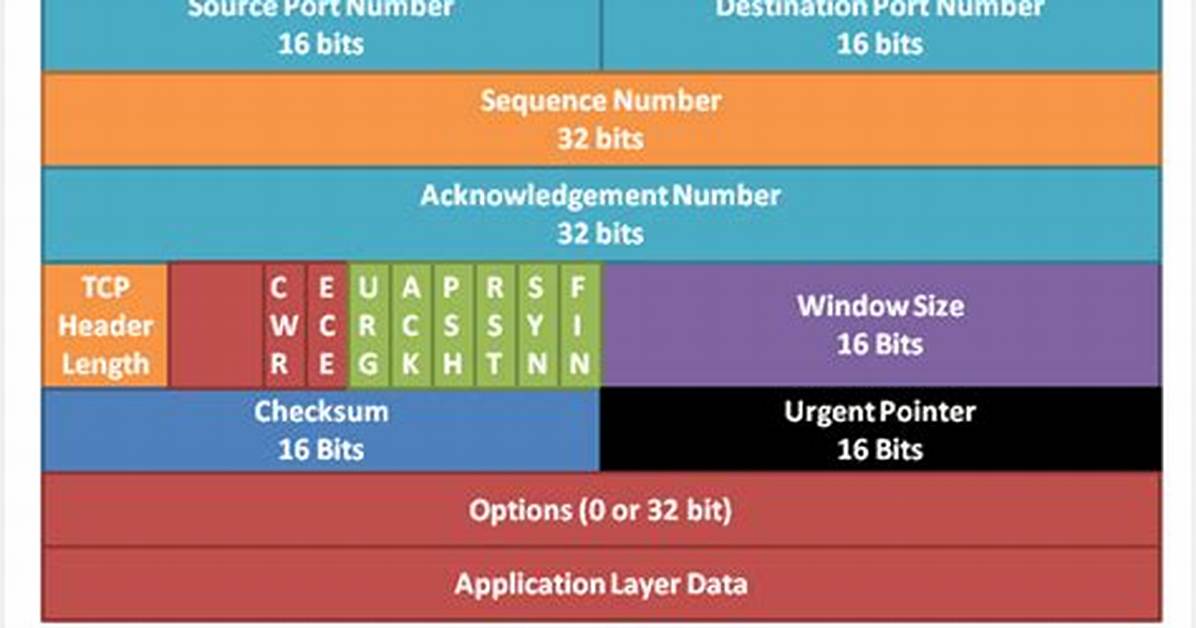
The Transmission Control Protocol (TCP) header is the first 24 bytes of a TCP segment that contains the parameters and state of an end-to-end TCP socket. The TCP header is used to track the state of communication between two TCP endpoints.
What are the 6 TCP flags?
We will begin our analysis by examining all six flags, starting from the top, that is, the Urgent Pointer:
1st Flag – Urgent Pointer. 2nd Flag – ACKnowledgement. 3rd Flag – PUSH. 4th Flag – Reset (RST) Flag. 5th Flag – SYNchronisation Flag. 6th Flag – FIN Flag. Summary.
What is TCP and UDP header?
Both TCP and UDP use headers as part of packaging the message data for transfer over network connections. Because TCP is the more robust of the two protocols, its header is larger at 20 bytes with an option for additional data, while UDP headers are limited to 8 bytes in size.
What is a header in Wireshark?
Wireshark captures full packets by default, so all HTTP headers are included anyway. You just need to open the HTTP section in the decode pane to see them all. If someone uses a proxy you can often see a “X-Forwarded-For” header that tells you for which original IP address the request was processed by the proxy.
What is SYN flag in TCP?
The SYN flag synchronizes sequence numbers to initiate a TCP connection. The FIN flag indicates the end of data transmission to finish a TCP connection. Their purposes are mutually exclusive.
What is CWR flag in TCP header?
CWR – The congestion window reduced flag is used by the sending host to indicate it received a packet with the ECE flag set. See RFC 3168 for more details. NS (experimental) – The nonce sum flag is still an experimental flag used to help protect against accidental malicious concealment of packets from the sender.
Which two fields are included in the TCP header?
The sequence number and window fields are included in the TCP header but not in the UDP header.
What is the difference between IP header and TCP header?
TCP operates with the internet protocol (IP) to specify how data is exchanged online. IP is responsible for sending each packet to its destination, while TCP guarantees that bytes are transmitted in the order in which they were sent with no errors or omissions. Together, the two protocols are referred to as TCP/IP.
How do I make a header in Wireshark?
If you just mean figuring out what part of the capture is the HTTP header, etc., Wireshark should automatically dissect the packets. Find any HTTP data packet, right-click and select “Follow TCP Stream” and it will show the HTTP traffic with the headers clearly readable.
What is FIN ACK in TCP?
[ACK] is the acknowledgement that the previously sent data packet was received. [FIN] is sent by a host when it wants to terminate the connection; the TCP protocol requires both endpoints to send the termination request (i.e. FIN ).
What are the 3 steps in a TCP handshake?
The TCP handshake
The connection is full duplex, and both sides synchronize (SYN) and acknowledge (ACK) each other. The exchange of these four flags is performed in three steps—SYN, SYN-ACK, and ACK—as shown in Figure 3.8.
What is the difference between push and URG flag?
The gist of the matter is that once you push data on a connection you have to wait for the receiver to get all of it before it gets to the new data. This is where the URG flag kicks in. When you send urgent data, your TCP creates a special segment in which it sets the URG flag and also the urgent pointer field.

