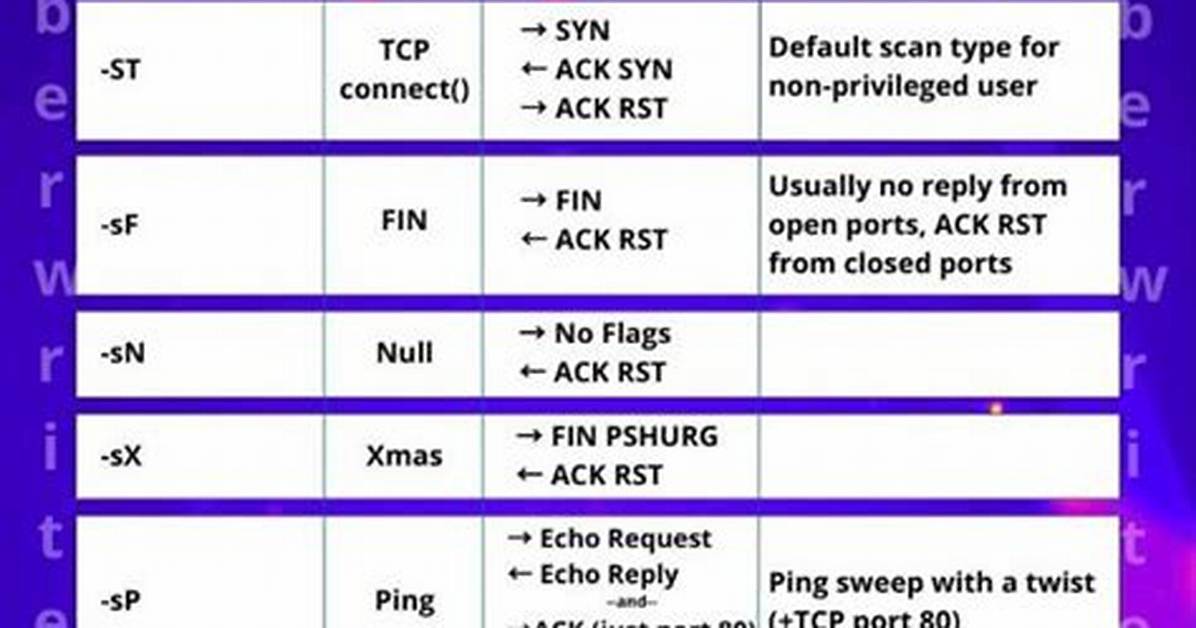
These flags are used for scanning port related information about target hosts. If you know which ports are open then you have a potential opening to get into the system, so pentesters rely heavily on this kind of Nmap query.
What is PN flag in Nmap?
-PN (No ping) . This option skips the Nmap discovery stage altogether. Normally, Nmap uses this stage to determine active machines for heavier scanning. By default, Nmap only performs heavy probing such as port scans, version detection, or OS detection against hosts that are found to be up.
Is it OK to Nmap Google?
The Nmap project has been wrongfully labeled as a cybersecurity “threat” by Google Chrome’s Safe Browsing service. The incident is the latest example of legitimate security tools becoming categorized in the same way as malware, phishing code, or malicious exploits.
What are Nmap arguments?
The only Nmap arguments used in this example are -A, to enable OS and version detection, script scanning, and traceroute; -T4 for faster execution; and then the two target hostnames. The newest version of Nmap can be obtained from
What is aggressive scan in Nmap?
Aggressive Scanning
Nmap has an aggressive mode that enables OS detection, version detection, script scanning, and traceroute. You can use the -A argument to perform an aggressive scan. > nmap -A scanme.nmap.org. Aggressive scans provide far better information than regular scans.
What does the oX flag do in an Nmap scan?
So the command nmap -oX – target will send only XML output to stdout. Serious errors may still be printed to the normal error stream, stderr. When you specify a filename to an output format flag such as -oN , that file is overwritten by default.
What is the flag for a UDP scan?
By default Nmap omits UDP scan, it can be enabled by adding the Nmap flag -sU. As listed above by ignoring UDP ports known vulnerabilities may remain ignored to the user. Nmap outputs for UDP scan may be open, open|filtered, closed and filtered.
Is it illegal to Nmap scan an IP?
While civil and (especially) criminal court cases are the nightmare scenario for Nmap users, these are very rare. After all, no United States federal laws explicitly criminalize port scanning. Unauthorized port scanning, for any reason, is strictly prohibited.
Is scanning an IP address illegal?
In the U.S., no federal law exists to ban port scanning.
Is it illegal to run Nmap on a website?
Network probing or port scanning tools are only permitted when used in conjunction with a residential home network, or if explicitly authorized by the destination host and/or network. Unauthorized port scanning, for any reason, is strictly prohibited.
What are Nmap commands?
Nmap Commands
Scan a Range of IP Address. Aim: To scan the entire IP range. Port Scanning. Aim: To scan a specific port or entire port range. Ping Scan Using Nmap. Saving the Nmap Scan Output to a File. Most Popular Ports Scanning. Display Open Ports. Exclude Host/ IP Addresses for the Scan. Service Version Detection.
What are Nmap scripts?
The Nmap Scripting Engine (NSE) is one of Nmap’s most powerful and flexible features. It allows users to write (and share) simple scripts (using the Lua programming language ) to automate a wide variety of networking tasks. Those scripts are executed in parallel with the speed and efficiency you expect from Nmap.
How many ports will Nmap scan if the flag was used?
By default, Nmap scans the 1,000 most popular ports of each protocol it is asked to scan. Alternatively, you can specify the -F (fast) option to scan only the 100 most common ports in each protocol or –top-ports to specify an arbitrary number of ports to scan.
Can Nmap detect OS?
Nmap is one of the most popular tools used for the enumeration of a targeted host. Nmap can use scans that provide the OS, version, and service detection for individual or multiple devices. Detection scans are critical to the enumeration process when conducting penetration testing of a network.
What is T4 in Nmap?
The -T4 is for the speed template, these templates are what tells nmap how quickly to perform the scan. The speed template ranges from 0 for slow and stealthy to 5 for fast and obvious.
What is decoy in Nmap?
nmap has -D option. It is called decoy scan. With -D option it appear to the remote host that the host(s) you specify as decoys are scanning the target network too. Thus their IDS might report 5-10 port scans from unique IP addresses, but they won’t know which IP was scanning them and which were innocent decoys.

