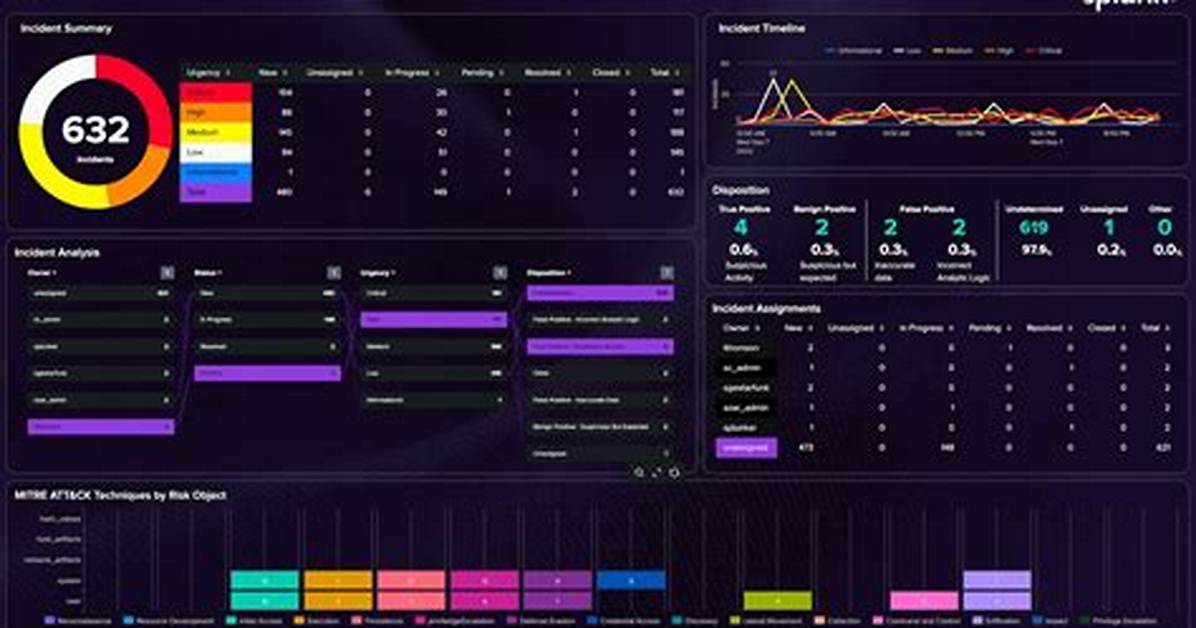
Splunk is used for monitoring and searching through big data. It indexes and correlates information in a container that makes it searchable, and makes it possible to generate alerts, reports and visualizations.
What is Splunk in simple terms?
Splunk is a software platform widely used for monitoring, searching, analyzing and visualizing the machine-generated data in real time. It performs capturing, indexing, and correlating the real time data in a searchable container and produces graphs, alerts, dashboards and visualizations.
Why is Splunk so popular?
It is Scalable and has no Backend
This makes Splunk available on multiple platforms and can be installed speedily on any software. If one server is not enough another can be added easily and data is distributed across both these servers evenly.
What is Splunk used for in Cyber security?
Splunk allows security teams to analyze large data sets, detect malicious network activity, and respond to threats across environments quickly and more accurately than legacy SIEM systems.
What is Splunk in DevOps?
Splunk is a popular application monitoring tool to gain real-time visibility into DevOps-driven application delivery for Continuous Delivery or Continuous Integration to move from concept to production quickly.
What is Splunk used for Quora?
In a nutshell, Splunk is Data collection, analysis & Visualisation Tool. Companies use this tool to collect and monitor various types of data such as Application Metrics, Application, Transactional Data, Customer Data, Network Data, Configuration Settings, csv , Security data, and more!
What programming language does Splunk use?
The Splunk daemon is written in C++ and offers a solid internal architecture for fast and effective data collection, storage, indexing and search capabilities. The Splunk Web Services is written in AJAX, Python and XML, among other languages to create an intuitive and easy-to-use graphical user interface.
Is Kibana like Splunk?
Kibana is the visualization tool in the ELK Stack, and like Splunk, the platform supports the creation of visualizations such as line charts, area arts and tables and the presentation of them in a dashboard.
What is Splunk database?
Splunk is a database system designed for extracting structure and analyzing machine-generated data. It takes in data from other databases, web servers, networks, sensors, etc. and then offers services to analyze the data, and produce dashboards, graphs, reports, alerts, and other visualizations.
Is Splunk a CRM?
The company further enriched the data by connecting Splunk software to its custom- built CRM system, enabling them to append every event with information on each customer’s city, history and device type. Step #2—Use real-time search to create insight.
What are the benefits of Splunk?
The benefits of Splunk
carries out specific searches.converts complex data into simple information.contributes to the adoption of a data-driven approach in the company.monitors operational flows in real time.integrates Machine Learning and Artificial Intelligence solutions into data management in a very simple way.
What is difference between Splunk and Elasticsearch?
Elasticsearch is a database search engine, and Splunk is a software tool for monitoring, analyzing, and visualizing the data. Elasticsearch stores the data and analyzes them, whereas Splunk is used to search, monitor, and analyze the machine data.
What type of technology is Splunk?
About Splunk | What is Splunk? Splunk. A data platform built for expansive data access, powerful analytics and automation. Cloud-powered insights for petabyte-scale data analytics across the hybrid cloud.
Is Splunk a cloud?
Splunk® Cloud™ delivers the capabilities of Splunk as Software-as-a-Service (SaaS), enabling you to make confident decisions and take decisive action on insights from your data without the need to purchase, manage and deploy additional infrastructure.
What is Splunk observability?
Observability is a property of that system, like functionality or testability. Specifically, monitoring is the act of observing a system’s performance over time. Monitoring tools collect and analyze system data and translate it into actionable insights.
Is Splunk a programming language?
Splunk is not a programming language. It is a software-based platform to store and manage machine-generated data. It allows you to search through and visualize large amounts of data with ease. You also don’t need to know programming to become a professional Splunk administrator.
What are Splunk logs?
Logs contain a record of customer activity and behavior, product and service usage, and transactions. Logs contain a record of activity for IT components, such as applications, servers and network devices.
Is Splunk a soar?
Splunk Security Orchestration, Automation and Response (SOAR)
Recommended Posts
porque as pessoas boiam nas aguas do mar morto confira isto porque as pessoas boiam no mar morto
quem e o melhor jogador de free fire do mundo atualmente confira isto qual o melhor jogador de free fire do mundo
que quiere decir poner en evidencia confira isto sinonimo de evidencia se
qual a profissao do marido da cantora iza confira isto marido da cantora iza
quantas e quais sao as modalidades do slackline confira isto quais as modalidades do slackline
quando vai sair a 3 temporada de voce confira isto quando sai a 3 temporada de voce
o que e metrica e de exemplos confira isto o que e metrica no poema
quais sao as etapas do desenvolvimento psicomotor confira isto fases do desenvolvimento psicomotor

