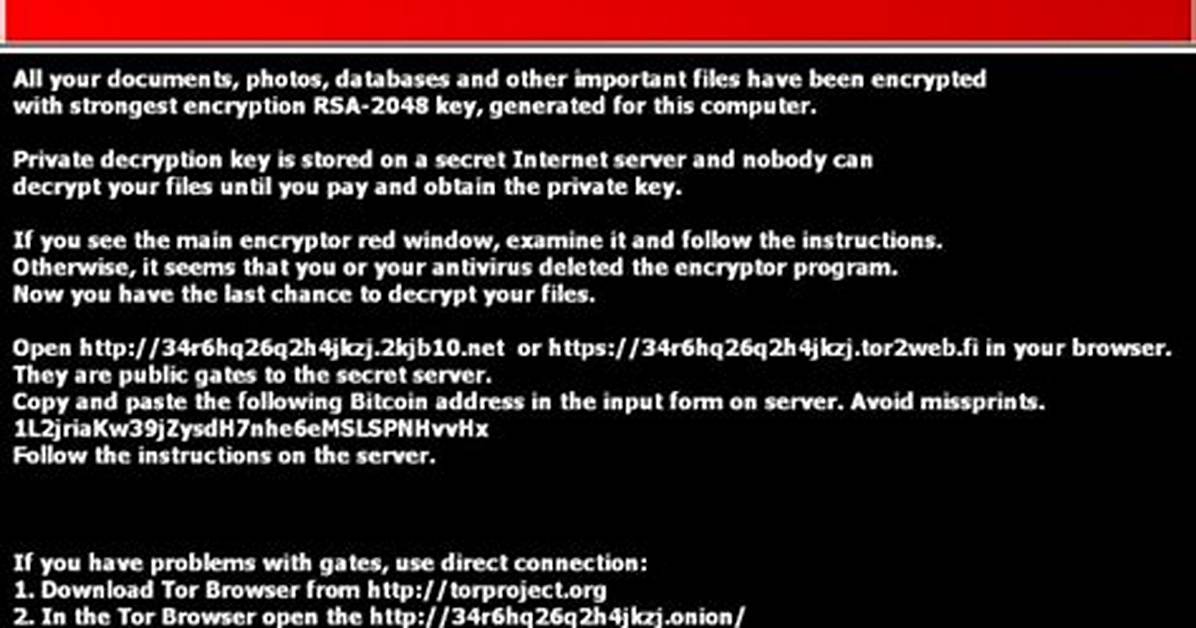
What is Win32/Filecoder.ODCODC.C infection?
In this post you will locate regarding the interpretation of Win32/Filecoder.ODCODC.C and also its unfavorable impact on your computer system. Such ransomware are a kind of malware that is clarified by on the internet fraudulences to require paying the ransom by a target.
In the majority of the situations, Win32/Filecoder.ODCODC.C ransomware will certainly instruct its sufferers to start funds transfer for the purpose of neutralizing the modifications that the Trojan infection has presented to the sufferer’s gadget.
Win32/Filecoder.ODCODC.C Summary
These adjustments can be as follows:
- HTTP traffic contains suspicious features which may be indicative of malware related traffic;
- Performs some HTTP requests;
- Behavior consistent with a dropper attempting to download the next stage.;
- Installs itself for autorun at Windows startup. There is simple tactic using the Windows startup folder located at:
C:\Users\[user-name]\AppData\Roaming\Microsoft\Windows\StartMenu\Programs\Startup. Shortcut links (.lnk extension) placed in this folder will cause Windows to launch the application each time [user-name] logs into Windows.The registry run keys perform the same action, and can be located in different locations:
- HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Run
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run
- HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\RunOnce
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\RunOnce
- Exhibits possible ransomware file modification behavior;
- Attempts to modify proxy settings. This trick used for inject malware into connection between browser and server;
- Creates a copy of itself;
- Ciphering the records situated on the target’s disk drive — so the victim can no longer make use of the information;
- Preventing normal accessibility to the victim’s workstation;
| e1.mysit.ru | Trojan.Ransom.Odcodc |
| e2.mysit.ru | Trojan.Ransom.Odcodc |
Win32/Filecoder.ODCODC.C
One of the most common networks whereby Win32/Filecoder.ODCODC.C Trojans are infused are:
- By methods of phishing e-mails. Email phishing is a cyber attack that uses disguised email as a goal is to trick the recipient into believing that the message is something they want or need — a request from their bank, for instance, or a note from someone in their company — and to click a link for download a malware.
- As an effect of user winding up on a resource that holds a malicious software application;
As quickly as the Trojan is efficiently injected, it will either cipher the information on the sufferer’s computer or protect against the tool from functioning in an appropriate fashion – while additionally putting a ransom money note that discusses the need for the victims to impact the settlement for the objective of decrypting the records or bring back the file system back to the preliminary condition. In most circumstances, the ransom note will certainly show up when the customer reboots the COMPUTER after the system has actually already been harmed.
Win32/Filecoder.ODCODC.C distribution networks.
In different corners of the globe, Win32/Filecoder.ODCODC.C expands by jumps as well as bounds. Nevertheless, the ransom money notes and methods of obtaining the ransom money quantity may differ relying on certain regional (local) setups. The ransom money notes and methods of extorting the ransom money quantity may vary depending on particular neighborhood (local) setups.
For instance:
Faulty notifies regarding unlicensed software.
In particular areas, the Trojans typically wrongfully report having spotted some unlicensed applications enabled on the sufferer’s tool. The alert then demands the user to pay the ransom money.
Faulty declarations regarding prohibited content.
In nations where software piracy is much less popular, this method is not as effective for the cyber frauds. Conversely, the Win32/Filecoder.ODCODC.C popup alert may wrongly declare to be deriving from a police institution and also will certainly report having situated youngster pornography or other unlawful data on the device.
Win32/Filecoder.ODCODC.C popup alert might incorrectly claim to be deriving from a law enforcement institution and also will certainly report having situated youngster porn or other unlawful information on the tool. The alert will in a similar way include a need for the user to pay the ransom.
Technical details
File Info:
crc32: 4FB95FF0md5: fc29e3361900783404010daa0adbc5f8name: FC29E3361900783404010DAA0ADBC5F8.mlwsha1: a7c3da6df215ff68aedbd84215021b24cb2b2f3asha256: 96c99ac61a86e460c482658a29d728baa11ba223c1a85f402e0bfc94110ff86fsha512: 8348abeddfeafcab6bffcc935ba72722b5b17ed7870f3dafdc3f0599ac144f628474a59d9a982b392db04c11c69ce60d242850127013ea5ec64a03aa009468ccssdeep: 3072:YWjPppAPFvJgQoMNQ+78vShndj1rppTAguJjJUY1gyW1Dyl+fworsk8BYgBdgGy:YuPPStZDddjT1APJdUY1gDYl+yconqtype: PE32 executable (GUI) Intel 80386, for MS WindowsVersion Info:
0: [No Data]
Win32/Filecoder.ODCODC.C also known as:
| GridinSoft | Trojan.Ransom.Gen |
| Bkav | W32.AIDetect.malware2 |
| K7AntiVirus | Trojan ( 0055e3ef1 ) |
| Elastic | malicious (high confidence) |
| DrWeb | Trojan.DownLoader23.35380 |
| Cynet | Malicious () |
| ALYac | Trojan.Ransom.Odcodc |
| Cylance | Unsafe |
| Zillya | Trojan.Filecoder.Win32.3989 |
| Sangfor | Trojan.Win32.Malex.gen |
| CrowdStrike | win/malicious_confidence_70% (W) |
| Alibaba | Trojan:Win32/Malex.db5ab733 |
| K7GW | Trojan ( 0055e3ef1 ) |
| Cybereason | malicious.619007 |
| Symantec | ML.Attribute.HighConfidence |
| ESET-NOD32 | a variant of Win32/Filecoder.ODCODC.C |
| APEX | Malicious |
| Avast | Win32:Malware-gen |
| Kaspersky | UDS:DangerousObject.Multi.Generic |
| BitDefender | Gen:Heur.Ransom.REntS.Gen.1 |
| NANO-Antivirus | Trojan.Win32.Filecoder.ejyzey |
| MicroWorld-eScan | Gen:Heur.Ransom.REntS.Gen.1 |
| Tencent | Win32.Trojan.Filecoder.Ednl |
| Ad-Aware | Gen:Heur.Ransom.REntS.Gen.1 |
| Sophos | Mal/Generic-S |
| Comodo | Malware@#qftymrih7l07 |
| BitDefenderTheta | Gen:NN.ZexaF.34686.xuW@aG0Beali |
| VIPRE | Trojan.Win32.Generic!BT |
| TrendMicro | Ransom_CRIPTODC.F116LR |
| McAfee-GW-Edition | BehavesLike.Win32.Generic.fh |
| FireEye | Generic.mg.fc29e33619007834 |
| Emsisoft | Gen:Heur.Ransom.REntS.Gen.1 (B) |
| SentinelOne | Static AI – Suspicious PE |
| Jiangmin | Trojan.Generic.apwah |
| Webroot | W32.Trojan.Gen |
| Avira | TR/AD.Malex.xkbeo |
| eGambit | Unsafe.AI_Score_99% |
| Kingsoft | Win32.Troj.Undef.(kcloud) |
| Microsoft | Trojan:Win32/Malex.gen!E |
| AegisLab | Trojan.Win32.Generic.4!c |
| ZoneAlarm | HEUR:Trojan.Win32.Generic |
| GData | Gen:Heur.Ransom.REntS.Gen.1 |
| AhnLab-V3 | Malware/Win32.Generic.C1473723 |
| McAfee | Artemis!FC29E3361900 |
| MAX | malware (ai score=100) |
| VBA32 | BScope.TrojanRansom.Agent |
| Panda | Trj/GdSda.A |
| TrendMicro-HouseCall | Ransom_CRIPTODC.F116LR |
| Rising | Ransom.FileCryptor!8.1A7 (CLOUD) |
| Ikarus | Trojan.Win32.Filecoder |
| Fortinet | W32/Generic.AP.3BCA4!tr |
| AVG | Win32:Malware-gen |
| Paloalto | generic.ml |

