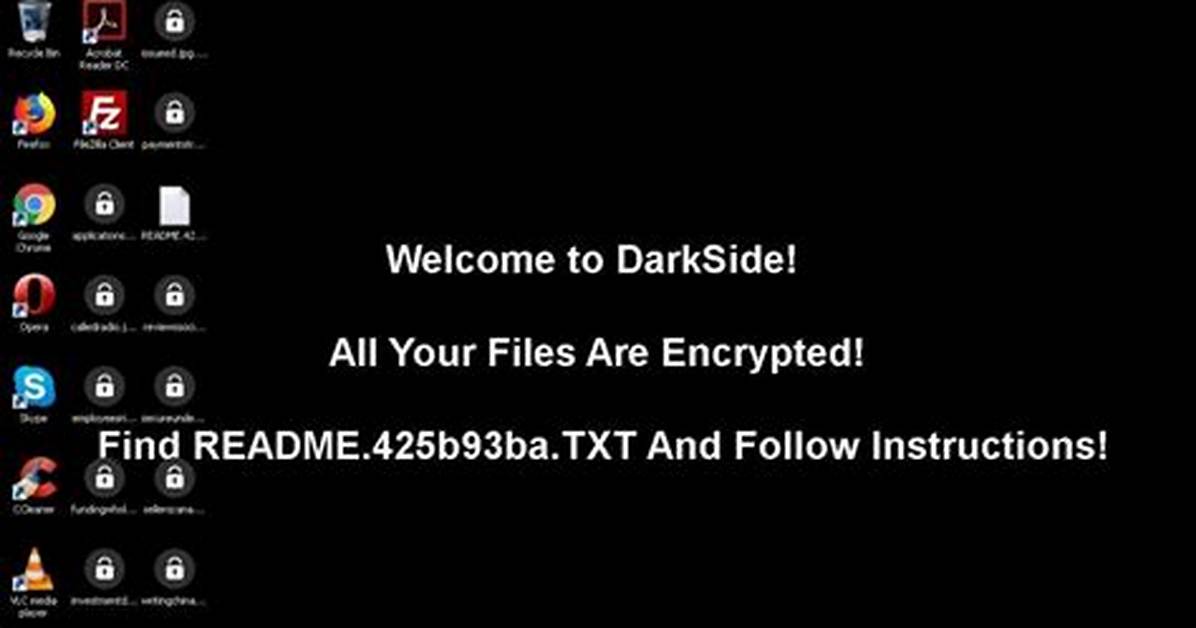
What is Win32/Filecoder.DarkSide.A infection?
In this article you will discover about the definition of Win32/Filecoder.DarkSide.A and also its negative effect on your computer system. Such ransomware are a type of malware that is clarified by on-line fraudulences to require paying the ransom by a sufferer.
Most of the situations, Win32/Filecoder.DarkSide.A infection will certainly advise its victims to launch funds transfer for the function of counteracting the changes that the Trojan infection has introduced to the sufferer’s device.
Win32/Filecoder.DarkSide.A Summary
These adjustments can be as adheres to:
- Executable code extraction. Cybercriminals often use binary packers to hinder the malicious code from reverse-engineered by malware analysts. A packer is a tool that compresses, encrypts, and modifies a malicious file’s format. Sometimes packers can be used for legitimate ends, for example, to protect a program against cracking or copying.
- At least one process apparently crashed during execution;
- A process attempted to delay the analysis task.;
- Reads data out of its own binary image. The trick that allows the malware to read data out of your computer’s memory.
Everything you run, type, or click on your computer goes through the memory. This includes passwords, bank account numbers, emails, and other confidential information. With this vulnerability, there is the potential for a malicious program to read that data.
- Attempts to stop active services;
- Crashed cuckoomon during analysis. Report this error to the Github repo.;
- Attempts to repeatedly call a single API many times in order to delay analysis time. This significantly complicates the work of the virus analyzer. Typical malware tactics!
- Collects information to fingerprint the system. There are behavioral human characteristics that can be used to digitally identify a person to grant access to systems, devices, or data. Unlike passwords and verification codes, fingerprints are fundamental parts of user’s identities. Among the threats blocked on biometric data processing and storage systems is spyware, the malware used in phishing attacks (mostly spyware downloaders and droppers), ransomware, and Banking Trojans as posing the greatest danger.
- Anomalous binary characteristics. This is a way of hiding virus’ code from antiviruses and virus’ analysts.
- Ciphering the papers located on the victim’s hard disk drive — so the victim can no longer use the data;
- Preventing routine accessibility to the sufferer’s workstation. This is the typical behavior of a virus called locker. It blocks access to the computer until the victim pays the ransom.
| catsdegree.com | Gen:Heur.Ransom.RTH.1 |
Win32/Filecoder.DarkSide.A
One of the most common channels where Win32/Filecoder.DarkSide.A are infused are:
- By ways of phishing e-mails;
- As a repercussion of user winding up on a source that hosts a harmful software application;
As quickly as the Trojan is effectively injected, it will certainly either cipher the data on the sufferer’s PC or stop the tool from operating in a proper fashion – while likewise positioning a ransom note that points out the requirement for the targets to impact the repayment for the objective of decrypting the files or recovering the data system back to the initial problem. In a lot of instances, the ransom money note will show up when the customer reboots the COMPUTER after the system has actually currently been damaged.
Win32/Filecoder.DarkSide.A circulation networks.
In numerous edges of the globe, Win32/Filecoder.DarkSide.A expands by jumps and bounds. Nevertheless, the ransom notes and also tricks of obtaining the ransom money quantity might vary depending on particular neighborhood (regional) setups. The ransom money notes and also methods of obtaining the ransom money quantity might vary depending on certain regional (local) settings.
As an example:
Faulty notifies regarding unlicensed software.
In particular areas, the Trojans often wrongfully report having actually discovered some unlicensed applications enabled on the victim’s tool. The alert then demands the individual to pay the ransom money.
Faulty declarations concerning prohibited content.
In countries where software application piracy is less popular, this method is not as efficient for the cyber frauds. Alternatively, the Win32/Filecoder.DarkSide.A popup alert might incorrectly claim to be deriving from a police organization and also will report having located child pornography or other illegal data on the device.
Win32/Filecoder.DarkSide.A popup alert might wrongly claim to be obtaining from a law enforcement organization and will report having situated kid pornography or other prohibited data on the device. The alert will similarly contain a need for the individual to pay the ransom.
Technical details
File Info:
crc32: BC2B957Bmd5: 04fde4340cc79cd9e61340d4c1e8ddfbname: 04FDE4340CC79CD9E61340D4C1E8DDFB.mlwsha1: 88fc623483f7ffe57f986ed10789e6723083fcd8sha256: 8cfd28911878af048fb96b6cc0b9da770542576d5c2b20b193c3cfc4bde4d3bcsha512: 105ddfb8bbfedc8460fb1e6d26c6cd02ea81bfdc12a196c1c2f8e52bc73faf03a688339b4c231ab5b5b3885f2ad248115c32c95fc64e84462a16c3e237e6fc9cssdeep: 768:TTjagICPhDt3bS4nyz2CuwSbV5dNcxGV1yldoZrY23W5o:BpDtG4nMpboDTV1ylVZ5type: PE32 executable (GUI) Intel 80386, for MS WindowsVersion Info:
0: [No Data]
Win32/Filecoder.DarkSide.A also known as:
| GridinSoft | Trojan.Ransom.Gen |
| Bkav | W32.AIDetect.malware1 |
| K7AntiVirus | Trojan ( 005762ca1 ) |
| Elastic | malicious (high confidence) |
| DrWeb | Trojan.Encoder.33499 |
| Cynet | Malicious () |
| ALYac | Gen:Heur.Ransom.RTH.1 |
| Cylance | Unsafe |
| CrowdStrike | win/malicious_confidence_100% (W) |
| K7GW | Trojan ( 005762ca1 ) |
| Cybereason | malicious.40cc79 |
| Symantec | ML.Attribute.HighConfidence |
| ESET-NOD32 | a variant of Win32/Filecoder.DarkSide.A |
| APEX | Malicious |
| Avast | Win32:Trojan-gen |
| ClamAV | Win.Packed.DarkSide-9262656-0 |
| Kaspersky | HEUR:Trojan.Win32.Generic |
| BitDefender | Gen:Heur.Ransom.RTH.1 |
| MicroWorld-eScan | Gen:Heur.Ransom.RTH.1 |
| Ad-Aware | Gen:Heur.Ransom.RTH.1 |
| Sophos | Mal/Generic-S |
| F-Secure | |
| BitDefenderTheta | AI:Packer.D6E5D0271E |
| TrendMicro | Ransom.Win32.DARKSIDE.SMYAAK-B |
| McAfee-GW-Edition | GenericRXNS-CM!04FDE4340CC7 |
| FireEye | Generic.mg.04fde4340cc79cd9 |
| Emsisoft | Gen:Heur.Ransom.RTH.1 (B) |
| SentinelOne | Static AI – Malicious PE |
| Jiangmin | Trojan.Generic.gttmr |
| Avira | TR/Crypt.XPACK.Gen |
| eGambit | Trojan.Generic |
| Antiy-AVL | Trojan[Ransom]/Win32.DarkSide |
| Microsoft | Ransom:Win32/DarkSide.DA!MTB |
| Arcabit | Trojan.Ransom.RTH.1 |
| ZoneAlarm | HEUR:Trojan.Win32.Generic |
| GData | Gen:Heur.Ransom.RTH.1 |
| AhnLab-V3 | Trojan/Win32.FileCoder.C4338100 |
| McAfee | GenericRXNS-CM!04FDE4340CC7 |
| MAX | malware (ai score=82) |
| VBA32 | BScope.Trojan.Diple |
| Malwarebytes | Ransom.DarkSide |
| TrendMicro-HouseCall | Ransom.Win32.DARKSIDE.SMYAAK-B |
| Rising | Trojan.Filecoder!8.68 (C64:YzY0OrFqPD/kdqW8) |
| Ikarus | Trojan-Ransom.DarkSide |
| Fortinet | W32/Filecoder.ODE!tr.ransom |
| AVG | Win32:Trojan-gen |
| Qihoo-360 | HEUR/QVM20.1.94AF.Malware.Gen |

