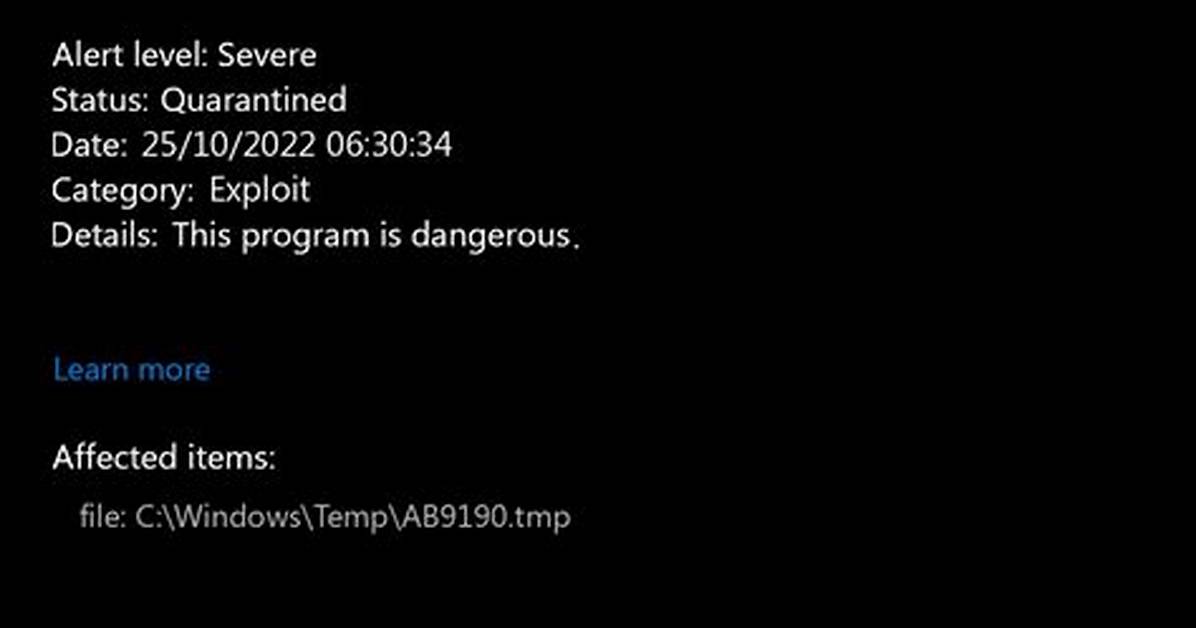
Any type of malware exists with the only target – make money on you1. And the programmers of these things are not thinking of morality – they utilize all possible tactics. Stealing your personal data, receiving the comission for the banners you watch for them, exploiting your hardware to mine cryptocurrencies – that is not the full list of what they do. Do you want to be a riding horse? That is a rhetorical question.
What does the pop-up with Exploit:Script/ExchgProxyRequest.B detection mean?
The Exploit:Script/ExchgProxyRequest.B detection you can see in the lower right corner is demonstrated to you by Microsoft Defender. That anti-malware application is good at scanning, however, prone to be mainly unstable. It is unprotected to malware attacks, it has a glitchy user interface and bugged malware removal features. For this reason, the pop-up which says about the Exchange Proxy Request is simply a notification that Defender has actually found it. To remove it, you will likely need to make use of another anti-malware program.
The exact Exploit:Script/ExchgProxyRequest.B virus is a really nasty thing. Exploits are like open gates for various other viruses. They use the vulnerabilities in the programs you have installed on your PC. After exploring your system and recognizing all exploitable vulnerabilities, viruses like Exchange Proxy Request download other malware. The particular kind of malware can be any of the ones present nowadays – coin miners, backdoors or spyware, for example. Their activity is quiet, so you will definitely miss the instant when that malware commences its task. However, you will likely be sad to observe what happens to your computer when it downloads a payload of other viruses.
Exploit Summary:
| Name | Exchange Proxy Request Exploit |
| Detection | Exploit:Script/ExchgProxyRequest.B |
| Damage | Exchange Proxy Request exploit is gain access to a computer system and then install malware on it. |
| Similar | Trojan Nettool, Iishack, Generic, Js Kaixin, Wordperf, Hacktool Bat Winactive, Vbs Hlpmbox, Smee |
| Fix Tool | See If Your System Has Been Affected by Exchange Proxy Request exploit |
Is Exploit:Script/ExchgProxyRequest.B dangerous?
As I have pointed out , non-harmful malware does not exist. And Exploit:Script/ExchgProxyRequest.B is not an exception. Exploit will certainly complete its filthy task if you grant it a possibility. And the results of its activity will not make you pleased – tons of different malware will make your system entirely inoperative. Moreover, exploits like Exchange Proxy Request one often inject spyware and stealer malware. It means that not just the computer features, but also your personal privacy is in danger. It is exceptionally reckless to underrate the threat of exploits.
Exploits are just one of the most prevalent viruses used by cybercriminal groups that aim at enterprises. Injecting ransomware or spyware/stealers into a corporate network that has some basic safety elements enabled requires some initial interruptions. At the same time, they can easily be neutralized. A lot of the weakness in the applications are fixed in upcoming updates. Just install them – and make your system and your company network safe.

