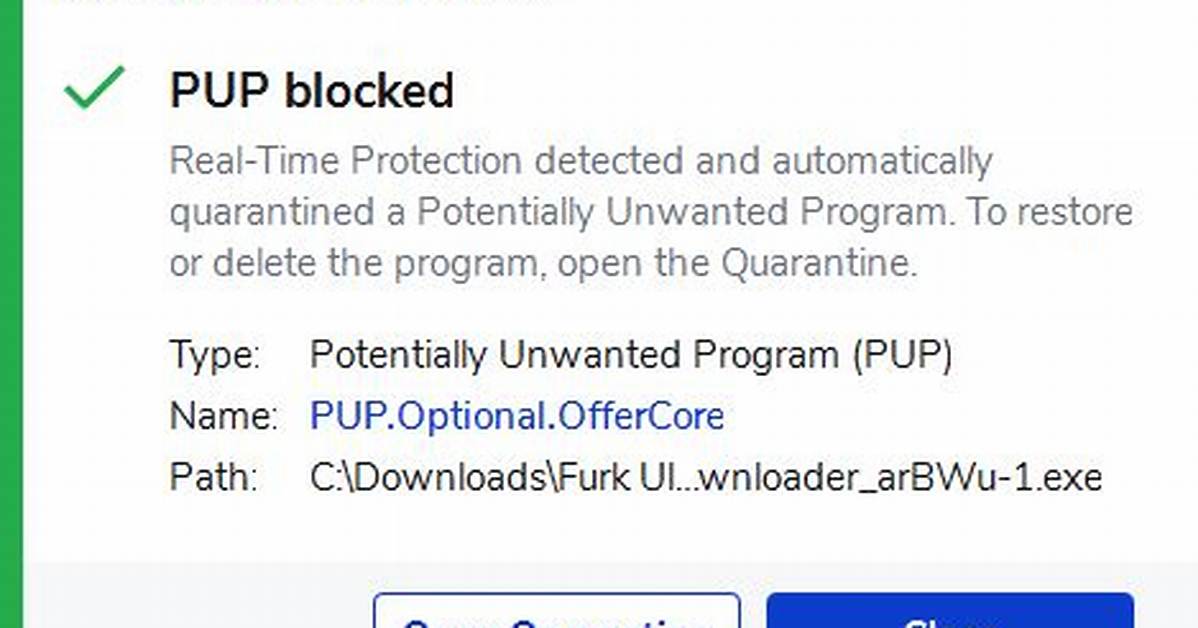
What is PUP.Optional.OfferCore infection?
In this post you will discover regarding the interpretation of PUP.Optional.OfferCore and also its unfavorable effect on your computer system. Such ransomware are a kind of malware that is clarified by on-line fraudulences to demand paying the ransom money by a sufferer.
In the majority of the situations, PUP.Optional.OfferCore infection will certainly instruct its sufferers to start funds transfer for the objective of reducing the effects of the modifications that the Trojan infection has presented to the sufferer’s device.
PUP.Optional.OfferCore Summary
These adjustments can be as follows:
- Behavioural detection: Executable code extraction – unpacking;
- Creates RWX memory;
- Possible date expiration check, exits too soon after checking local time;
- Dynamic (imported) function loading detected;
- Reads data out of its own binary image;
- The binary contains an unknown PE section name indicative of packing;
- Authenticode signature is invalid;
- Anomalous binary characteristics;
- Ciphering the documents found on the victim’s hard drive — so the victim can no longer use the information;
- Preventing regular access to the target’s workstation;
PUP.Optional.OfferCore
The most normal networks through which PUP.Optional.OfferCore Trojans are injected are:
- By methods of phishing emails;
- As an effect of customer ending up on a source that holds a destructive software program;
As soon as the Trojan is effectively injected, it will certainly either cipher the information on the victim’s computer or protect against the tool from working in an appropriate manner – while also placing a ransom note that discusses the requirement for the sufferers to effect the settlement for the purpose of decrypting the files or recovering the file system back to the initial problem. In a lot of circumstances, the ransom note will certainly turn up when the customer restarts the COMPUTER after the system has actually already been damaged.
PUP.Optional.OfferCore distribution channels.
In numerous edges of the world, PUP.Optional.OfferCore expands by leaps and bounds. Nonetheless, the ransom money notes as well as techniques of obtaining the ransom money amount may differ relying on particular neighborhood (local) settings. The ransom notes as well as techniques of extorting the ransom amount may differ depending on particular local (regional) settings.
For example:
Faulty signals concerning unlicensed software program.
In particular locations, the Trojans commonly wrongfully report having spotted some unlicensed applications enabled on the victim’s tool. The alert then demands the user to pay the ransom money.
Faulty statements about prohibited web content.
In nations where software program piracy is much less preferred, this approach is not as reliable for the cyber fraudulences. Alternatively, the PUP.Optional.OfferCore popup alert might incorrectly claim to be deriving from a law enforcement organization and will report having situated kid pornography or other illegal information on the gadget.
PUP.Optional.OfferCore popup alert may incorrectly declare to be obtaining from a legislation enforcement institution and also will certainly report having situated child pornography or various other illegal data on the gadget. The alert will similarly have a demand for the individual to pay the ransom money.
Technical details
File Info:
name: E2BBC7C041C8915A6734.mlwpath: /opt/CAPEv2/storage/binaries/e5a5c17aeac26e604f634305268bb2898aea789bf7f9bb9797b0ca8a7f5e486fcrc32: C3525B1Bmd5: e2bbc7c041c8915a6734e60c7f86ba63sha1: 34c89101692f7e3e2ff1c53bc1fb33d71c23b797sha256: e5a5c17aeac26e604f634305268bb2898aea789bf7f9bb9797b0ca8a7f5e486fsha512: 3f8e3991b8716dda88451de4ad07f32a6db54909dadff4333ad07d7c83dd2f1222dc0a053d66685f77ae97e6214baa4d475c314cf15efc33ac57868162be243bssdeep: 49152:dqe3f6zP6QkO6U6HP6RbthjZT0B5Lnw/511:sSizP6Qk/U6iRbthNk54type: PE32 executable (GUI) Intel 80386, for MS Windowstlsh: T1B2C5C03BB2E8A13EC4EA4B32457392505B777A73E91A8C2A17F0450DCFE64601E3B6D5sha3_384: 163bce7c28d875303013bd5e553ac32edcdd53b8877a71e3d1584ec8b4c58fa2470caf6bc9aed97ce3873e87cf064152ep_bytes: 558bec83c4a453565733c08945c48945timestamp: 2020-11-15 09:48:30Version Info:
Comments: This installation was built with Inno Setup.CompanyName: FileDescription: Innova Media d.o.o. Download Manager FileVersion: 1.0.0 LegalCopyright: OriginalFileName: ProductName: Innova Media d.o.o. ProductVersion: 1.0.0 Translation: 0x0000 0x04b0
PUP.Optional.OfferCore also known as:
| GridinSoft | Trojan.Ransom.Gen |
| Elastic | malicious (high confidence) |
| MicroWorld-eScan | Application.Bundler.CSU |
| FireEye | Application.Bundler.CSU |
| ALYac | Application.Bundler.CSU |
| VIPRE | Trojan.Win32.Generic!BT |
| K7AntiVirus | Adware ( 00579f2a1 ) |
| K7GW | Adware ( 00579f2a1 ) |
| Cybereason | malicious.041c89 |
| Symantec | Trojan.Gen.MBT |
| ESET-NOD32 | Win32/OfferCore.A potentially unwanted |
| BitDefender | Application.Bundler.CSU |
| Avast | FileRepMalware |
| Ad-Aware | Application.Bundler.CSU |
| Sophos | Generic PUA DE (PUA) |
| DrWeb | Adware.Downware.19949 |
| McAfee-GW-Edition | Artemis!Trojan |
| Emsisoft | Application.Bundler.CSU (B) |
| MAX | malware (ai score=74) |
| Gridinsoft | Ransom.Win32.Sabsik.sa |
| Microsoft | Trojan:Win32/Sabsik.FL.B!ml |
| GData | Application.Bundler.CSU |
| AhnLab-V3 | Malware/Win.Generic.R421179 |
| McAfee | Artemis!E2BBC7C041C8 |
| VBA32 | Adware.Downware |
| Malwarebytes | PUP.Optional.OfferCore |
| SentinelOne | Static AI – Suspicious PE |
| Fortinet | Adware/OfferCore |
| AVG | FileRepMalware |
| CrowdStrike | win/malicious_confidence_60% (D) |

