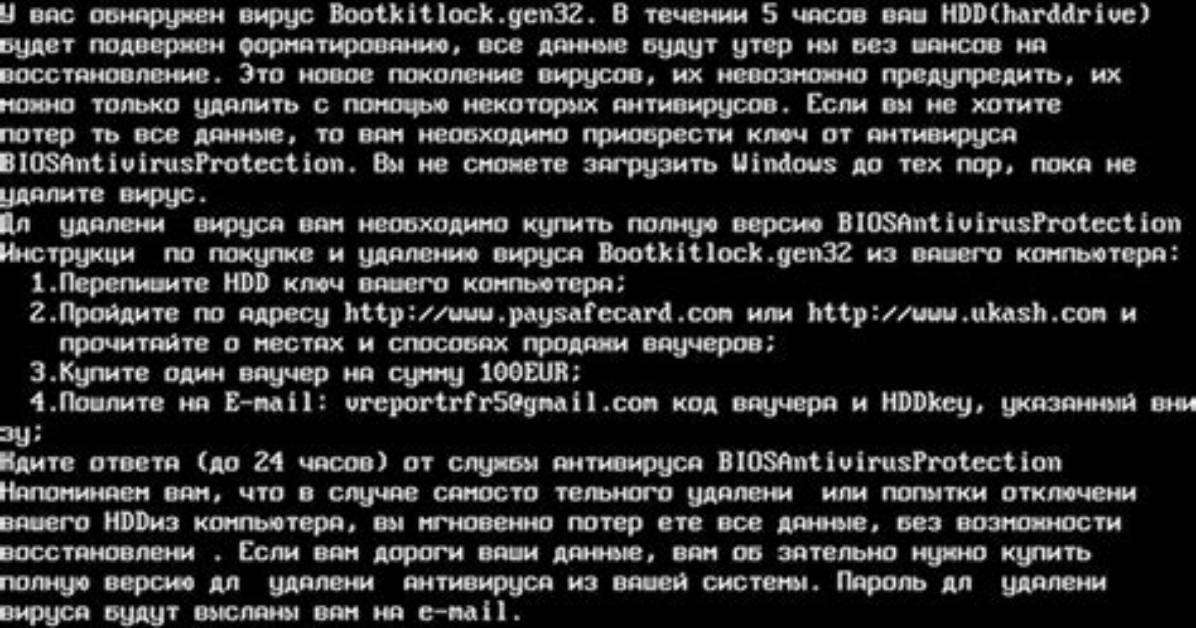
What is Trojan.MBRLock infection?
In this short article you will certainly discover regarding the interpretation of Trojan.MBRLock as well as its adverse impact on your computer. Such ransomware are a form of malware that is specified by on the internet fraudulences to require paying the ransom money by a victim.
In the majority of the instances, Trojan.MBRLock ransomware will certainly instruct its sufferers to initiate funds move for the purpose of neutralizing the changes that the Trojan infection has introduced to the victim’s device.
Trojan.MBRLock Summary
These alterations can be as complies with:
- Executable code extraction. Cybercriminals often use binary packers to hinder the malicious code from reverse-engineered by malware analysts. A packer is a tool that compresses, encrypts, and modifies a malicious file’s format. Sometimes packers can be used for legitimate ends, for example, to protect a program against cracking or copying.
- Creates RWX memory. There is a security trick with memory regions that allows an attacker to fill a buffer with a shellcode and then execute it. Filling a buffer with shellcode isn’t a big deal, it’s just data. The problem arises when the attacker is able to control the instruction pointer (EIP), usually by corrupting a function’s stack frame using a stack-based buffer overflow, and then changing the flow of execution by assigning this pointer to the address of the shellcode.
- Unconventionial binary language: Chinese (Simplified);
- Unconventionial language used in binary resources: Chinese (Simplified);
- The binary likely contains encrypted or compressed data. In this case, encryption is a way of hiding virus’ code from antiviruses and virus’ analysts.
- Likely installs a bootkit via raw harddisk modifications;
- Network activity detected but not expressed in API logs. Microsoft built an API solution right into its Windows operating system it reveals network activity for all apps and programs that ran on the computer in the past 30-days. This malware hides network activity.
- Anomalous binary characteristics. This is a way of hiding virus’ code from antiviruses and virus’ analysts.
- Ciphering the documents found on the target’s hard disk drive — so the sufferer can no more make use of the data;
- Preventing regular access to the victim’s workstation. This is the typical behavior of a virus called locker. It blocks access to the computer until the victim pays the ransom.
Trojan.MBRLock
The most normal channels where Trojan.MBRLock Trojans are infused are:
- By means of phishing e-mails;
- As a consequence of individual winding up on a source that holds a malicious software application;
As soon as the Trojan is efficiently injected, it will certainly either cipher the data on the victim’s PC or protect against the gadget from working in a correct manner – while likewise putting a ransom note that mentions the requirement for the victims to impact the settlement for the objective of decrypting the files or recovering the documents system back to the first condition. In a lot of instances, the ransom money note will certainly come up when the client restarts the PC after the system has currently been damaged.
Trojan.MBRLock circulation networks.
In different corners of the globe, Trojan.MBRLock grows by jumps and bounds. However, the ransom notes and also techniques of extorting the ransom money amount may differ depending on specific neighborhood (regional) setups. The ransom money notes and also techniques of extorting the ransom money amount may vary depending on specific regional (local) setups.
For instance:
Faulty notifies about unlicensed software application.
In certain locations, the Trojans commonly wrongfully report having actually identified some unlicensed applications enabled on the sufferer’s gadget. The alert after that requires the customer to pay the ransom money.
Faulty declarations about unlawful material.
In nations where software program piracy is much less popular, this technique is not as effective for the cyber frauds. Alternatively, the Trojan.MBRLock popup alert might wrongly declare to be stemming from a law enforcement organization and also will report having situated child porn or various other unlawful information on the device.
Trojan.MBRLock popup alert may wrongly assert to be acquiring from a law enforcement institution and will report having situated child pornography or various other unlawful information on the tool. The alert will likewise consist of a demand for the customer to pay the ransom.
Technical details
File Info:
crc32: 7279A00Fmd5: db169bde85ac40e6dcf4518eba23f0f1name: upload_filesha1: a1d18bed249c5a66a92f5437293fb873172456casha256: d40b1bfac0717d700a2a2dfae70e335827d022fb0f61043d9f565fb71f04df1esha512: 50428c06ca9cfc0b2f705da52f4cc71188b45d377311ce145cbc31a80129ab67c85edf549017e3e8362024fc380d6415dce61588f377fb49cbab40b2927d6383ssdeep: 24576:gJ0sl0pLkTe37Kiug3CKw1HqOY8fWqHW23Dp75Ht3NYLRRy5YkeD++7yw:gMthbSvt7pWqHW2TLt3ORGPe1htype: PE32 executable (GUI) Intel 80386, for MS WindowsVersion Info:
LegalCopyright: x4f5cx8005x7248x6743x6240x6709 x8bf7x5c0ax91cdx5e76x4f7fx7528x6b63x7248FileVersion: 1.0.0.0Comments: x672cx7a0bx5e8fx4f7fx7528x6613x8bedx8a00x7f16x5199()ProductName: x6613x8bedx8a00x7a0bx5e8fProductVersion: 1.0.0.0FileDescription: x9189x68a6Translation: 0x0804 0x04b0
Trojan.MBRLock also known as:
| GridinSoft | Trojan.Ransom.Gen |
| Bkav | W32.AIDetectVM.malware1 |
| Elastic | malicious (high confidence) |
| MicroWorld-eScan | Trojan.GenericKD.43955736 |
| FireEye | Generic.mg.db169bde85ac40e6 |
| CAT-QuickHeal | Trojan.DiskWriter |
| McAfee | GenericRXAA-AA!DB169BDE85AC |
| Cylance | Unsafe |
| VIPRE | Trojan.Win32.Generic!BT |
| Sangfor | Malware |
| K7AntiVirus | Trojan ( 005239691 ) |
| BitDefender | Trojan.GenericKD.43955736 |
| K7GW | Trojan ( 004b8a501 ) |
| Cybereason | malicious.d249c5 |
| TrendMicro | Trojan.Win32.WACATAC.USMANJ220 |
| Cyren | W32/S-e743b39f!Eldorado |
| Symantec | ML.Attribute.HighConfidence |
| APEX | Malicious |
| Avast | Win32:Malware-gen |
| Kaspersky | Trojan.Win32.DiskWriter.euf |
| Alibaba | Trojan:Win32/DiskWriter.ceffe62f |
| NANO-Antivirus | Trojan.Win32.DiskWriter.hynizq |
| Tencent | Win32.Trojan.Diskwriter.Wqwk |
| Ad-Aware | Trojan.GenericKD.43955736 |
| Emsisoft | Trojan.GenericKD.43955736 (B) |
| F-Secure | |
| DrWeb | Trojan.Siggen10.32538 |
| Zillya | Trojan.MBRlock.Win32.700 |
| Invincea | Mal/Generic-S |
| McAfee-GW-Edition | BehavesLike.Win32.Dropper.tc |
| Sophos | Mal/Generic-S |
| Ikarus | PUA.NoobyProtect |
| Jiangmin | Trojan/Generic.aptoz |
| Webroot | W32.WACATAC.USMANJ220 |
| Avira | HEUR/AGEN.1138441 |
| MAX | malware (ai score=99) |
| Microsoft | PUA:Win32/Vigua.A |
| Arcabit | Trojan.Generic.D29EB618 |
| ZoneAlarm | Trojan.Win32.DiskWriter.euf |
| GData | Win32.Application.PUPStudio.A |
| Cynet | Malicious () |
| Acronis | suspicious |
| BitDefenderTheta | Gen:NN.ZexaF.34298.vv0@aq@I5whb |
| ALYac | Trojan.Ransom.MBRlock |
| VBA32 | TScope.Malware-Cryptor.SB |
| Malwarebytes | Trojan.MBRLock |
| Panda | Trj/CI.A |
| ESET-NOD32 | Win32/MBRlock.BA |
| TrendMicro-HouseCall | Trojan.Win32.WACATAC.USMANJ220 |
| Rising | Trojan.Generic@ML.100 (RDML:ay12JYm/ayJhKjzLuREi9Q) |
| Yandex | Trojan.DiskWriter! |
| SentinelOne | DFI – Malicious PE |
| eGambit | Unsafe.AI_Score_100% |
| Fortinet | Riskware/MBRlock |
| AVG | Win32:Malware-gen |
| Paloalto | generic.ml |
| CrowdStrike | win/malicious_confidence_100% (W) |
| Qihoo-360 | Generic/Trojan.96f |

