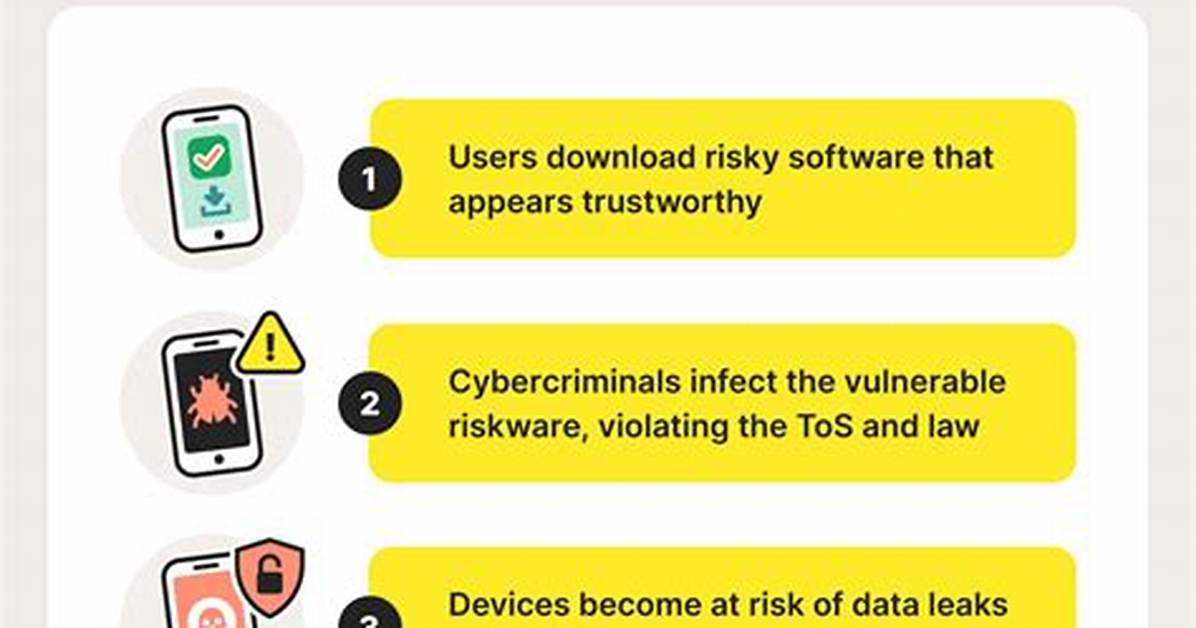
What is RiskWare.HackTool infection?
In this post you will discover regarding the interpretation of RiskWare.HackTool and also its adverse impact on your computer system. Such ransomware are a type of malware that is elaborated by online fraudulences to require paying the ransom by a victim.
Most of the cases, RiskWare.HackTool virus will advise its victims to launch funds transfer for the function of reducing the effects of the amendments that the Trojan infection has actually introduced to the sufferer’s device.
RiskWare.HackTool Summary
These adjustments can be as complies with:
- Uses Windows utilities for basic functionality;
- Anomalous binary characteristics;
- Ciphering the records located on the sufferer’s hard disk drive — so the victim can no longer utilize the information;
- Preventing regular accessibility to the victim’s workstation;
RiskWare.HackTool
The most common networks where RiskWare.HackTool Ransomware Trojans are injected are:
- By ways of phishing emails;
- As an effect of individual winding up on a source that holds a malicious software;
As quickly as the Trojan is effectively injected, it will either cipher the information on the victim’s computer or stop the gadget from functioning in a correct manner – while additionally placing a ransom money note that points out the requirement for the sufferers to effect the settlement for the purpose of decrypting the documents or recovering the file system back to the preliminary condition. In many circumstances, the ransom note will certainly turn up when the customer reboots the PC after the system has currently been damaged.
RiskWare.HackTool circulation networks.
In various corners of the globe, RiskWare.HackTool expands by leaps as well as bounds. Nonetheless, the ransom notes and also methods of extorting the ransom amount may vary relying on certain neighborhood (regional) setups. The ransom notes and tricks of extorting the ransom amount might vary depending on certain neighborhood (regional) setups.
For instance:
Faulty informs about unlicensed software program.
In certain areas, the Trojans typically wrongfully report having detected some unlicensed applications allowed on the victim’s gadget. The sharp then demands the customer to pay the ransom.
Faulty statements concerning unlawful material.
In nations where software program piracy is much less popular, this approach is not as efficient for the cyber frauds. Alternatively, the RiskWare.HackTool popup alert might incorrectly assert to be deriving from a police institution and will report having situated kid porn or other illegal data on the gadget.
RiskWare.HackTool popup alert might falsely declare to be acquiring from a regulation enforcement organization and will certainly report having situated kid pornography or other unlawful information on the tool. The alert will in a similar way include a demand for the individual to pay the ransom.
Technical details
File Info:
crc32: 3D39996Cmd5: 8510130a883f7e48782e895c84a80ebcname: 8510130A883F7E48782E895C84A80EBC.mlwsha1: 0f615a6c1cbc06fae118b4e043fab02d7f1c81aasha256: c3bca3b74f6525e3cba9eb931ed649fabfc5f77e804904893bc700ab585402b6sha512: 82c9d4b714065cbac8c521c94f5021668ce198abb8c3acf5814be3d16acbd9e388a2f5fd7f8931551ae39c77281271beb478c636cd5f3af8bd45127c4e137a75ssdeep: 1536:6PumNW1AD6eR6bcQpz/lYNnMJmsu0AhBBHMk/z0wVX6QTXdixhEZ/cstvsWjcdY:xmNkeIFyJMJRodjowX62lnqYIPtype: PE32 executable (console) Intel 80386, for MS WindowsVersion Info:
0: [No Data]
RiskWare.HackTool also known as:
| GridinSoft | Trojan.Ransom.Gen |
| DrWeb | Tool.Ipscan.6 |
| Cynet | Malicious () |
| CAT-QuickHeal | Trojan.Tiggre |
| ALYac | Trojan.GenericKD.46394970 |
| Cylance | Unsafe |
| Zillya | Tool.Agent.Win32.74180 |
| Sangfor | Trojan.Win32.GenericKD.32198805 |
| Alibaba | Ransom:Win32/Crysis.7d39775c |
| Symantec | ML.Attribute.HighConfidence |
| ClamAV | Win.Tool.ShareScanner-6827521-0 |
| BitDefender | Trojan.GenericKD.46394970 |
| MicroWorld-eScan | Trojan.GenericKD.46394970 |
| Tencent | Win32.Trojan.Agent.Dxwa |
| Ad-Aware | Trojan.GenericKD.46394970 |
| BitDefenderTheta | Gen:NN.ZexaF.34790.imW@aqK7mrl |
| VIPRE | Trojan.Win32.Generic!BT |
| McAfee-GW-Edition | Ransom-Crysis!8510130A883F |
| FireEye | Trojan.GenericKD.46394970 |
| Emsisoft | Trojan.GenericKD.46394970 (B) |
| Jiangmin | NetTool.Agent.hz |
| Webroot | W32.Malware.Gen |
| Microsoft | Ransom:Win32/Crysis |
| Arcabit | Trojan.Generic.D2C3EE5A |
| GData | Trojan.GenericKD.46394970 |
| AhnLab-V3 | Malware/Win32.Generic.C3093798 |
| MAX | malware (ai score=99) |
| Malwarebytes | RiskWare.HackTool |
| Panda | Trj/GdSda.A |
| TrendMicro-HouseCall | HKTL_NETSHARE |
| Rising | HackTool.NetScan!1.CABE (CLASSIC) |
| Ikarus | Trojan-Ransom.Crysis |
| MaxSecure | Trojan.Malware.300983.susgen |
| Fortinet | W32/PossibleThreat |
| AVG | FileRepMalware |
| Qihoo-360 | Win32/Trojan.Generic.HgIASRAA |

