What is Win32/Filecoder.BH infection?
In this article you will certainly discover concerning the definition of Win32/Filecoder.BH and also its negative impact on your computer system. Such ransomware are a kind of malware that is clarified by on-line frauds to require paying the ransom money by a victim.
Most of the instances, Win32/Filecoder.BH virus will advise its sufferers to launch funds move for the function of neutralizing the changes that the Trojan infection has introduced to the target’s device.
Win32/Filecoder.BH Summary
These modifications can be as follows:
- Attempts to connect to a dead IP:Port (1 unique times);
- A process attempted to delay the analysis task.;
- Repeatedly searches for a not-found process, may want to run with startbrowser=1 option;
- Reads data out of its own binary image. The trick that allows the malware to read data out of your computer’s memory.
Everything you run, type, or click on your computer goes through the memory. This includes passwords, bank account numbers, emails, and other confidential information. With this vulnerability, there is the potential for a malicious program to read that data.
- A process created a hidden window;
- Drops a binary and executes it. Trojan-Downloader installs itself to the system and waits until an Internet connection becomes available to connect to a remote server or website in order to download additional malware onto the infected computer.
- HTTP traffic contains suspicious features which may be indicative of malware related traffic;
- Performs some HTTP requests;
- The binary likely contains encrypted or compressed data. In this case, encryption is a way of hiding virus’ code from antiviruses and virus’ analysts.
- Attempts to remove evidence of file being downloaded from the Internet;
- Installs itself for autorun at Windows startup. There is simple tactic using the Windows startup folder located at:
C:\Users\[user-name]\AppData\Roaming\Microsoft\Windows\StartMenu\Programs\Startup. Shortcut links (.lnk extension) placed in this folder will cause Windows to launch the application each time [user-name] logs into Windows.The registry run keys perform the same action, and can be located in different locations:
- HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Run
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run
- HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\RunOnce
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\RunOnce
- Creates a hidden or system file. The malware adds the hidden attribute to every file and folder on your system, so it appears as if everything has been deleted from your hard drive.
- Likely virus infection of existing system binary;
- Operates on local firewall’s policies and settings;
- Creates a copy of itself;
- Attempts to disable UAC.
User Account Control or just UAC is a part of the Windows security system which prevents apps from making unwanted changes on PC.
UAC includes several technologies 1:
- File and egistry Virtualization;
- Same-desktop Elevation;
- Filtered Token;
- User Interface Privilege Isolation;
- Protected Mode Internet Explorer;
- Installer Detection;
- Attempts to disable Windows Defender;
- Attempts to modify or disable Security Center warnings;
- Ciphering the documents situated on the target’s hard drive — so the target can no longer use the data;
- Preventing normal accessibility to the victim’s workstation;
| z.whorecord.xyz | GenPack:Trojan.Ransom.ABZ |
| a.tomx.xyz | GenPack:Trojan.Ransom.ABZ |
| viweabkkfe.com | GenPack:Trojan.Ransom.ABZ |
| lscyqrjofqmtn.com | GenPack:Trojan.Ransom.ABZ |
| ltcfpuctidqqqxxzpikz.com | GenPack:Trojan.Ransom.ABZ |
| wowsfhnnvlwhlotryvh.com | GenPack:Trojan.Ransom.ABZ |
| linbzxpkmdtngnbdg.com | GenPack:Trojan.Ransom.ABZ |
| sjytgtnkdl.com | GenPack:Trojan.Ransom.ABZ |
| zkkfpkbbfnmihohix.com | GenPack:Trojan.Ransom.ABZ |
| vjuxtixi.com | GenPack:Trojan.Ransom.ABZ |
| ntrshvquunyzxevkucs.com | GenPack:Trojan.Ransom.ABZ |
| lxpcmncky.com | GenPack:Trojan.Ransom.ABZ |
| pjgnhujlmwtgf.com | GenPack:Trojan.Ransom.ABZ |
| pvqwziehrqscosb.com | GenPack:Trojan.Ransom.ABZ |
| qxcrbliabignczlmuc.com | GenPack:Trojan.Ransom.ABZ |
| okenhqzgxngnkbwouvfm.com | GenPack:Trojan.Ransom.ABZ |
| oismeark.com | GenPack:Trojan.Ransom.ABZ |
| bfgtwvhgsibiufmcerl.com | GenPack:Trojan.Ransom.ABZ |
| wxluitpliymeoirc.com | GenPack:Trojan.Ransom.ABZ |
| mzwfwjayhom.com | GenPack:Trojan.Ransom.ABZ |
| kvmihtamuopvagdlrwzg.com | GenPack:Trojan.Ransom.ABZ |
| rtlwqvhwuisfnery.com | GenPack:Trojan.Ransom.ABZ |
| xzfqmrfmyuaxs.com | GenPack:Trojan.Ransom.ABZ |
| xtvklujmo.com | GenPack:Trojan.Ransom.ABZ |
| dxkirxfzwhnnah.com | GenPack:Trojan.Ransom.ABZ |
| vyeaukkyszhdeug.com | GenPack:Trojan.Ransom.ABZ |
| kcubcfuhwwn.com | GenPack:Trojan.Ransom.ABZ |
| cpejcogzznpudbsmaxxm.com | GenPack:Trojan.Ransom.ABZ |
| zvwbjvhfrkqciz.com | GenPack:Trojan.Ransom.ABZ |
| pnqclaedmavju.com | GenPack:Trojan.Ransom.ABZ |
| kwsrmhroj.com | GenPack:Trojan.Ransom.ABZ |
| qwtzjokvjfvecysgypbd.com | GenPack:Trojan.Ransom.ABZ |
| avcctrnrxx.com | GenPack:Trojan.Ransom.ABZ |
| vgcdinjoj.com | GenPack:Trojan.Ransom.ABZ |
| towhyechciopdte.com | GenPack:Trojan.Ransom.ABZ |
| tmgskmvaxftffa.com | GenPack:Trojan.Ransom.ABZ |
| eiiveuuptweirgz.com | GenPack:Trojan.Ransom.ABZ |
| fryqhsblmvzsal.com | GenPack:Trojan.Ransom.ABZ |
| ohrpszrfydauhfuzyzbk.com | GenPack:Trojan.Ransom.ABZ |
| zbzxolintzi.com | GenPack:Trojan.Ransom.ABZ |
| fidkjesxq.com | GenPack:Trojan.Ransom.ABZ |
| owsxylebhmuzver.com | GenPack:Trojan.Ransom.ABZ |
| izaubgigwfl.com | GenPack:Trojan.Ransom.ABZ |
| yievjaklo.com | GenPack:Trojan.Ransom.ABZ |
| hqihrutpabwndvldae.com | GenPack:Trojan.Ransom.ABZ |
| nuepdkau.com | GenPack:Trojan.Ransom.ABZ |
| rjpkxiywinyhjoqltq.com | GenPack:Trojan.Ransom.ABZ |
| worazowxtkdznvvz.com | GenPack:Trojan.Ransom.ABZ |
| fzzxkhmkfunhotpjmdoy.com | GenPack:Trojan.Ransom.ABZ |
| kuyfpapjundhcit.com | GenPack:Trojan.Ransom.ABZ |
| nxcyhbauwgvdryyz.com | GenPack:Trojan.Ransom.ABZ |
| ajfdmjbywzibf.com | GenPack:Trojan.Ransom.ABZ |
Win32/Filecoder.BH
One of the most common channels through which Win32/Filecoder.BH Trojans are injected are:
- By methods of phishing emails;
- As a repercussion of user ending up on a resource that organizes a malicious software;
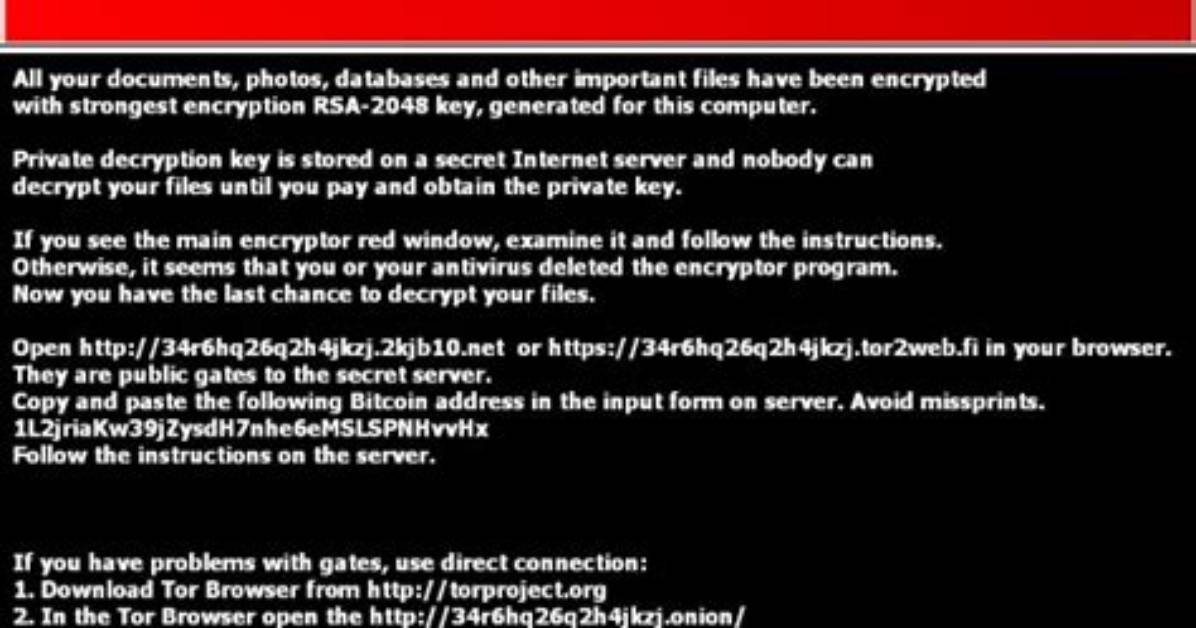
As soon as the Trojan is effectively infused, it will certainly either cipher the data on the target’s computer or avoid the gadget from operating in a correct fashion – while additionally putting a ransom note that points out the need for the targets to impact the settlement for the objective of decrypting the records or restoring the file system back to the first problem. In the majority of instances, the ransom note will certainly show up when the customer reboots the COMPUTER after the system has already been damaged.
Win32/Filecoder.BH distribution channels.
In various edges of the globe, Win32/Filecoder.BH grows by jumps and bounds. Nevertheless, the ransom money notes and also tricks of extorting the ransom money amount might vary depending upon specific regional (regional) setups. The ransom notes and techniques of obtaining the ransom money quantity might differ depending on particular regional (regional) settings.
For instance:
Faulty informs concerning unlicensed software program.
In specific areas, the Trojans often wrongfully report having actually detected some unlicensed applications made it possible for on the sufferer’s gadget. The sharp then demands the user to pay the ransom money.
Faulty statements about prohibited content.
In nations where software piracy is less preferred, this approach is not as reliable for the cyber scams. Alternatively, the Win32/Filecoder.BH popup alert may falsely declare to be deriving from a law enforcement institution and also will report having situated youngster pornography or other prohibited information on the device.
Win32/Filecoder.BH popup alert might incorrectly claim to be deriving from a regulation enforcement institution and will certainly report having located youngster pornography or other unlawful information on the gadget. The alert will likewise contain a need for the individual to pay the ransom.
Technical details
File Info:
crc32: 39FDB3C8md5: 7fb238f32b4e3804fd175d1a687d9611name: 7FB238F32B4E3804FD175D1A687D9611.mlwsha1: 2420bbc3b7352c57877622e2303bbe2b528d0796sha256: 75052ca1cf9c295f631979d111d6be4a27c15426e00b215583c6b2128b184547sha512: 4199bd264a2dad2f20cd4a702b02afe29ae346efa944d786642c0b757453617971316ab41f4b83aa6897899ca967c2d18027ca9063c99b434657185b33c7cc0fssdeep: 3072:YVOOJx1R5yAdd0cubb+gjPZ2KtjS+YIoBe5DE1Dx+IHIGLKnbFNOsKpjf:gOOtRrd0PyotjS+Yt9nHIGLINOHprtype: MS-DOS executable, MZ for MS-DOSVersion Info:
0: [No Data]
Win32/Filecoder.BH also known as:
| GridinSoft | Trojan.Ransom.Gen |
| Bkav | W32.AIDetect.malware1 |
| K7AntiVirus | Trojan ( 0044516f1 ) |
| Elastic | malicious (high confidence) |
| DrWeb | Trojan.Winlock.9241 |
| Cynet | Malicious () |
| ALYac | GenPack:Trojan.Ransom.ABZ |
| Cylance | Unsafe |
| Zillya | Trojan.Blocker.Win32.63628 |
| Sangfor | Trojan.Win32.Save.a |
| CrowdStrike | win/malicious_confidence_100% (W) |
| Alibaba | Ransom:Win32/Blocker.a54d0f7e |
| K7GW | Trojan ( 0044516f1 ) |
| Cybereason | malicious.32b4e3 |
| Cyren | W32/Ransom.HTLL-8465 |
| Symantec | ML.Attribute.HighConfidence |
| ESET-NOD32 | a variant of Win32/Filecoder.BH |
| APEX | Malicious |
| Avast | FileRepMalware |
| ClamAV | Win.Ransomware.Swed-9757258-0 |
| Kaspersky | Trojan-Ransom.Win32.Blocker.bqlz |
| BitDefender | GenPack:Trojan.Ransom.ABZ |
| NANO-Antivirus | Trojan.Win32.Blocker.idkjzn |
| MicroWorld-eScan | GenPack:Trojan.Ransom.ABZ |
| Tencent | Win32.Trojan.Raas.Auto |
| Ad-Aware | GenPack:Trojan.Ransom.ABZ |
| Sophos | Mal/Generic-R + Mal/TinyDL-T |
| Comodo | Malware@#3c4s85tcyu0xi |
| BitDefenderTheta | AI:Packer.1AB822821E |
| VIPRE | Trojan.Win32.Generic!BT |
| TrendMicro | TROJ_DIRCRYPT.K |
| McAfee-GW-Edition | BehavesLike.Win32.Generic.cc |
| FireEye | Generic.mg.7fb238f32b4e3804 |
| Emsisoft | GenPack:Trojan.Ransom.ABZ (B) |
| SentinelOne | Static AI – Malicious PE |
| Jiangmin | Trojan.Blocker.srq |
| Avira | TR/Crypt.XPACK.Gen |
| Microsoft | Ransom:Win32/Blocker |
| AegisLab | Trojan.Win32.GenericCryptor.m5oU |
| GData | GenPack:Trojan.Ransom.ABZ |
| Acronis | suspicious |
| McAfee | Artemis!7FB238F32B4E |
| MAX | malware (ai score=83) |
| VBA32 | Trojan.Agent |
| Panda | Trj/CI.A |
| TrendMicro-HouseCall | TROJ_DIRCRYPT.K |
| Rising | Ransom.Blocker!8.12A (CLOUD) |
| Yandex | Trojan.Blocker!tZo7CxxVvcs |
| Ikarus | Trojan-Ransom.FileCrypter |
| Fortinet | W32/Blocker.BH!tr.ransom |
| AVG | FileRepMalware |
| Paloalto | generic.ml |

