What is Win32/Filecoder.BTCware.I infection?
In this article you will certainly locate regarding the definition of Win32/Filecoder.BTCware.I and also its adverse impact on your computer system. Such ransomware are a kind of malware that is elaborated by on the internet fraudulences to demand paying the ransom money by a target.
Most of the situations, Win32/Filecoder.BTCware.I infection will certainly advise its sufferers to launch funds move for the objective of neutralizing the amendments that the Trojan infection has introduced to the sufferer’s gadget.
Win32/Filecoder.BTCware.I Summary
These alterations can be as adheres to:
- Installs itself for autorun at Windows startup. There is simple tactic using the Windows startup folder located at:
C:\Users\[user-name]\AppData\Roaming\Microsoft\Windows\StartMenu\Programs\Startup. Shortcut links (.lnk extension) placed in this folder will cause Windows to launch the application each time [user-name] logs into Windows.The registry run keys perform the same action, and can be located in different locations:
- HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Run
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run
- HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\RunOnce
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\RunOnce
- Exhibits possible ransomware file modification behavior;
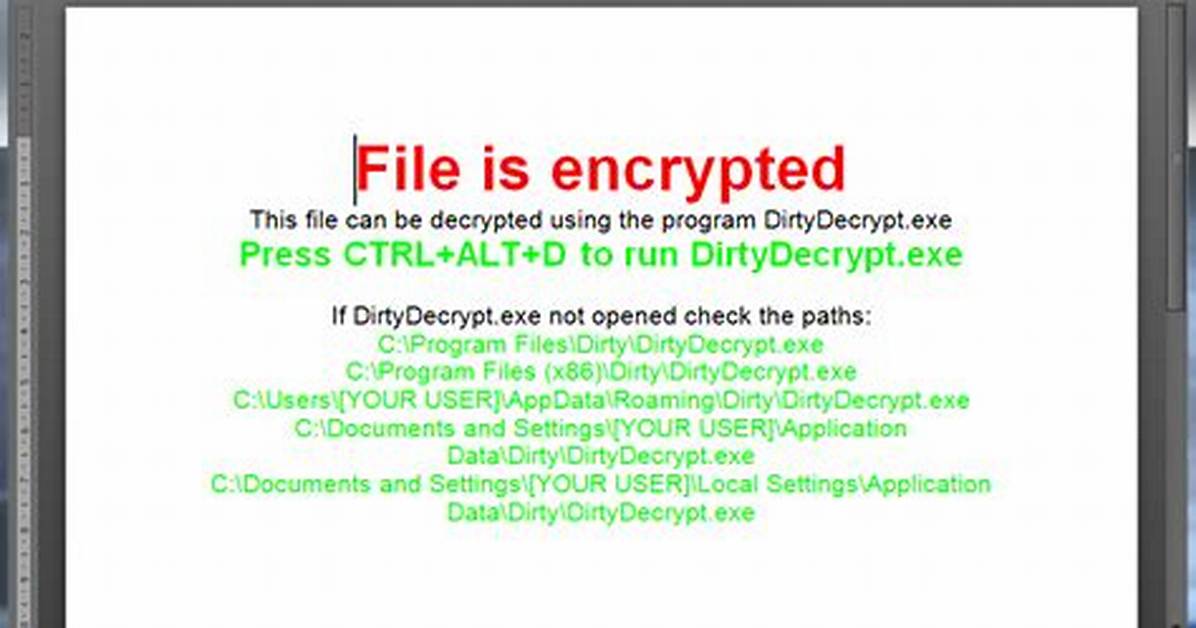
- Writes a potential ransom message to disk;
- Likely virus infection of existing system binary;
- Ciphering the records found on the sufferer’s hard disk — so the sufferer can no longer make use of the information;
- Preventing normal access to the victim’s workstation. This is the typical behavior of a virus called locker. It blocks access to the computer until the victim pays the ransom.
Win32/Filecoder.BTCware.I
One of the most normal networks where Win32/Filecoder.BTCware.I Ransomware are infused are:
- By methods of phishing emails;
- As a consequence of customer ending up on a resource that organizes a destructive software program;
As quickly as the Trojan is effectively injected, it will certainly either cipher the data on the target’s computer or stop the device from functioning in a proper way – while likewise putting a ransom note that mentions the demand for the targets to effect the settlement for the objective of decrypting the files or restoring the documents system back to the preliminary problem. In many circumstances, the ransom note will certainly come up when the customer restarts the PC after the system has already been harmed.
Win32/Filecoder.BTCware.I distribution channels.
In various corners of the globe, Win32/Filecoder.BTCware.I expands by leaps and also bounds. However, the ransom money notes and methods of obtaining the ransom money amount might differ depending on specific local (local) settings. The ransom notes and also techniques of extorting the ransom amount might vary depending on specific neighborhood (regional) setups.
For example:
Faulty alerts regarding unlicensed software.
In particular locations, the Trojans commonly wrongfully report having actually found some unlicensed applications allowed on the sufferer’s device. The alert then demands the individual to pay the ransom.
Faulty statements concerning prohibited content.
In countries where software application piracy is less prominent, this approach is not as effective for the cyber frauds. Alternatively, the Win32/Filecoder.BTCware.I popup alert may incorrectly declare to be stemming from a law enforcement establishment as well as will certainly report having situated kid pornography or other illegal data on the tool.
Win32/Filecoder.BTCware.I popup alert may falsely assert to be obtaining from a regulation enforcement institution and will report having located kid porn or various other illegal data on the tool. The alert will likewise have a requirement for the customer to pay the ransom money.
Technical details
File Info:
crc32: 9B7F0F6Dmd5: d09dae757d5520be686bc8e9b55b4992name: D09DAE757D5520BE686BC8E9B55B4992.mlwsha1: 64b76e2f81bb0771bc821acff6167e4da895445esha256: dffa308495b1c0e068693254a62a4a45f15d06568f3f8549911699f594db3ac6sha512: 29ff16c088a17fe422fffe27ea57d8c9f944e07add9bdd0f2d0f89ff5976a9a5b4bd370880e309cc5865e6b7e17d993678f7dd2e19029183b8927471a03d1bc0ssdeep: 1536:nRChFrXgcQ65H+GFmfQxZZ0LRxsXfpvfesp9fssWRcdIMV3gvWtJKlPz:nQxh5H5FvZ0LR+Xlfe29IMV3RtJ0Ptype: PE32 executable (GUI) Intel 80386, for MS WindowsVersion Info:
0: [No Data]
Win32/Filecoder.BTCware.I also known as:
| GridinSoft | Trojan.Ransom.Gen |
| Bkav | W32.AIDetect.malware2 |
| K7AntiVirus | Trojan ( 0050b0f71 ) |
| Elastic | malicious (high confidence) |
| DrWeb | Trojan.Encoder.11958 |
| Cynet | Malicious () |
| CAT-QuickHeal | Trojan.Generic |
| ALYac | Trojan.Ransom.BTCWare |
| Cylance | Unsafe |
| Zillya | Trojan.Filecoder.Win32.5926 |
| Sangfor | Trojan.Win32.Save.a |
| CrowdStrike | win/malicious_confidence_100% (W) |
| Alibaba | Ransom:Win32/Crusis.30fc8dee |
| K7GW | Trojan ( 0050b0f71 ) |
| Cybereason | malicious.57d552 |
| Cyren | W32/Ransom.GH.gen!Eldorado |
| Symantec | Ransom.BTCware |
| ESET-NOD32 | a variant of Win32/Filecoder.BTCware.I |
| APEX | Malicious |
| Avast | Win32:RansomX-gen [Ransom] |
| ClamAV | Win.Ransomware.Btcware-9778905-0 |
| Kaspersky | HEUR:Trojan.Win32.Generic |
| BitDefender | Generic.Ransom.BTCWare.F129DF71 |
| NANO-Antivirus | Trojan.Win32.Crusis.erpfsi |
| ViRobot | Trojan.Win32.S.Crypton.99840.V |
| SUPERAntiSpyware | |
| MicroWorld-eScan | Generic.Ransom.BTCWare.F129DF71 |
| Tencent | Win32.Trojan.Crusis.Wptd |
| Ad-Aware | Generic.Ransom.BTCWare.F129DF71 |
| Sophos | Mal/Generic-R + Troj/Btcware-A |
| Comodo | Malware@#33ffkya55lbm7 |
| BitDefenderTheta | Gen:NN.ZexaF.34608.guW@ayN9s0ei |
| VIPRE | Trojan.Win32.Generic!BT |
| TrendMicro | Ransom_GRYPHON.SM |
| McAfee-GW-Edition | Ransom-BTCWare!D09DAE757D55 |
| FireEye | Generic.mg.d09dae757d5520be |
| Emsisoft | Trojan.FileCoder (A) |
| SentinelOne | Static AI – Malicious PE |
| Webroot | W32.Trojan.Gen |
| Avira | HEUR/AGEN.1103387 |
| eGambit | Unsafe.AI_Score_99% |
| Kingsoft | Win32.Troj.Undef.(kcloud) |
| Microsoft | Ransom:Win32/Betisrypt.D |
| AegisLab | Adware.Win32.MegaSearch.lWQ3 |
| GData | Win32.Trojan-Ransom.BTCWare.I |
| AhnLab-V3 | Trojan/Win32.Gryphon.R205807 |
| McAfee | Ransom-BTCWare!D09DAE757D55 |
| MAX | malware (ai score=100) |
| VBA32 | BScope.TrojanRansom.Bitcovar |
| Panda | Trj/Genetic.gen |
| TrendMicro-HouseCall | Ransom_GRYPHON.SM |
| Rising | Ransom.Genasom!8.293 (CLOUD) |
| Yandex | Trojan.GenAsa!ZyCD9xkjazU |
| Ikarus | Trojan.Win32.Filecoder |
| Fortinet | W32/BTCWare.I!tr.ransom |
| AVG | Win32:RansomX-gen [Ransom] |
| Paloalto | generic.ml |
| Qihoo-360 | Win32/Ransom.CrySiS.HwoChu8A |

