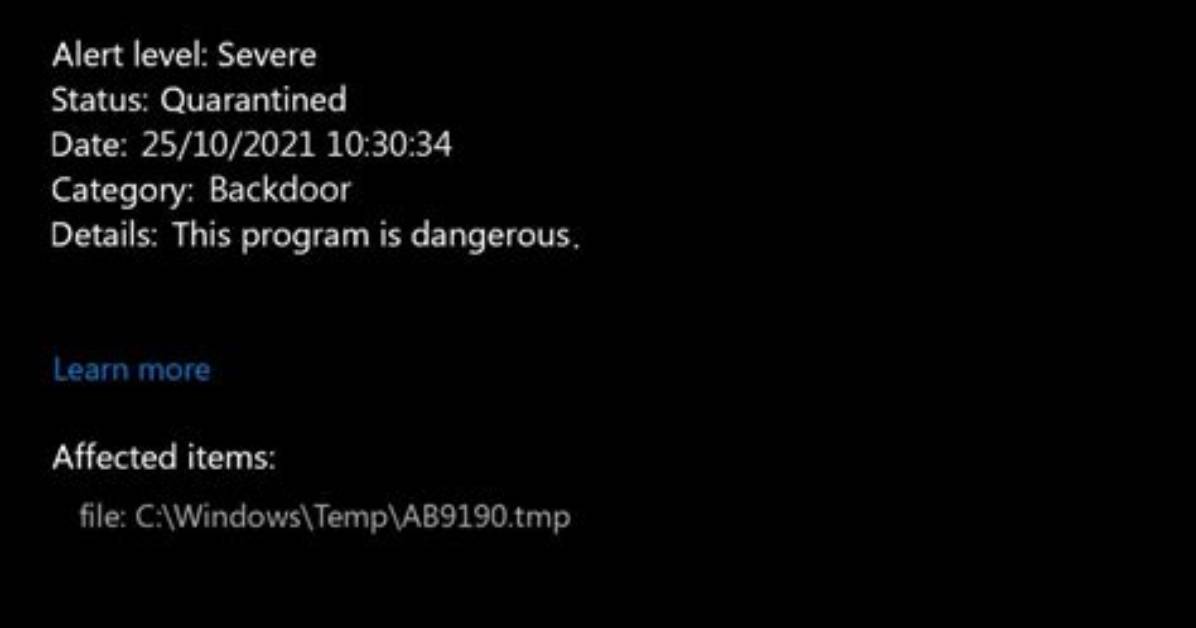
What is Backdoor:Win64/TurtleLoader.S infection?
In this post you will certainly discover about the interpretation of Backdoor:Win64/TurtleLoader.S and also its adverse impact on your computer system. Such ransomware are a form of malware that is specified by online fraudulences to require paying the ransom by a sufferer.
In the majority of the instances, Backdoor:Win64/TurtleLoader.S virus will certainly instruct its targets to launch funds move for the objective of neutralizing the amendments that the Trojan infection has actually introduced to the sufferer’s tool.
Backdoor:Win64/TurtleLoader.S Summary
These modifications can be as adheres to:
- Reads data out of its own binary image;
- Network activity detected but not expressed in API logs;
- Ciphering the documents situated on the target’s hard disk drive — so the sufferer can no more use the information;
- Preventing normal access to the target’s workstation;
Backdoor:Win64/TurtleLoader.S
The most normal networks where Backdoor:Win64/TurtleLoader.S Ransomware Trojans are injected are:
- By ways of phishing e-mails;
- As a repercussion of customer winding up on a resource that organizes a harmful software;
As soon as the Trojan is successfully infused, it will either cipher the information on the sufferer’s computer or protect against the gadget from working in a correct way – while likewise positioning a ransom money note that points out the requirement for the targets to impact the settlement for the objective of decrypting the papers or restoring the file system back to the initial problem. In most instances, the ransom money note will turn up when the customer restarts the PC after the system has currently been harmed.
Backdoor:Win64/TurtleLoader.S distribution networks.
In numerous edges of the world, Backdoor:Win64/TurtleLoader.S expands by jumps as well as bounds. Nevertheless, the ransom money notes and also tricks of obtaining the ransom money quantity might differ relying on certain local (regional) setups. The ransom notes and methods of extorting the ransom money amount might differ depending on certain local (local) setups.
For example:
Faulty informs concerning unlicensed software.
In particular areas, the Trojans typically wrongfully report having identified some unlicensed applications allowed on the target’s gadget. The alert after that demands the user to pay the ransom.
Faulty statements regarding illegal material.
In countries where software program piracy is less preferred, this technique is not as efficient for the cyber scams. Alternatively, the Backdoor:Win64/TurtleLoader.S popup alert might falsely claim to be originating from a law enforcement establishment and also will certainly report having situated child pornography or other unlawful information on the tool.
Backdoor:Win64/TurtleLoader.S popup alert might incorrectly assert to be obtaining from a law enforcement organization and also will report having situated child pornography or various other prohibited data on the gadget. The alert will similarly have a demand for the user to pay the ransom money.
Technical details
File Info:
crc32: DAECBE65md5: b48820db20dd1024866ae55117492a5cname: B48820DB20DD1024866AE55117492A5C.mlwsha1: 7da88b21bd1188bb90cbc15b5607ad03350eccbcsha256: ca538665cec05b30b8c868753cb3f7a09f974b3b1ba9583f968a9cee83c6454fsha512: cd34835933a8250ebdf6ddaff77ab44507c551331ff95c146abe0be8da0fe75d6e98cef87a7f01a956b154b0de1596290ef8a439c0bb54836aab7912fcf0315bssdeep: 196608:xfLUCgdUyeUSyhK9dWPU+oaoUXbB/mWylJTUHm4/ruB:xDdgayrSyk9yU+oaJ9fyldKCBtype: PE32 executable (GUI) Intel 80386, for MS WindowsVersion Info:
LegalCopyright: Copyright (c) 1999-2018 Igor PavlovInternalName: 7zS.sfxFileVersion: 19.00CompanyName: Igor PavlovProductName: 7-ZipProductVersion: 19.00FileDescription: 7z Setup SFXOriginalFilename: 7zS.sfx.exeTranslation: 0x0409 0x04b0
Backdoor:Win64/TurtleLoader.S also known as:
| GridinSoft | Trojan.Ransom.Gen |
| K7AntiVirus | Riskware ( 0040eff71 ) |
| DrWeb | Trojan.Siggen15.41726 |
| Cynet | Malicious () |
| CAT-QuickHeal | Trojan.SabsikIH.S21959152 |
| ALYac | Gen:Variant.Jaik.45735 |
| Cylance | Unsafe |
| K7GW | Riskware ( 0040eff71 ) |
| Cybereason | malicious.b20dd1 |
| Cyren | W64/Agent.DNH.gen!Eldorado |
| Symantec | ML.Attribute.HighConfidence |
| ESET-NOD32 | multiple detections |
| Avast | Win64:PWSX-gen [Trj] |
| ClamAV | Win.Packed.Barys-9859531-0 |
| Kaspersky | Trojan.Win32.Fabookie.abd |
| BitDefender | Gen:Variant.Jaik.45735 |
| MicroWorld-eScan | Gen:Variant.Jaik.45735 |
| Ad-Aware | Gen:Variant.Jaik.45735 |
| Sophos | Mal/Generic-S |
| BitDefenderTheta | Gen:NN.ZedlaF.34266.n88baOE@FOp |
| McAfee-GW-Edition | GenericRXQA-BO!96AB6B706F75 |
| FireEye | Gen:Variant.Jaik.45735 |
| Emsisoft | Gen:Variant.Jaik.45735 (B) |
| Jiangmin | Backdoor.Mokes.erv |
| Avira | TR/Crypt.XPACK.Gen7 |
| Antiy-AVL | Trojan/Generic.ASMalwS.34CE459 |
| Kingsoft | Win32.Hack.MSIL.bi.(kcloud) |
| Microsoft | Backdoor:Win64/TurtleLoader.S |
| GData | Gen:Variant.Jaik.45735 |
| McAfee | Artemis!B48820DB20DD |
| MAX | malware (ai score=82) |
| VBA32 | BScope.TrojanRansom.FileCryptor |
| Malwarebytes | Trojan.Dropper.SFX.Generic |
| TrendMicro-HouseCall | TROJ_GEN.R002C0DKF21 |
| Rising | Trojan.Starter!1.D93D (CLASSIC:QFEVA6vnUjBugBBo4rGVhQ) |
| Fortinet | W32/BSE.4Q7Q!tr |
| AVG | Win64:PWSX-gen [Trj] |

