.
Subsequently, one may also ask, what is Cross Site Scripting example?
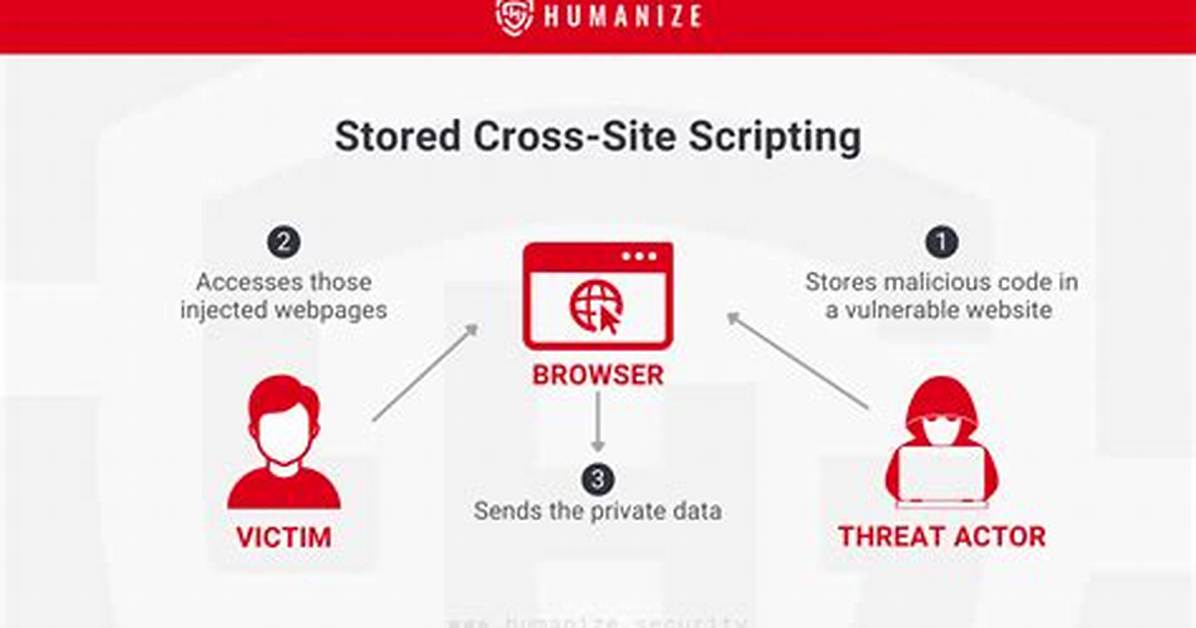
Overview. Cross-Site Scripting (XSS) attacks are a type of injection, in which malicious scripts are injected into otherwise benign and trusted websites. XSS attacks occur when an attacker uses a web application to send malicious code, generally in the form of a browser side script, to a different end user.
Beside above, what is cross site scripting and how can it be prevented? The first method you can and should use to prevent XSS vulnerabilities from appearing in your applications is by escaping user input. By escaping user input, key characters in the data received by a web page will be prevented from being interpreted in any malicious way.
Subsequently, one may also ask, what is the difference between persistent and non persistent cross site scripting attacks?
Non-persistent XSS - the main difference is that a web application doesn't store the malicious input in the database. A special case of non-persistent XSS is called - this type of attack is done without sending any DOM-based XSS requests to the web server. The attacker injects JavaScript code directly.
How does cross site scripting work?
Cross-site scripting works by manipulating a vulnerable web site so that it returns malicious JavaScript to users. When the malicious code executes inside a victim's browser, the attacker can fully compromise their interaction with the application.
What are the types of cross site scripting?
- Persistent XSS, where the malicious input originates from the website's database.
- Reflected XSS, where the malicious input originates from the victim's request.
- DOM-based XSS, where the vulnerability is in the client-side code rather than the server-side code.
Why is it called cross site scripting?

