.
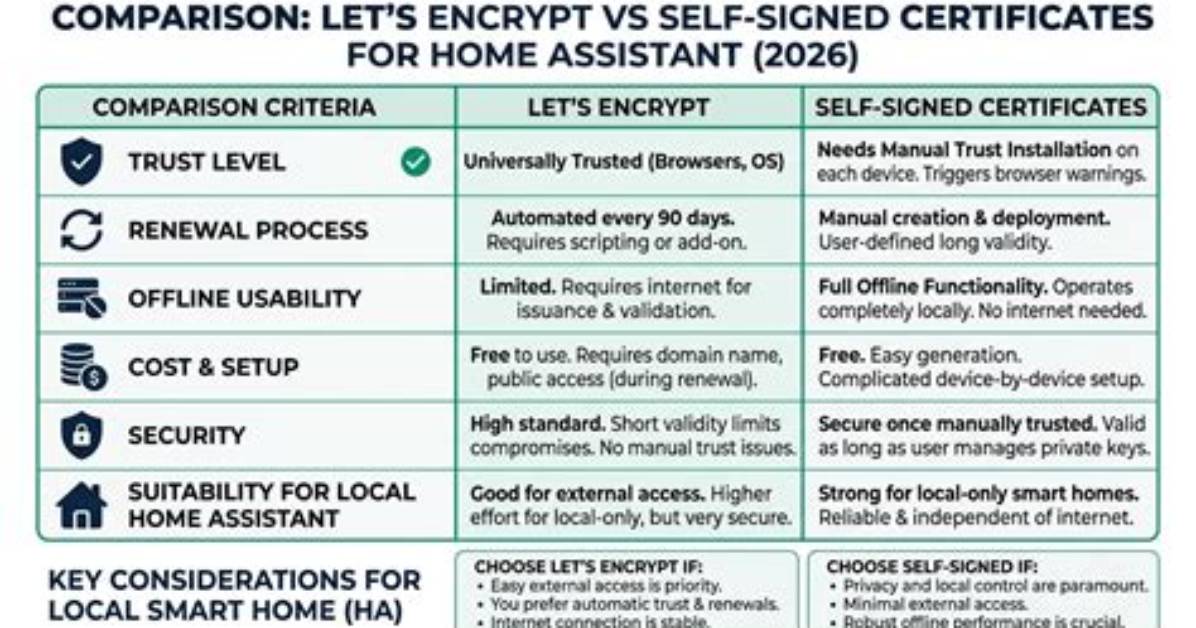
Also, are self signed certificates secure?
Unlike CA issued certificates, self-signed certificates are free of charge. While self-signed SSL Certificates also encrypt customers' log in and other personal account credentials, they prompt most web servers to display a security alert because the certificate was not verified by a trusted Certificate Authority.
One may also ask, can you use a self signed certificate for TLS? A self-signed certificate can be used for either HTTPS communication or SMTP/TLS. A self-signed certificate used for SMTP/TLS may not be recognized by some email servers. Many email servers require a certificate authority-signed certificate.
Keeping this in consideration, what is the risk of self signed certificates?
Risk of Using Self-Signed on Public Sites The security warnings associated with self-signed SSL Certificates drive away potential clients for fear that the website does not secure their credentials. Both brand reputation and customer trust are damaged.
How can I verify a self signed certificate?
When the certificate is presented for an entity to validate, they first verify the hash of the certificate matches the reference hash in the white-list, and if they match (indicating the self-signed certificate is the same as the one that was formally trusted) then the certificate's validity dates can be trusted.
Do self signed certificates expire?
What is the use of self signed certificate?

