.
In this manner, what is the use of syslog in Linux?
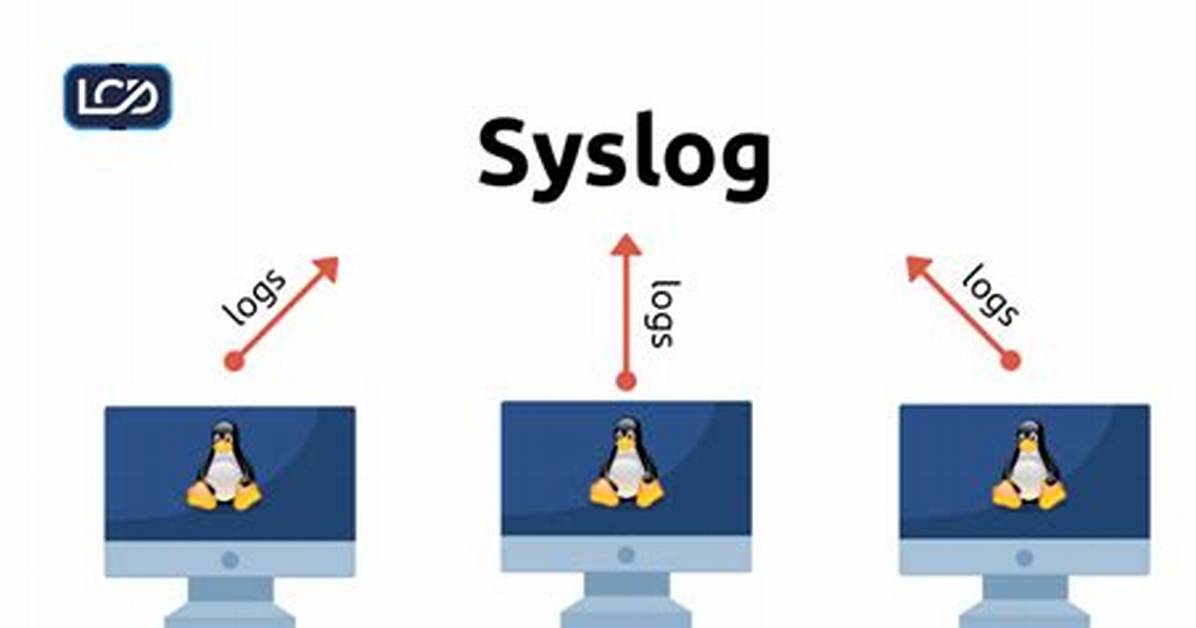
Syslog, is a standardized way (or Protocol) ofproducing and sending Log and Event information fromUnix/Linux and Windows systems (which produces Event Logs)and Devices (Routers, Firewalls, Switches, Servers, etc) over UDPPort 514 to a centralized Log/Event Message collector which isknown as a Syslog Server.
Additionally, what does syslog stand for? Syslog stands for System Logging Protocol, and isa way for network devices to send all types of logs and eventmessages from different machines to a centralized server forstorage, log monitoring, and analysis.
what is the role of the syslog daemon?
The syslog daemon is a server process thatprovides a message logging facility for application and systemprocesses. The syslog daemon is started by the InternetDaemon and receives messages on well-known port514.
What does syslog contain?
Syslog content (information contained inan event message) Syslog application (generates, interprets,routes and stores messages) Syslog transport (transmits themessages)
What is Kiwi Syslog?
Where is syslog on Linux?
- where some of the logs are dumped under a subdirectory likecups, samba, httpd.
- The configuration file for syslogd service is/etc/sysconfig/syslog.
- There you see two different group of options for:
- The default configuration file lists some options where we candescribe further:
- klogd options:

