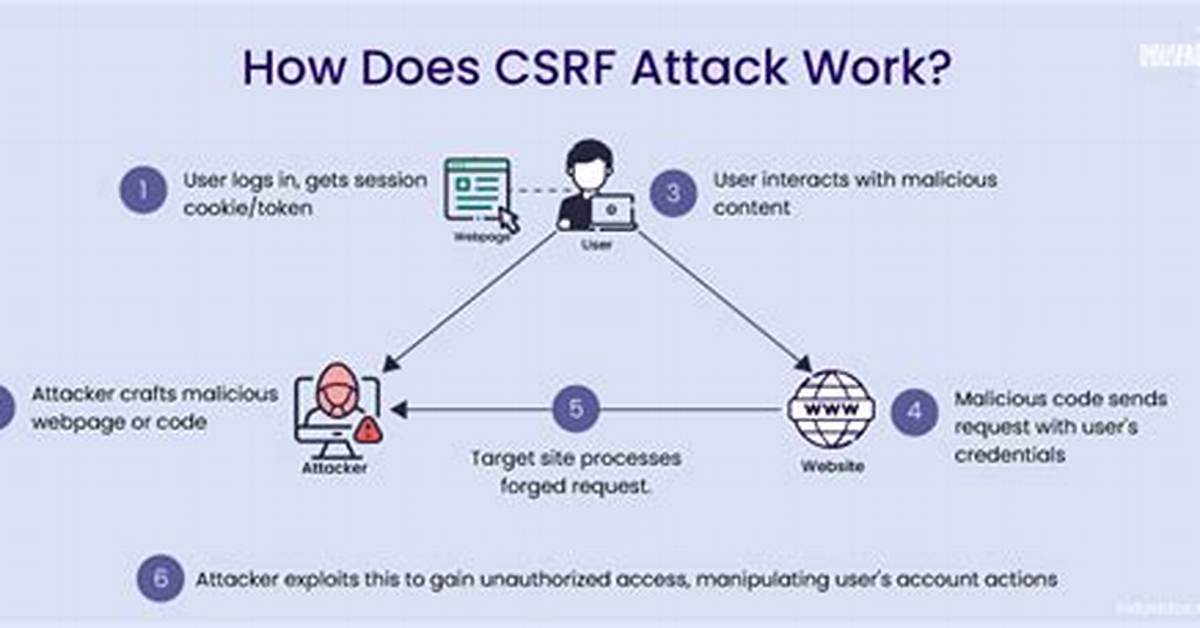
Server headers are generally easy for an attacker to manipulate. … However, a comparison of existing server headers does not provide sufficient protection against CSRF attacks, which is why a matching CSRF token is necessary. A CSRF token should be sent with every action that can result in a change of status.
Is CSRF protection needed?
Generally the answer is: Any form should be CSRF protected. Considering the minimal overhead csrf protection causes, I would really just use it. … It would be easier on your users to protect the sign up form. There are alternative methods that don’t need a token, such as a referrer or origin check:
Do we actually need to worry about CSRF attacks when SSL is used namely https with https dominating are CSRF attacks still common?
5 Answers. No, running a page on HTTPS does not protect it from CSRF. The fact that the communications between the browser and server is encrypted has no bearing on CSRF.

