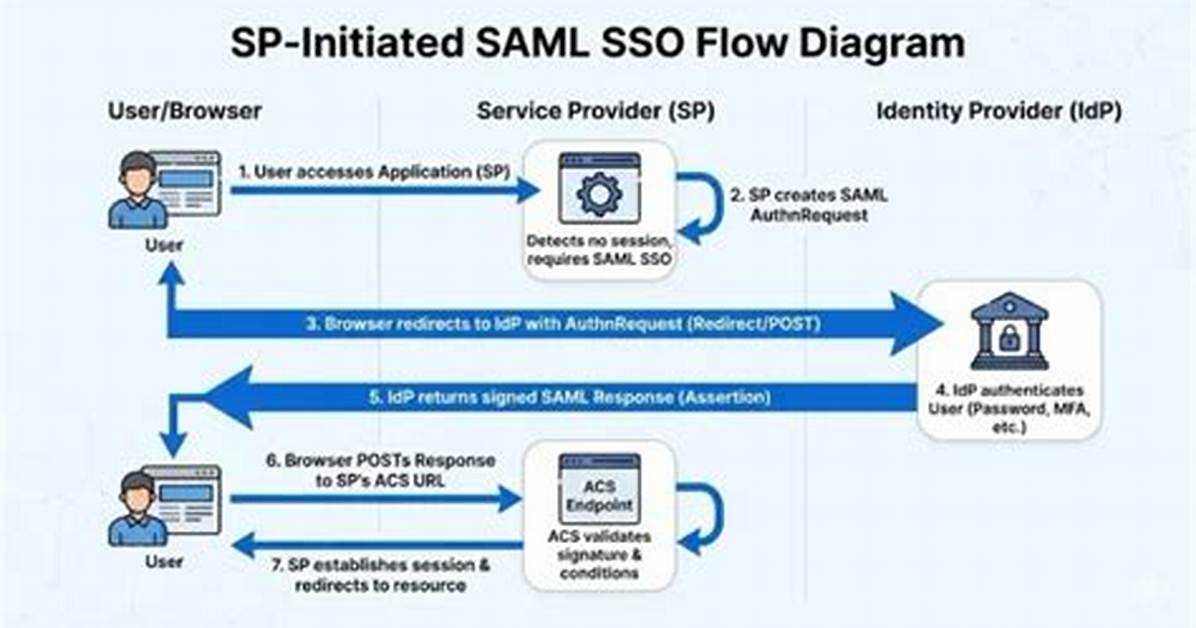
SAML works by passing information about users, logins, and attributes between the identity provider and service providers. Each user logs in once to Single Sign On with the identify provider, and then the identify provider can pass SAML attributes to the service provider when the user attempts to access those services.
Is SAML used in ADFS?
Active Directory Federation Services (ADFS) ADFS uses a claims-based access-control authorization model. This process involves authenticating users via cookies and Security Assertion Markup Language (SAML). That means ADFS is a type of Security Token Service, or STS.
How ADFS works step by step?
- The website requests an authentication token.
- User requests token from the ADFS server.
- ADFS server issues token containing user’s set of claims.
- User forwards token to the partner-company website.
- The website grants authorization access to the user.

