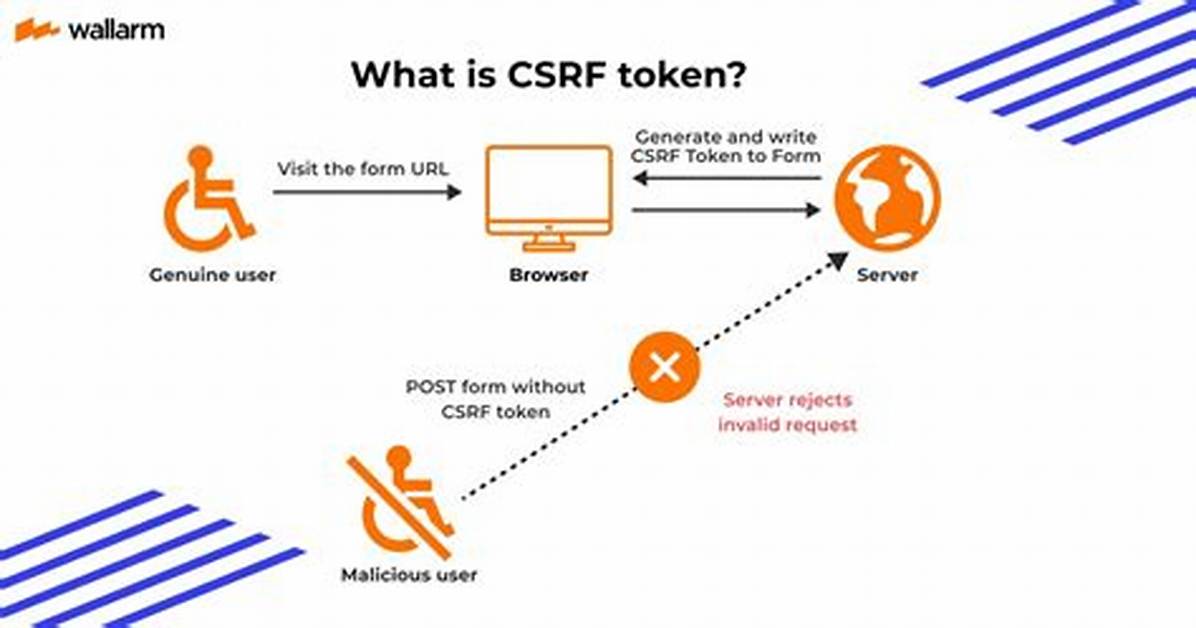
What are CSRF tokens? … CSRF tokens can prevent CSRF attacks by making it impossible for an attacker to construct a fully valid HTTP request suitable for feeding to a victim user.
What is the purpose of CSRF token?
A CSRF token is a secure random token (e.g., synchronizer token or challenge token) that is used to prevent CSRF attacks. The token needs to be unique per user session and should be of large random value to make it difficult to guess. A CSRF secure application assigns a unique CSRF token for every user session.
Why we use CSRF token in Django?
The CSRF token only ensures that only forms that have originated from trusted domains can be used to POST data back. So it doesn’t validate the data or how much data the form sends but if data comes from a form from a legit domain (your site usually). Hence the name: Cross Site Request Forgery protection.

