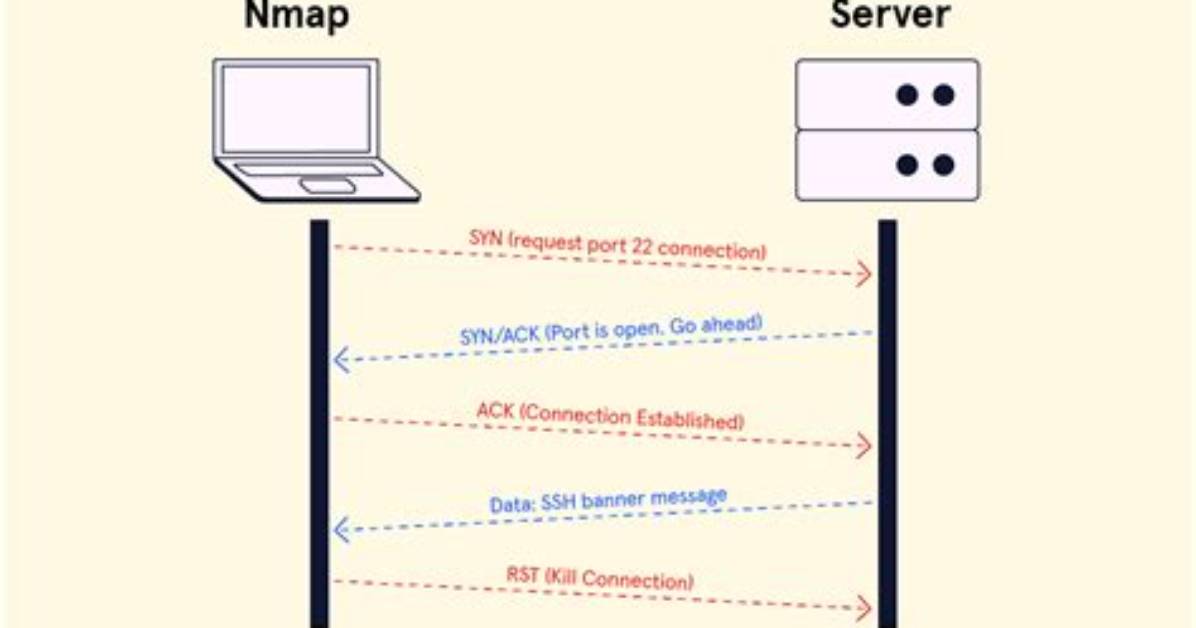
Nmap works by checking a network for hosts and services. Once found, the software platform sends information to those hosts and services which then respond. Nmap reads and interprets the response that comes back and uses the information to create a map of the network.
What does a port scan tell you?
A port scan is a method for determining which ports on a network are open. … Running a port scan on a network or server reveals which ports are open and listening (receiving information), as well as revealing the presence of security devices such as firewalls that are present between the sender and the target.
What port does Nmap use to scan?
If you specify the secure HTTPS protocol instead, the browser will try port 443 by default. Nmap works with two protocols that use ports: TCP and UDP. A connection for each protocol is uniquely identified by four elements: source and destination IP addresses and corresponding source and destination ports.

