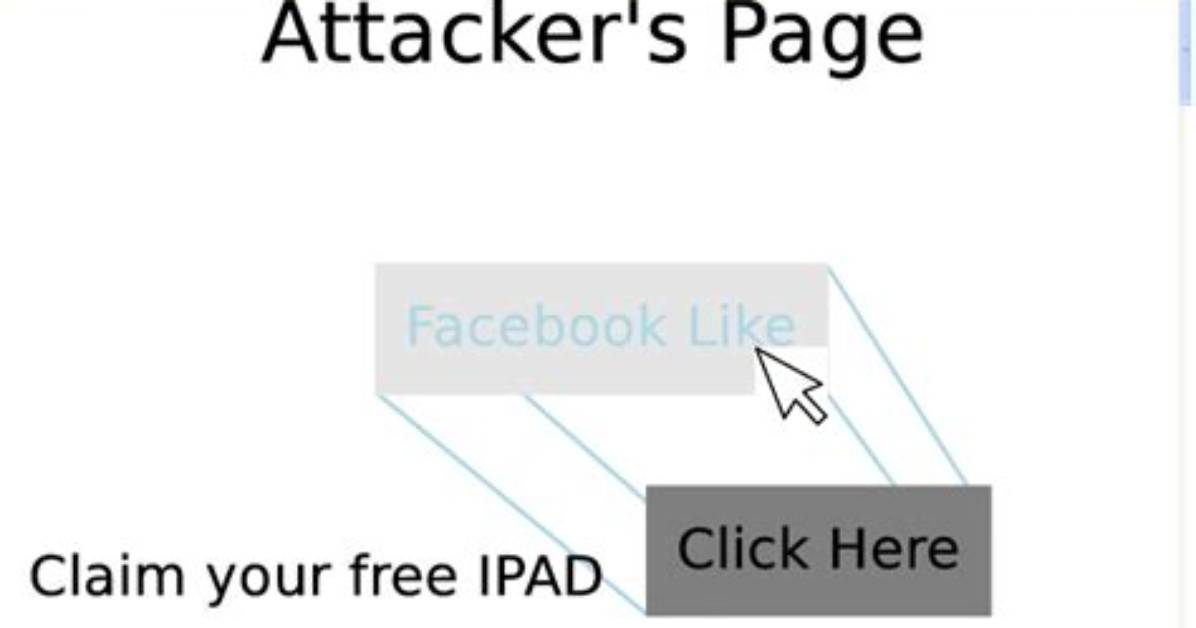
An iFrame injection is a very common cross-site scripting (or XSS) attack. It consists of one or more iFrame tags that have been inserted into a page or post’s content and typically downloads an executable program or conducts other actions that compromise the site visitors’ computers.
What is iframe hack?
The name Iframe Hacking has been derived from the manner in which the hacking is done using an iframe tag. … When anyone visits that page, the hidden iframe code secretly downloads and installs a Trojan or a malware such as key-logger on the unsuspecting user’s computer, if his computer is not adequately protected.
Is iframe a security risk?
Iframes Bring Security Risks. If you create an iframe, your site becomes vulnerable to cross-site attacks. You may get a submittable malicious web form, phishing your users’ personal data. … A malicious user can change the source site URL.

