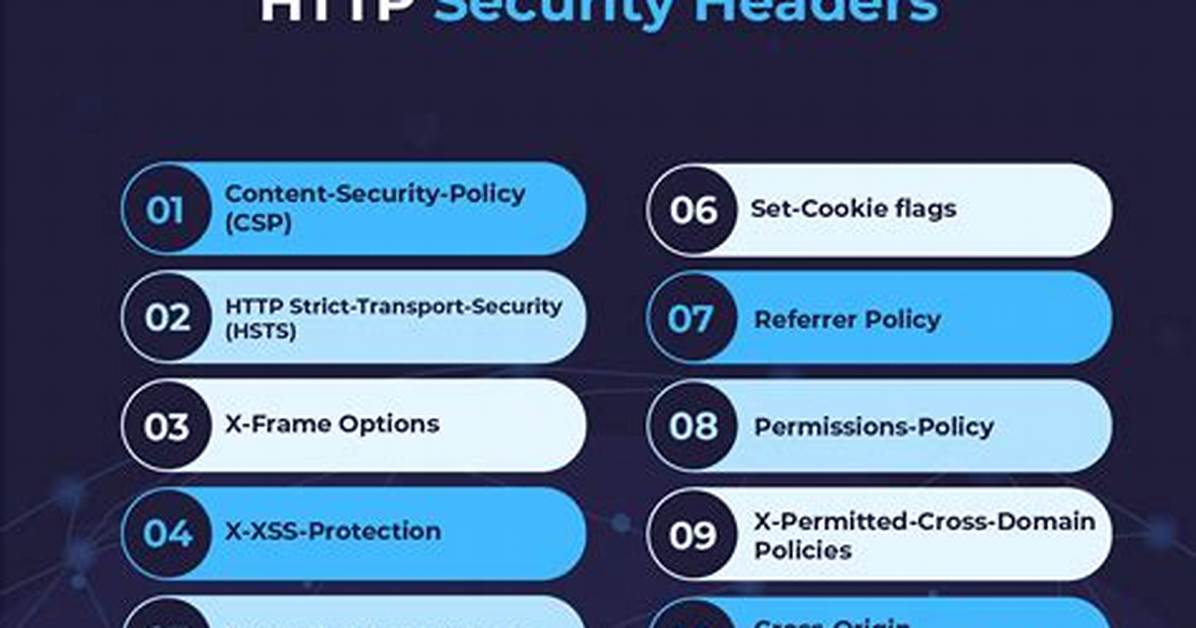
Security headers are directives used by web applications to configure security defenses in web browsers. Based on these directives, browsers can make it harder to exploit client-side vulnerabilities such as Cross-Site Scripting or Clickjacking.
Do security headers matter?
HTTP security headers are mostly useful for client side attacks like phishing, cross site scripting (XSS), or Man In The Middle (MITM). … That’s where security headers are important. The more you put efforts on client side security, the more that road will be safe to take.
What are some headers that add security?
- HTTP Strict Transport Security.
- X-Frame-Options.
- X-Content-Type-Options.
- Content Security Policy.
- X-Permitted-Cross-Domain-Policies.
- Referrer-Policy.
- Expect-CT.
- Permissions-Policy.

