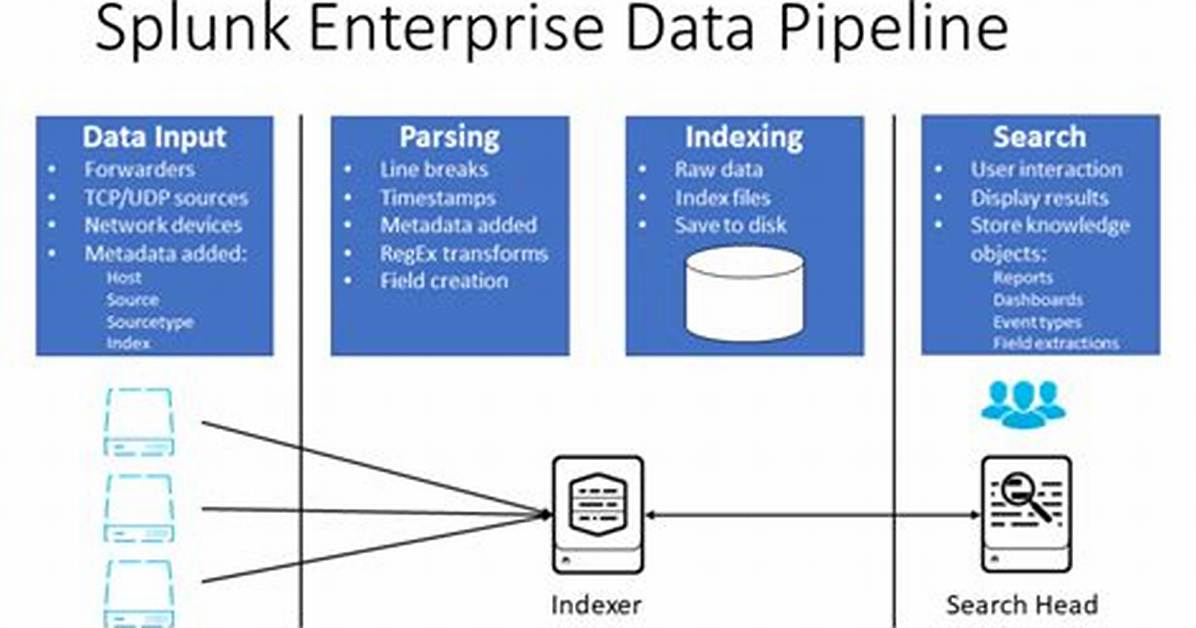
Splunk does not use any database to store its data, as it extensively makes use of its indexes to store the data but Splunk uses MongoDB to facilitate certain internal functionality like the kvstore. Splunk ingests the data from external sources like Universal forwarder etc.
Is Splunk a SQL database?
Splunk DB Connect is a generic SQL database extension for Splunk that enables easy integration of database information with Splunk queries and reports. … Use Splunk DB Connect’s Inputs to import structured data for powerful indexing, analysis, and visualization.
Does Splunk use NoSQL?
You can integrate Splunk with NoSQL and relational databases, and establish connections between your workflow tools and Splunk. Splunk also provides several methods for backing up large data sets to on-premise and S3-compatible storage.

