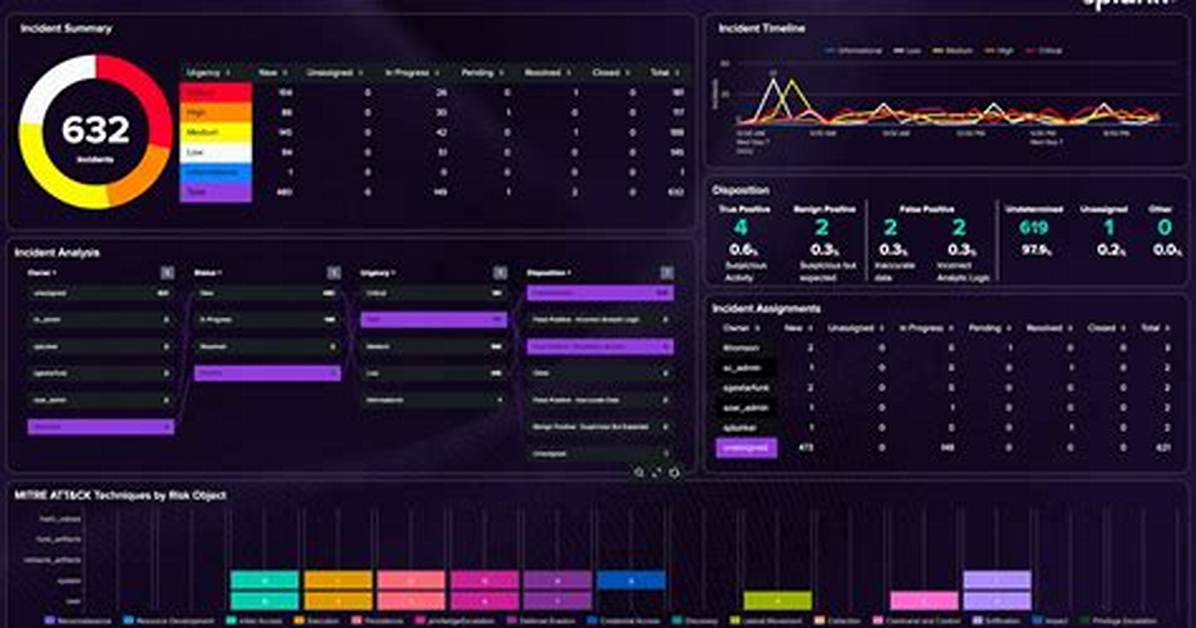
Splunk reports are results saved from a search action which can show statistics and visualizations of events. Reports can be run anytime, and they fetch fresh results each time they are run. The reports can be shared with other users and can be added to dashboards.
Is splunk a reporting tool?
Splunk is used for monitoring and searching through big data. It indexes and correlates information in a container that makes it searchable, and makes it possible to generate alerts, reports and visualizations.
What is Splunk process?
noun. The system process that handles indexing, searching, forwarding, and (as of Splunk Enterprise version 6.2) the Web interface that you log into Splunk Enterprise with. The process is a distributed C/C++ binary that accesses, processes, and indexes streaming data and handles search requests.

