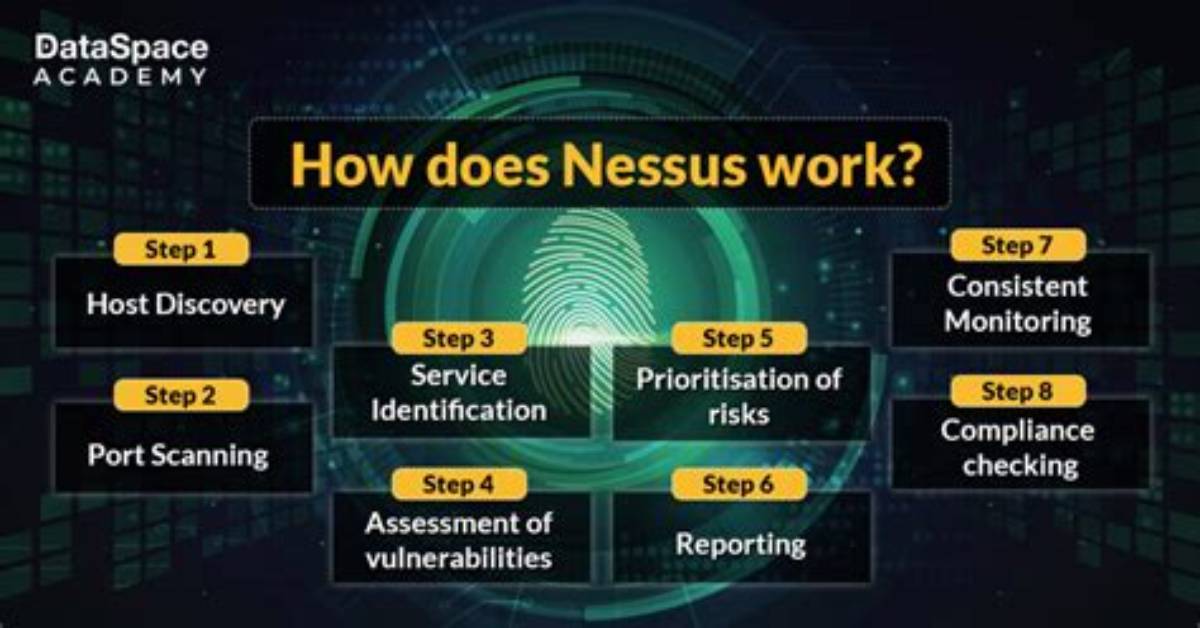
Nessus works by testing each port on a computer, determining what service it is running, and then testing this service to make sure there are no vulnerabilities in it that could be used by a hacker to carry out a malicious attack.
How do you use Nessus?
How To: Run Your First Vulnerability Scan with Nessus
- Step 1: Creating a Scan. Once you have installed and launched Nessus, you're ready to start scanning. ...
- Step 2: Choose a Scan Template. ...
- Step 3: Configure Scan Settings. ...
- Step 4: Viewing Your Results. ...
- Step 5: Reporting Your Results.
What types of vulnerabilities are scanned by Nessus?
Nessus can scan these vulnerabilities and exposures:
- Vulnerabilities that could allow unauthorized control or access to sensitive data on a system.
- Misconfiguration (e.g. open mail relay)
- Denials of service (Dos) vulnerabilities.
- Default passwords, a few common passwords, and blank/absent passwords on some system accounts.

