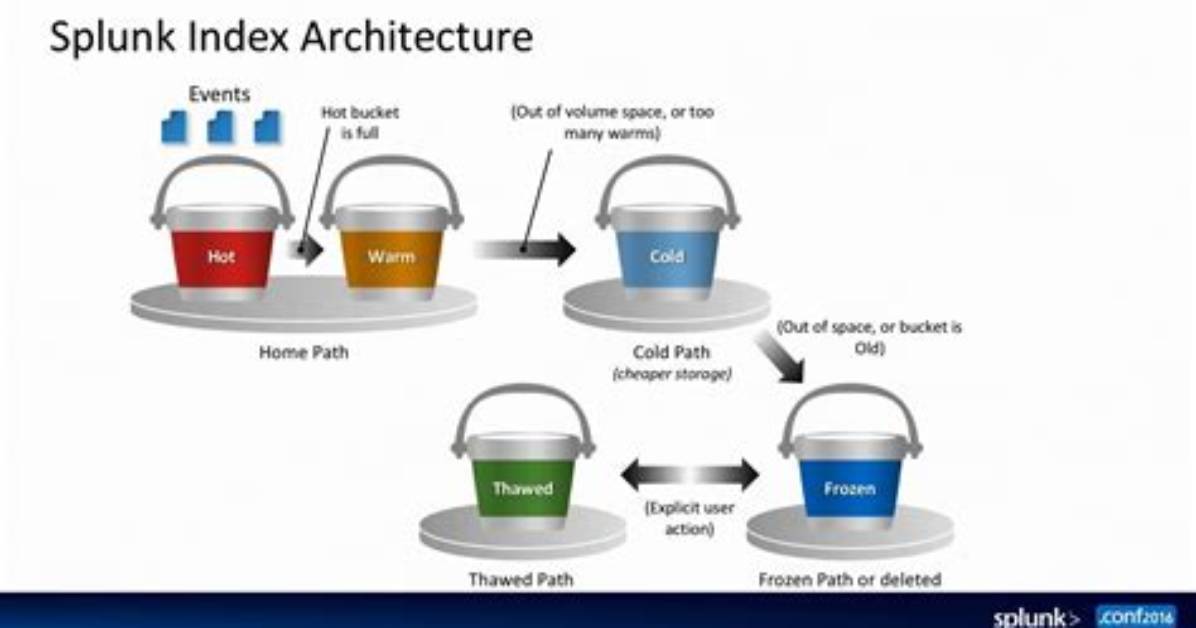
Splunk indexed data is located in database directories, divided into subdirectories called buckets. As time goes by, Splunk performs storage tiering, moving data through several types of buckets, which represent four tiers—hot, warm, cold and frozen.
Which directory is splunk bucket?
By default, your buckets are located in $SPLUNK_HOME/var/lib/splunk/defaultdb/db . You should see the hot-db there, and any warm buckets you have.
What is warm bucket Splunk?
Warm buckets
When a hot bucket reaches a size limit or gets restarted, it rolls on to become a warm bucket. The default location for a Warm bucket state is $SPLUNK_HOME/var/lib/splunk/defaultdb/db/*. Several other conditions can lead to a hot bucket rolling on to a warm bucket.

