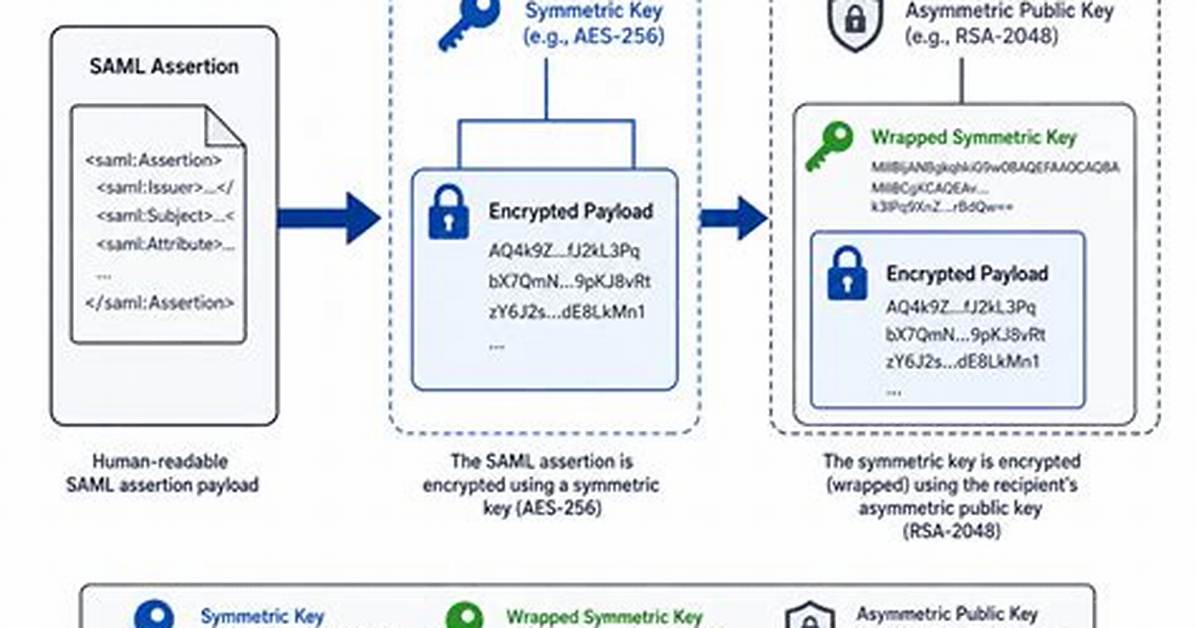
Encrypting the SAML assertion is optional. In most situations it isn't encrypted and privacy is provided at the transport layer using HTTPS. 2. It's an extra level of security that's enabled if the SAML assertion contains particularly sensitive user information or the environment dictates the need.
Do SAML assertions need to be encrypted?
Encryption of SAML assertions is disabled by default. Responses can be signed while carrying a signed encrypted Assertion, but the Response itself is not encrypted.
What is SAML assertion encryption?
SAML token encryption enables the use of encrypted SAML assertions with an application that supports it. When configured for an application, Azure AD will encrypt the SAML assertions it emits for that application using the public key obtained from a certificate stored in Azure AD.

