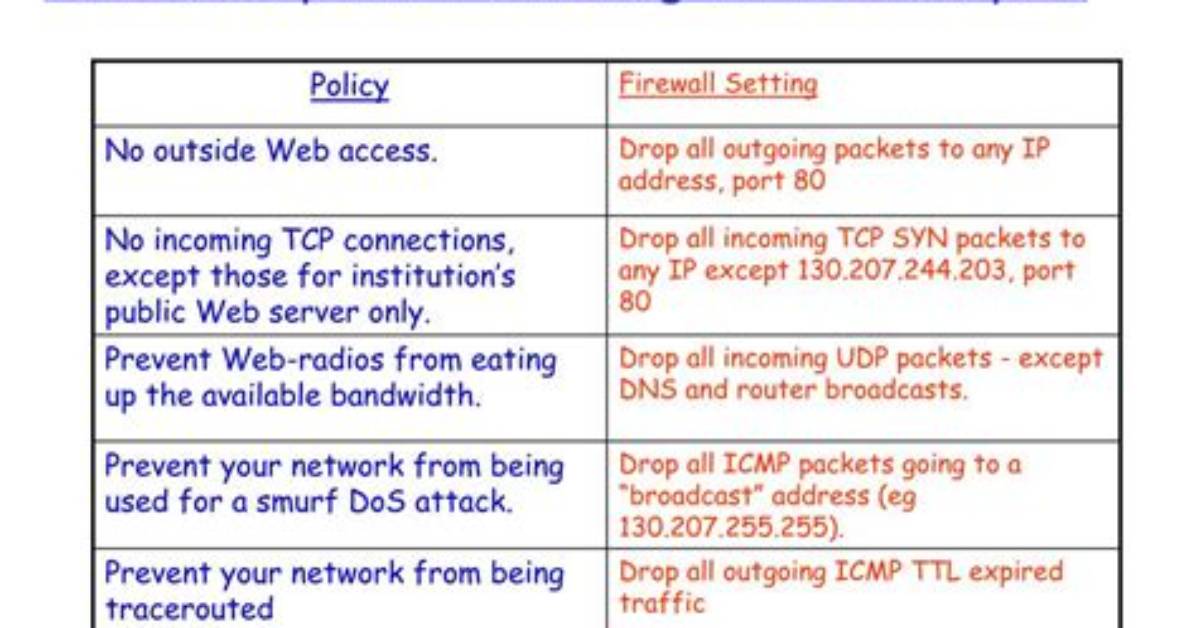
Stateless firewalls are designed to protect networks based on static information such as source and destination. Whereas
What is stateful and stateless filtering?
Stateful firewalls are capable of monitoring and detecting states of all traffic on a network to track and defend based on traffic patterns and flows. Stateless firewalls, however, only focus on individual packets, using preset rules to filter traffic.
What is difference between stateful and packet filtering?
Stateful packet inspection
While a packet filtering firewall only examines an individual packet out of context, a stateful firewall is able to watch the traffic over a given connection, generally defined by the source and destination IP addresses, the ports being used, and the already existing network traffic.

