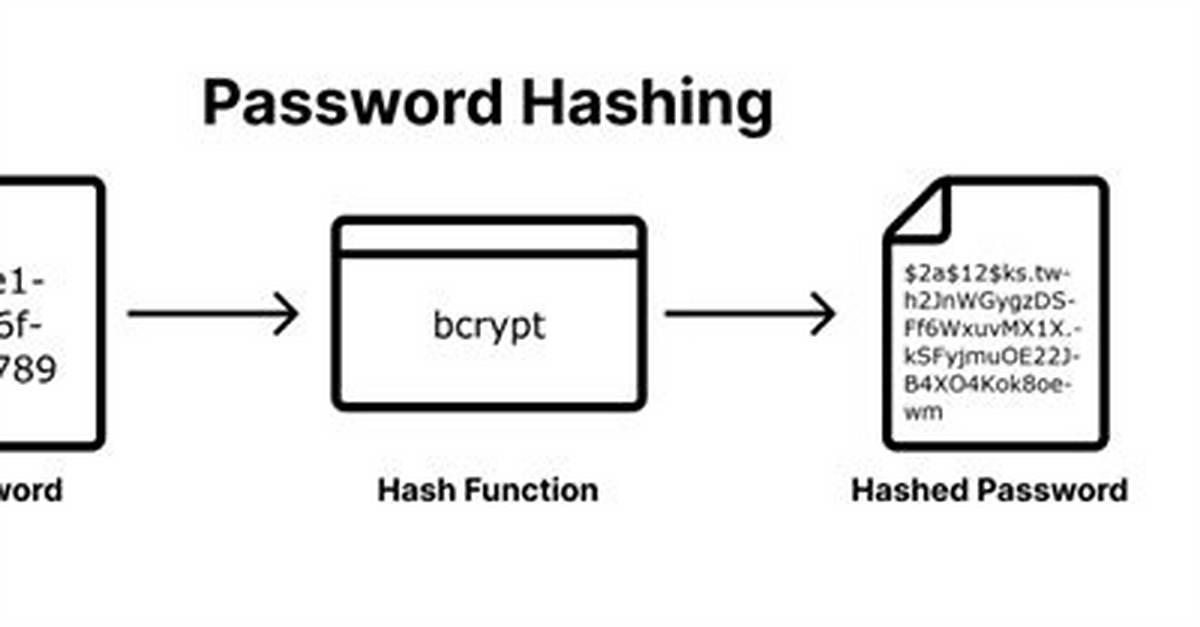
The problems present in traditional UNIX password hashes led naturally to a new password scheme which we call bcrypt, referring to the Blowfish encryption algorithm. Bcrypt uses a 128-bit salt and encrypts a 192-bit magic value. It takes advantage of the expensive key setup in eksblowfish.
Is bcrypt encrypted?
The bcrypt hash function is just that, a hash function. It does not perform encryption, it hashes. It's based on the Blowfish cipher, and is considered a good thing because you can make it slower over time. ... In regards to storing passwords on your site, you should be encrypting passwords before you hash them.
Can bcrypt be hacked?
With weak password hashing algorithms, what hackers will do is try millions, or billions of different combinations - as fast as their hardware allows for - and many easy passwords will fall quickly to rainbow tables / password crackers / dictionary-based attacks.

